Your Step-by-Step Guide to ISO 9001 Certification
Your practical roadmap to ISO 9001 certification and QMS setup
ISO 9001 sets the baseline for a quality management system (QMS) that helps organizations meet customer and regulatory requirements consistently while improving how work gets done. This guide gives a clear, step-by-step certification roadmap and practical instructions for implementing ISO 9001, preparing for audits, and maintaining certification. We break down common pain points — scoping, documented information, audit readiness, and continual improvement — into actionable steps and timelines so teams can move from gap analysis to certificate with less risk and wasted time. Read on to learn what ISO 9001 requires, how to build an effective QMS, what to expect from internal and external audits, and how to sustain certification through surveillance and re‑certification. We also cover how AI-assisted audit tools speed up gap analysis and planning, and we point to templates and controls you can use for document control, risk-based thinking, and performance evaluation.
What ISO 9001 is — and why certification matters
ISO 9001 is an international standard that specifies what a QMS must do to meet customer needs, ensure conformity and improve performance over time. The standard uses a process-based, risk-aware approach tied to leadership, context analysis, documented information and performance evaluation to produce consistent, auditable quality outcomes. Getting certified gives you third-party validation of your QMS — helping you win trust, access markets, and create a repeatable framework for continual improvement and operational efficiency. Organizations that adopt ISO 9001 also gain clearer process ownership, tighter document control and measurable indicators to drive corrective actions and management reviews. Below are the core business benefits to keep front of mind.
ISO 9001 drives measurable operational and market benefits:
- Market access and credibility: A certificate signals independent conformity and builds customer and partner confidence.
- Improved efficiency and lower costs: Formal process controls and nonconformity handling reduce rework and variation.
- Clear performance visibility: Objective metrics from audits and reviews enable data-driven improvement.
These advantages flow from the standard’s principles and clause structure, which show how a QMS should be designed to deliver those outcomes.
Key principles and core requirements
The standard rests on seven quality management principles: customer focus, leadership, engagement of people, process approach, improvement, evidence-based decision making and relationship management. These principles map across clauses 4–10 and guide governance, planning, support, operation, performance evaluation and improvement. For example, customer focus informs context and requirements, while the process approach requires documented inputs, outputs and performance indicators. In practice, applying the principles means creating a clear scope, defined roles, risk-based controls, measurable process metrics and documented evidence of competence and monitoring. Understanding that mapping helps teams prioritize implementation tasks and ensure audit evidence aligns with clause requirements.
Those same principles underpin risk-based thinking and performance evaluation — both essential for audit readiness and a sustainable QMS.
How to prepare for ISO 9001 certification
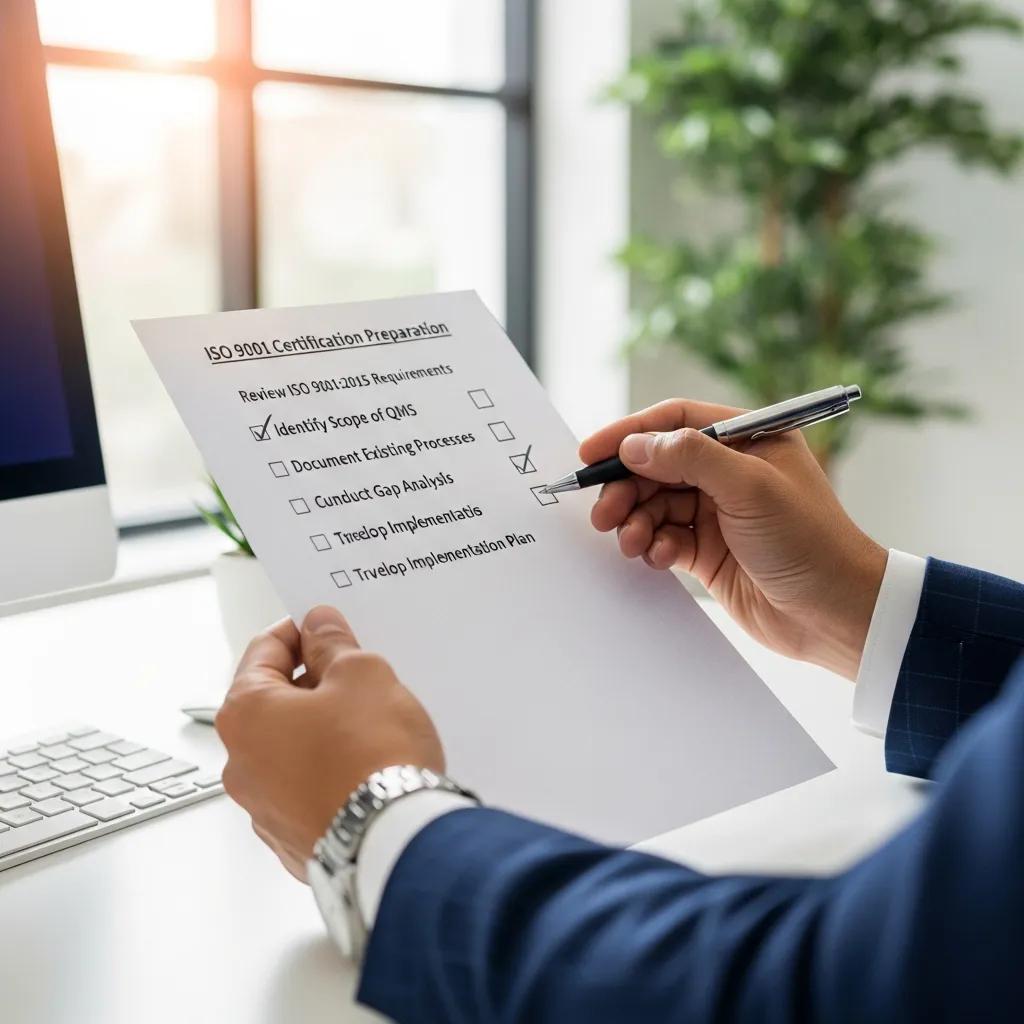
Preparation starts with leadership buy-in, a clearly defined QMS scope and a methodical gap analysis to identify what’s missing and how much work is required. You’ll also assign roles, secure resources, set a timeline, and capture baseline metrics. A focused preparation sequence helps teams prioritize high‑impact gaps, sequence documentation, and schedule internal audits before external assessment. Use the compact checklist below to move from scoping to readiness verification.
Follow this 6-step checklist to prepare for certification:
- Define scope and context: Record organizational boundaries, interested parties, products/services and the QMS scope.
- Secure leadership commitment: Get formal management support, allocate resources and nominate a QMS owner.
- Conduct a gap analysis: Compare current practices to ISO 9001 and prioritize corrective actions.
- Develop documented information: Produce core documents (policy, objectives, process maps, records) and controls.
- Run internal audits and management review: Confirm implementation, log nonconformities and close corrective actions.
- Schedule the external certification audit: Verify readiness and book Stage 1/Stage 2 assessments.
This checklist sets up implementation and leads into what a gap analysis should look like and how it shapes the plan.
What a gap analysis does and how it reveals compliance needs
A gap analysis compares your current processes, documents and evidence against ISO 9001 requirements to reveal missing or weak controls. Typical activities include document review, process walkthroughs, staff interviews, evidence mapping and a scored risk assessment. The deliverable is a prioritized remediation roadmap with estimated resources, timelines and owners for corrective actions. Findings and effort vary by organization size; the short comparison below helps set realistic expectations and allocate resources.
The gap analysis report then feeds the project plan and training priorities you’ll use during implementation and internal audits.
Comparison of typical gap findings and remediation effort by organization type:
| Organization Type | Typical Top Findings | Typical Remediation Effort |
|---|---|---|
| Small/SME | Few documented procedures, informal record control, limited KPIs | 4–8 weeks — focused documentation and training |
| Mid-size | Partial process maps, inconsistent risk assessments, incomplete metrics | 8–16 weeks — cross-functional alignment work |
| Enterprise | Cross-site integration gaps, complex supplier controls, siloed data | 12–24+ weeks — stakeholder coordination and system changes |
Use this as a planning guide: smaller organizations can close priority gaps quickly, while larger enterprises should budget for longer, cross-functional programs to harmonize processes and evidence.
How to implement an effective QMS for ISO 9001
Turn your gap analysis into prioritized projects: document creation, process mapping, risk controls, competence management and performance metrics. Work by process — define inputs, activities, outputs, owners and indicators for each critical flow so auditors can see how things actually operate. Enforce document control (versioning, approvals, retention and access) so evidence is traceable. Set objectives, monitoring systems, internal audit schedules and management review cadences to create a repeatable control loop for continual improvement and compliance.
Next, we’ll look at the documented information you need and how to structure it for audit readiness.
Required documents and practical procedures
At minimum, auditors will expect the quality policy and objectives, scope statement, process descriptions, records of competence and training, internal audit reports, corrective action records and management review outputs. Helpful supporting materials include process maps, work instructions, supplier evaluations and risk registers. Follow document control best practices: unique IDs, revision history, approvals and retention rules so documents remain current and auditable. Keep documentation concise, process-focused and tied to measurable objectives so auditors can trace inputs to outputs and see continual improvement in action.
Research underscores how controlled, maintained documented information supports QMS operations and ensures processes are carried out as intended.
ISO 9001:2015 — Documented information for an effective QMS
This paper explains the documents needed to set up a Quality Management System under ISO 9001:2015. The standard treats documented information as the evidence an organization must control and maintain to operate processes reliably and show they work as planned. It covers both documents required by the standard and any additional records the organization needs for system effectiveness.
From documented procedure to documented information: The new approach of ISO 9001: 2015, L Borsacchi, 2015
After you capture processes and records, make sure people are competent and aware of QMS responsibilities so you can demonstrate effective implementation during audits.
Core documented information — purpose and what to include:
| Document | Purpose | Typical Contents |
|---|---|---|
| Quality Policy | State the organisation’s commitment to quality and direction | Commitment statement, customer focus, high-level objectives |
| Quality Objectives | Set measurable targets to drive improvement | KPIs, targets, owners, review cadence |
| Process Descriptions | Describe how key processes work in practice | Inputs/outputs, process owner, controls, interfaces |
Prioritise the quality policy and objectives first, then create process descriptions and records that show consistent operation and measurement.
Managing training and awareness for QMS success
Identify competence needs for each role, build a training plan and keep a living training matrix that records training, qualifications and evidence of competence. Evidence can be certificates, assessments, on-the-job evaluations or shadowing records; auditors will expect to see the link between roles and competence. Reinforce awareness with briefings, team meetings and visible reminders, and capture attendance or minutes as evidence. Reviewing the training matrix during management review keeps competence gaps visible and prompts development actions.
Strong staff awareness and competence improve internal audit quality and overall QMS performance.
Auditing steps for ISO 9001 certification
The audit path includes internal audit cycles, management review, pre-certification checks, and the certification body’s Stage 1 and Stage 2 audits, followed by surveillance audits. Internal audits verify conformity, surface findings and drive corrective actions; management review evaluates results and prioritises resources. External certification begins with Stage 1 (document review and readiness) and continues with Stage 2 (on-site verification across the scope). After certification, surveillance audits — typically annual — keep the QMS under review, and re‑certification normally happens on a three-year cycle.
Quick reference sequence for internal and external audits:
- Plan and run internal audits: define scope, sample, collect evidence and log findings.
- Management review: assess audit outcomes, objectives, resourcing and decisions.
- Stage 1 audit: certification body reviews documents and readiness.
- Stage 2 audit: on-site verification of implementation and objective evidence.
- Certification decision and surveillance: ongoing checks and closure of corrective actions.
This flow explains the audit stages and sets up deeper guidance on internal audit practice and external assessment expectations.
How internal audits are carried out
Internal audits start with a programme that defines scope, objectives and criteria mapped to QMS processes and clauses. Auditors collect objective evidence through document review, interviews, observation and record sampling; findings are logged as conformities, opportunities for improvement or nonconformities, each supported by evidence and suggested actions. Nonconformities should include clear descriptions, root-cause notes and corrective action plans with owners and deadlines; follow-up audits must verify closure. A strong internal audit function uncovers issues early and improves readiness for external assessment.
Internal audits also feed management review and drive continual improvement across the QMS.
Audit type comparison:
| Audit Type | Objective | Typical Duration & Output |
|---|---|---|
| Internal Audit | Confirm process conformity and effectiveness | 1–5 days per scope; findings report and corrective actions |
| Stage 1 Audit | Document review and readiness assessment | 0.5–1 day; readiness report and reviewer notes |
| Stage 2 Audit | On-site verification of implementation | 1–5 days; nonconformities report and certification decision |
In short: internal audits find issues early, Stage 1 confirms readiness and Stage 2 verifies implementation for certification.
What happens during the external certification audit?
Stage 1 auditors review your documented information to confirm scope, policy, objectives and general readiness; they usually list areas to address before Stage 2. Stage 2 auditors perform an on-site check: sampling processes, reviewing records, watching activities and interviewing staff to confirm the QMS is implemented and maintained. Findings are classed as major or minor depending on severity and systemic impact — a major nonconformity typically blocks certification until fixed and verified, while minor ones require documented corrective action and closure evidence. Once Stage 2 is passed and any findings are closed, the certification body issues the certificate and schedules surveillance audits to monitor ongoing compliance.
Knowing these differences helps you prepare staff and evidence for the types of sampling and checks auditors will use.
How to achieve and keep ISO 9001 certification
To achieve certification you must close priority gaps, pass the Stage 2 verification and receive the certification decision. To maintain it, plan for surveillance audits, document continual improvement actions and run regular management reviews. Surveillance audits (usually annual) check ongoing conformity and the effectiveness of corrective actions. Management review should routinely assess objectives, audit results, customer feedback and resource needs to drive improvements. Continual improvement follows the Plan‑Do‑Check‑Act cycle: use audit data, complaints and metrics to target corrective and preventive actions and measure their impact.
This iterative approach is central to ISO 9001; many implementation guides structure work around the PDCA model.
ISO 9001 implementation and the PDCA model
This guideline links ISO 9001 requirements with implementation steps following the Plan‑Do‑Check‑Act model, including considerations for Industry 4.0 technologies where relevant.
Integrating ISO 9001 and Industry 4.0.
An implementation guideline and PDCA model for manufacturing sector, A Chiarini, 2023
Re‑certification (typically every three years) requires you to pull together surveillance reports, records of closed corrective actions and up‑to‑date documented information for the re‑assessment.
Key ongoing activities to plan and schedule:
- Surveillance: keep audit schedules up to date and close findings promptly.
- Management reviews: use metrics and audit outputs to set improvement priorities.
- Re‑certification prep: consolidate surveillance records and resolve systemic issues ahead of reassessment.
These activities prepare you for re‑certification and define the evidence auditors expect when renewing a certificate.
Management review and continual improvement — why they matter
Management review is where top leadership evaluates QMS performance, audits, customer feedback, objective progress and resourcing, then decides on actions to improve suitability, adequacy and effectiveness. Typical inputs include internal and external audit results, process performance data, nonconformities and corrective action status; outputs are decisions and actions with owners and timelines. Continual improvement uses those outputs to implement targeted changes — process updates, training, supplier actions or system upgrades — and measures impact through KPIs. Demonstrating regular, evidence‑based management reviews and resulting improvements is vital for auditors to see the QMS is active and evolving.
Well-documented management reviews close the loop between findings and sustained QMS improvement, supporting long-term certification success.
Re‑certification: timing and common pitfalls
Re‑certification usually occurs every three years and involves a full reassessment similar to the initial Stage 2 audit to confirm continued conformity across your scope. Prepare by compiling surveillance audit reports, records of closed corrective actions, updated documented information and evidence of continual improvement over the certification cycle. Start planning early to address outstanding systemic issues, ensure internal audits have been completed and verify KPIs show maintained or improved performance. Common pitfalls include incomplete corrective-action evidence, fragmented records across sites and weak management review documentation; proactive scheduling and record consolidation reduce these risks.
Thorough preparation preserves market access and the credibility a valid ISO 9001 certificate provides.
If you want to speed up assessments and reduce time to certification, consider modern audit technology and external expertise to help focus effort and close gaps faster.
Stratlane Certification is an accredited certification body offering ISO 9001 services across Europe and the UK. We can issue certificates in over 27 countries and work with professional auditors in 29+ countries; our certificates are recognised by corporate and academic stakeholders. Our service model uses AI‑assisted auditing to streamline gap analysis and audit planning while maintaining full conformity assessment. If you’re ready to accelerate readiness, request an AI‑assisted gap analysis or ask for a tailored quote from Stratlane Certification to see timelines and resource estimates for your scope.
Next, we explain how AI‑driven auditing changes the certification process and what measurable benefits it delivers.
How Stratlane’s AI‑driven auditing speeds up ISO 9001 certification
Our AI‑driven auditing blends automated evidence mapping, risk scoring and audit plan optimisation to cut manual work in gap analysis and focus auditor time on the highest‑risk areas that affect certification readiness. The tools ingest documented information, flag missing controls and correlate evidence across processes to prioritise remediation and produce clearer remediation roadmaps. AI also helps optimise audit schedules by predicting where findings are most likely, improving sampling efficiency and reducing on‑site days. For organisations that value speed and accuracy, AI‑assisted audits shorten certification timelines and lower administrative overhead while preserving accredited conformity assessment.
Concrete AI benefits and short examples of typical gains:
- Faster identification of compliance gaps through automated document analysis and pattern recognition.
- Risk scoring and prioritisation so teams tackle high‑impact items first.
- Reduced time‑to‑certification by optimising auditor workloads and scheduling.
AI amplifies auditor expertise rather than replacing it — directing human effort where it has the most impact.
Benefits of AI‑powered gap analysis and audit planning
AI accelerates baseline assessments by scanning documented information and highlighting mismatches with ISO 9001 clauses, cutting initial assessment time and producing prioritized remediation lists. Risk algorithms assign severity and likelihood to findings so you can address high‑risk issues first, often shortening implementation timelines and lowering remediation costs. AI‑driven audit planning aligns auditor skills to the risk profile, improving sampling efficiency and targeting process weak points that matter most for certification. The short comparison below shows typical differences between manual and AI‑assisted approaches.
Comparison — manual vs AI‑assisted gap analysis:
| Approach | Time to Baseline | Prioritization | Typical Outcome |
|---|---|---|---|
| Manual Gap Analysis | Weeks | Reviewer dependent; subjective | Broad checklist, mixed priorities |
| AI-Assisted Analysis | Days | Risk‑scored and prioritized | Actionable remediation roadmap |
In short: AI‑assisted analysis reduces assessment time and delivers a higher‑fidelity, prioritized roadmap so teams focus on what drives certification.
How AI improves audit efficiency, accuracy and cost effectiveness
AI handles repetitive evidence‑mapping tasks so auditors spend more time on interviews, observations and root‑cause analysis where human judgment is essential. Accuracy improves because algorithms spot patterns and omissions across large document sets and historical audit data that manual review can miss. Cost savings come from shorter on‑site days, fewer repeat visits and less administrative work for both client and auditor, reducing total audit hours for certification or surveillance. Typical improvements include automated cross‑referencing of records, smarter sample selection for higher‑probability nonconformities and clearer evidence trails for management review.
Combining AI with experienced auditors preserves conformity assurance while streamlining resources and timelines.
If you’re ready to leverage these efficiencies, Stratlane Certification offers AI‑driven gap analysis and audit planning as part of our ISO 9001 services — available by quote or initial assessment booking.
Frequently Asked Questions
What does ISO 9001 certification cost?
Costs vary by organisation size, process complexity and the certification body you choose. Typical expenses include certification audit fees, internal training, documentation work and any consultancy support. You should also budget for implementation changes required to meet the standard. For small and medium businesses, total costs commonly range from a few thousand to tens of thousands of dollars depending on scope and support needs.
How long does the certification process take?
Timeframes depend on your starting point and operational complexity. A realistic timeline is three to six months from preparation through internal audits to certification for many organisations. Teams with an established QMS can move faster; organisations starting from scratch should allow extra time for documentation and process changes. Plan resources and milestones to keep the project on track.
What common challenges arise during certification?
Typical challenges include resistance to change, weak management engagement and limited understanding of the standard’s requirements. Poorly defined processes and incomplete documentation also slow progress, as does inconsistent cross‑team communication. Overcome these by securing leadership support, running targeted training, and creating clear, achievable milestones that keep teams aligned.
How can organisations stay compliant after certification?
Ongoing compliance requires regular internal audits, timely corrective actions, structured management reviews and a culture of continuous improvement. Plan surveillance audits, maintain documentation, track KPIs and address nonconformities promptly. Engaging staff in quality practices and keeping improvement visible are key to sustained compliance.
How important is employee involvement?
Employee engagement is essential. When people understand their role in the QMS and see how it ties to objectives, they take ownership and contribute practical improvements. Training, clear role descriptions and channels for feedback help embed quality into daily work and improve overall system performance.
Is ISO 9001 useful for small businesses?
Yes. ISO 9001 helps small businesses put repeatable processes in place, reduce waste, and increase customer confidence. Certification can open doors to new customers and contracts while improving internal control and efficiency. The investment often pays back through reduced errors and stronger market positioning.
Conclusion
ISO 9001 certification gives you a clear framework to strengthen quality management, boost operational efficiency and build customer confidence. Follow the steps in this guide and consider AI‑assisted tools to speed readiness and reduce manual effort. If you’d like help, our team can guide you through every stage — from gap analysis to certification and beyond. Start your ISO 9001 journey today and explore how our services can help you reach certification faster and keep it working for your business.