Enhance Data Privacy: Key Advantages of ISO 27001:2022
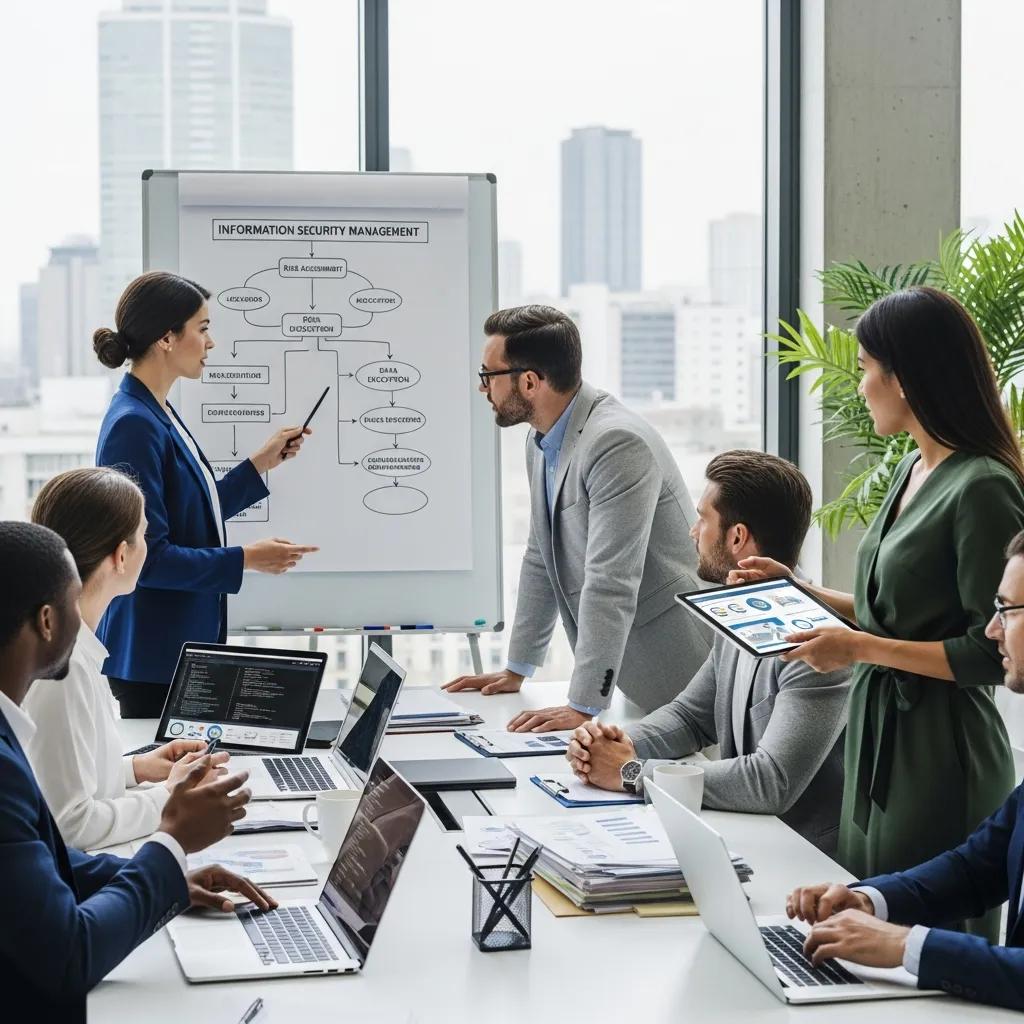
ISO 27001:2022 — How Certification Strengthens Security, Compliance, and Efficiency
ISO 27001:2022 defines a repeatable Information Security Management System (ISMS) that helps organisations protect information assets, reduce risk, and meet legal and contractual obligations. This guide explains how the standard tightens security, supports data-privacy compliance, and drives operational efficiency. You’ll find practical risk-management steps, mappings to regulations like GDPR and NIS2, an overview of cost and ROI considerations, and how AI-augmented auditing can speed certification. The focus stays on ISO 27001:2022 benefits, core ISMS elements (policies, controls, continuous improvement), and implementation priorities for decision-makers. Later sections cover what ISO 27001:2022 is, regulatory alignments, cybersecurity advantages, operational and cost benefits, market differentiation, and how Stratlane Certification’s AI-enabled audits shorten and strengthen the certification path.
What is ISO 27001:2022 and How Does It Strengthen Information Security?
ISO 27001:2022 is the international standard that sets requirements for creating, operating, maintaining, and improving an Information Security Management System. It strengthens security by forcing organisations to identify critical information assets, assess risks, implement appropriate Annex A controls, and maintain governance and continual improvement cycles that protect confidentiality, integrity, and availability. The ISMS model relies on documented policies, clear roles and responsibilities, and evidence-based audits, so security moves from ad hoc fixes to measurable, auditable practice. That framework converts routine security work into measurable risk reduction — a useful lens when we break down the ISMS components.
What Defines an Information Security Management System?
An ISMS is a coordinated system of policies, procedures, processes, and controls that manages information risks across an organisation. Core elements include security policies, an asset inventory, risk assessment and treatment plans, Annex A control implementations, written procedures, staff training, and internal audits. The ISMS follows the Plan–Do–Check–Act (PDCA) cycle to embed continual improvement through surveillance audits and management reviews. This structure ties governance to practical controls and ensures security choices reflect the organisation’s risk appetite and business goals — setting the stage for the 2022 updates.
What Are the Key Updates in the 2022 Version of ISO 27001?
The 2022 update revises Annex A control groupings and clarifies controls to better reflect modern tech and the current threat landscape, improving alignment with cloud services, AI systems, and privacy needs. Structural refinements emphasise asset lifecycle management, monitoring, and supplier relationships, and they make it easier to map ISO 27001 to related standards like ISO 27701. Organisations should review existing ISMS documentation against the updated control set and plan a transition that prioritises high-risk assets and cloud/AI governance gaps. Thoughtful transition planning keeps risk treatments aligned with updated controls and preserves the certification’s real-world value.
How Does ISO 27001:2022 Certification Improve Data Privacy and Regulatory Compliance?
ISO 27001:2022 supports data privacy and regulatory compliance by formalising an ISMS that aligns security controls with legal obligations and data-protection principles. The standard helps organisations apply data-protection-by-design, implement access controls and encryption, and maintain audit trails that support GDPR, HIPAA, CCPA, NIS2, and other sector rules. By documenting risk assessments, a Statement of Applicability (SoA), and procedures, ISO 27001:2022 makes it simpler to show compliance during audits and regulatory reviews. The table below links major regulations to ISO features and concrete benefits you can act on.
| Regulation | ISO 27001 Feature | Practical Benefit |
|---|---|---|
| GDPR | Data-protection by design, access controls, DPIA alignment | Clear technical and organisational measures to support lawful processing |
| HIPAA | Risk assessment, access control, logging and audit trails | Stronger PHI protections and improved audit readiness |
| NIS2 | Incident response, supplier security, governance | Better operational resilience and reporting for essential services |
| DORA (financial sector) | Third-party risk management, continuity planning | Improved vendor oversight and ICT resilience for financial services |
| CCPA | Data inventory, subject access procedures | Faster, more reliable responses to consumer data requests |
These mappings show how ISO 27001’s outputs support privacy obligations and establish a defensible compliance posture. Next, we explain how the ISMS risk-management process turns those mappings into operational activity.
Which Data Privacy Regulations Does ISO 27001:2022 Support?
ISO 27001:2022 underpins a wide range of privacy and sector-specific rules by formalising controls and management processes that reflect common legal principles such as minimisation, purpose limitation, and accountability. For GDPR, it helps with privacy-by-design and documenting processing activities; for HIPAA, it enforces technical safeguards like access controls and audit logging for PHI; for CCPA, it supports inventories and subject-access workflows. The standard also offers governance elements useful for NIS2 and DORA where operational resilience and third-party oversight matter. Mapping regulatory needs to ISMS outputs simplifies audits and evidence-gathering for regulators.
How Does ISO 27001:2022 Facilitate Effective Risk Management?
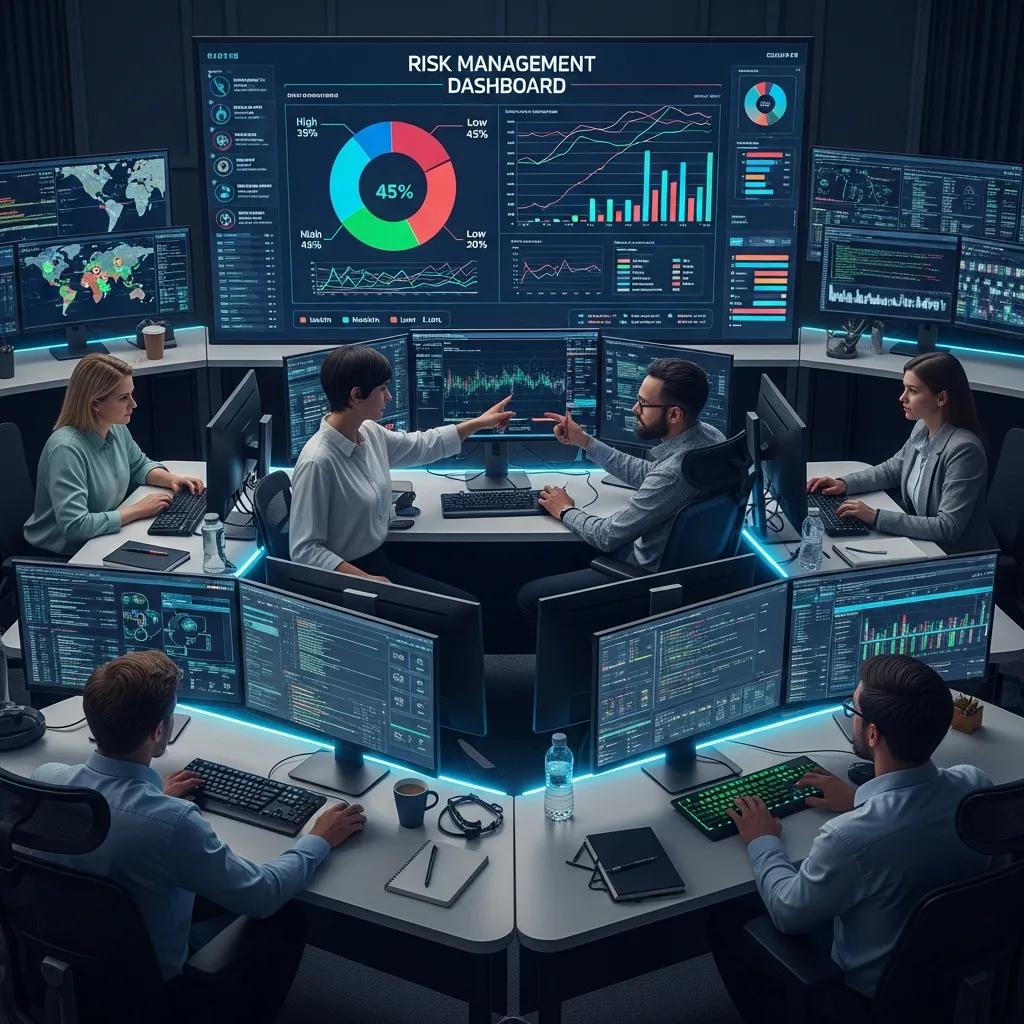
ISO 27001:2022 prescribes a risk-based process: identify assets, assess threats and vulnerabilities, evaluate likelihood and impact, and select risk treatments recorded in the SoA. This produces practical outputs — risk registers, treatment plans, and KPIs — that tie control investments to residual risk and organisational targets. Continuous monitoring, periodic reassessment, and surveillance audits ensure the ISMS adapts to changing threats and stays aligned with compliance needs. Bringing risk management into day-to-day processes yields measurable security improvements and lets teams prioritise remediation where it matters most.
What Cybersecurity Advantages Does ISO 27001:2022 Provide to Businesses?
ISO 27001:2022 delivers practical cybersecurity benefits by formalising detection, response, and prevention through documented controls, monitoring, and governance. The standard supports integration with tools like SIEMs, requires incident-response playbooks, and encourages continuous improvement via post-incident reviews and internal audits. Operational governance helps organisations reduce mean time to detect and respond, lower the risk of major breaches, and tighten oversight of cloud and AI deployments. The table below summarises key cybersecurity benefits, the mechanisms that deliver them, and the business impacts you can measure.
| Benefit | Mechanism | Business Impact |
|---|---|---|
| Improved detection | Centralised logging, SIEM integration, monitoring controls | Faster detection and reduced attacker dwell time |
| Streamlined response | Formal incident playbooks, defined roles, forensic readiness | Lower recovery costs and shorter service interruptions |
| Supply chain security | Supplier assessments, contractual controls, continuous monitoring | Reduced third-party breach risk and smoother procurement |
This clarifies how ISO controls create measurable cybersecurity outcomes. We’ll next look deeper at incident detection and response, followed by cloud and AI-specific considerations.
It’s also worth noting how AI-driven audit tools can complement security teams by improving audit coverage and speeding evidence collection — a practical innovation for modern ISMS programs.
How Does ISO 27001:2022 Enhance Cyber Threat Detection and Incident Response?
The standard improves detection and response by requiring documented incident procedures, clear roles and responsibilities, and logging and monitoring that feed detection platforms. Organisations adopt incident playbooks, escalation matrices, and tabletop exercises to validate readiness and refine cross-functional workflows involving IT, legal, and communications. Forensic readiness and evidence preservation are formalised to support root-cause analysis and reduce recurrence. Post-incident reviews then feed improvements back into the ISMS to strengthen controls and targeted monitoring.
What Role Does ISO 27001:2022 Play in Cloud and AI Security?
ISO 27001:2022 applies directly to cloud and AI environments by requiring controls that address shared responsibility models, data classification, and model governance. It ensures protections for data in transit and at rest, enforces supplier and change management for cloud and AI providers, and sets monitoring and access controls to limit model misuse and data leakage. Aligning ISO 27001 with ISO 27701 and keeping an eye on emerging AI regulation helps organisations build accountability across cloud and AI stacks and improve resilience for sensitive applications.
Research increasingly highlights the value of integrating ISO 27001:2022 with AI management frameworks such as ISO/IEC 42001:2023 to strengthen ethical, reliable AI governance alongside information security controls.
ISO 27001:2022 & AI Management System Integration
This study reviews how adopting ISO/IEC 42001:2023 — an AI management-system standard — complements ISO/IEC 27001:2022 by addressing the governance, fairness, transparency and reliability of AI systems. It outlines practical benefits across data security, operational efficiency, regulatory alignment and competitive advantage, and discusses integration patterns that let organisations manage AI risks alongside information-security obligations.
Exploring the Impact of ISO/IEC 42001:2023 AI Management Standard on Organizational Practices, S. Biroğul, 2023
How Can ISO 27001:2022 Certification Drive Operational Efficiency and Cost Savings?
ISO 27001:2022 certification drives efficiency and cost savings by standardising processes, eliminating duplicated controls, and reducing incident-related expenses. A mature ISMS lowers incident frequency and severity, shortens audit cycles with consistent evidence trails, and simplifies vendor due diligence through standard artefacts like SoAs and risk registers. These efficiencies also help in procurement and insurance negotiations, where demonstrable controls can reduce friction and improve terms. The table below compares traditional audit approaches with AI-augmented methods to illustrate time and cost differences.
| Audit Method | Time-to-Certify | Cost | Accuracy/Coverage |
|---|---|---|---|
| Traditional on-site sampling | Long (months) | Higher (labour-intensive) | Moderate (sample-based) |
| Hybrid remote + manual | Moderate | Moderate | Improved coverage |
| AI-driven auditing | Short (weeks-to-months) | Lower (automated evidence) | Higher (broader coverage) |
Automation can compress timelines and broaden evidence coverage — outcomes that translate into specific cost savings and smoother vendor management.
What Are the Cost Benefits of ISO 27001:2022 Certification?
Certification reduces expected breach costs by lowering incident frequency and impact through preventive controls and faster response, which cuts remediation, legal and reputational expenses. Certified organisations also see faster procurement and improved insurance terms, turning security investment into lower operating costs over time. Comparing reduced incident costs and audit-efficiency gains against certification expense often shows a positive ROI within a multi-year horizon. Exact figures vary by sector and size, but systematic ISMS adoption consistently improves predictability of security-related costs.
How Does Certification Streamline Business Processes and Vendor Management?
ISO 27001 certification streamlines vendor management by providing standard supplier-assessment templates, clear contractual control expectations, and reusable evidence that shortens repeated due diligence. Internally, standard operating procedures and mapped processes reduce variance, speed onboarding, and clarify escalation paths for third-party incidents. The SoA and supplier audit records become reusable procurement artifacts, shortening negotiations and reducing duplicated security checks so teams can focus on strategic priorities instead of baseline assurance tasks.
How Does ISO 27001:2022 Certification Build Customer Trust and Competitive Advantage?
ISO 27001:2022 acts as a market-proven trust signal that reassures customers, partners, and regulators about your commitment to protecting sensitive information. Certified organisations stand out in bids and RFPs where security assurances matter, and they commonly report smoother procurement and greater stakeholder confidence. Independent certification underpins reputational resilience and is persuasive in regulated sectors and partner decisions. The next subsection explains how those commercial benefits typically play out and which industries gain the most.
Why Is ISO 27001:2022 Certification a Market Differentiator?
Certification differentiates suppliers by providing a verified baseline of information security — often serving as a prequalification for sensitive contracts. Buyers see certification as evidence of mature governance, which reduces negotiation time and perceived vendor risk. In crowded markets, ISO 27001 can be the deciding factor in a selection process, boosting reputation and making security claims easier to substantiate — especially when certification is a tender requirement.
Which Business Sectors Benefit Most from ISO 27001:2022?
Industries that handle sensitive data or operate in regulated environments gain the most: finance, healthcare, cloud and managed-service providers, government contractors, and research organisations. SMEs targeting enterprise customers use certification to meet supplier prequalification thresholds, while large companies use it to harmonise controls across regions. Cloud providers show operational security to tenants with ISO 27001, and healthcare organisations pair it with HIPAA practices for patient data protection. These sector insights help prioritise controls and risk treatments.
After outlining market benefits, it’s important to connect certification outcomes — trust, procurement advantages, and certificate lifecycle support — to accredited certificate issuance and ongoing management services.
For organisations seeking accredited certification and lifecycle support, Stratlane Certification is an accredited body offering ISO certification services, including ISO 27001:2022. We combine AI-enabled audit tools with experienced auditors to improve assessment quality, speed, and cost-efficiency, issuing recognised certificates across 27+ countries and supporting clients from quotes and audits through to certificate management. Primary offering: ISO 27001:2022 Certification (ISMS).
How Does Stratlane’s AI-Driven Auditing Revolutionize ISO 27001:2022 Certification?
Stratlane’s AI-driven auditing speeds and improves ISO 27001:2022 certification by automating evidence collection, augmenting auditor analysis, and tightening reporting — reducing manual effort and accelerating decisions. As an accredited certification body, Stratlane blends AI tools with professional auditors to raise control coverage and shorten audit cycles. AI capabilities help reduce time-to-certify, lower audit labour costs, and increase control visibility through automated document mapping and anomaly detection.
Typical delivery follows: quote → AI-enabled gap analysis → focused audit → certificate issuance and ongoing certificate management. That sequence improves ROI by compressing audit cycles and letting human auditors concentrate on high-risk findings. Organisations benefit from faster evidence trails for surveillance audits, clearer SoAs produced by automated mappings, and lower administrative overhead for renewals. For buyers, these improvements reduce the total cost of compliance and increase audit transparency.
How Does AI Improve Audit Efficiency and Accuracy?
AI improves efficiency by locating relevant evidence across policies, logs, and configurations, mapping artefacts to Annex A controls, and flagging anomalies for reviewer attention. This reduces manual sampling and repetitive tasks, freeing auditors to assess control effectiveness and advise on corrective actions. AI-generated mappings and reports speed report production while improving coverage and repeatability across audit cycles. Combined with human judgment, the approach raises confidence in audit outcomes and accelerates remediation.
What Are Real-World Benefits of AI-Driven Auditing?
In practice, AI-driven auditing shortens certification timelines, lowers audit costs, and uncovers control gaps that manual methods might miss — delivering measurable audit ROI. Automated mapping and evidence collection can shrink initial assessments from months to weeks, while broader coverage decreases the chance of overlooked non-conformities during surveillance. These gains create stronger audit trails, support proactive remediation, and make certificate management more predictable — aligning with the operational and financial advantages described earlier.
- Faster Certification: Automated evidence aggregation shortens assessment windows.
- Lower Audit Cost: Fewer manual hours reduce third-party audit spend.
- Higher Coverage: Automated control mapping expands audited evidence breadth.
Together, these outcomes make AI-driven auditing a practical lever to lower total compliance cost and improve security posture without sacrificing rigour.
Frequently Asked Questions
What is the process for obtaining ISO 27001:2022 certification?
Typically, the process starts with a gap analysis to identify ISMS shortfalls. Next you implement required controls and document processes. An accredited certification body (for example, Stratlane Certification) then performs an audit against the standard. If your ISMS meets requirements, you receive certification — generally valid for three years — with periodic surveillance audits to confirm continued compliance.
How often should an organization review its ISMS under ISO 27001:2022?
At minimum, review your ISMS annually. More frequent reviews are best after significant organisational changes, security incidents, or changes to the regulatory landscape. Continuous monitoring and periodic internal audits are recommended to spot gaps early and ensure the ISMS stays aligned with risks and business objectives.
What are the common challenges organizations face when implementing ISO 27001:2022?
Common challenges include resistance to change, limited management engagement, and constrained resources for training and documentation. Organisations also struggle with accurate risk assessment and aligning the ISMS with existing processes. Overcoming these issues requires visible leadership support, a clear roadmap, targeted training, and pragmatic prioritisation of high-risk controls.
How does ISO 27001:2022 certification impact business reputation?
Certification strengthens reputation by proving a commitment to information security and data protection. It serves as a clear trust signal to customers, partners and regulators, reduces procurement friction, and can be decisive in competitive bids. Independent verification also helps preserve credibility in regulated industries and during stakeholder due diligence.
Can small and medium-sized enterprises (SMEs) benefit from ISO 27001:2022 certification?
Yes. SMEs gain a structured approach to managing information security, which protects sensitive data and builds customer trust. Certification can unlock new business opportunities where buyers require certified suppliers, and the ISMS implementation itself often improves operational efficiency and reduces breach risk, lowering long-term costs.
What role does employee training play in ISO 27001:2022 compliance?
Employee training is essential. It ensures staff understand their security responsibilities, recognise threats, and follow policies and procedures. Regular, role-specific training reinforces compliance, reduces human error, and supports a security-aware culture — a critical factor in preventing many common incidents.
Conclusion
ISO 27001:2022 certification delivers clear advantages: stronger security, better alignment with privacy regulations, and operational efficiencies that reduce cost and risk. A well-run ISMS helps organisations manage risk, demonstrate compliance, and build trust with customers and partners. If you’re ready to move toward certification, Stratlane Certification combines accredited auditing with AI-enabled tools and expert support to make the journey faster, clearer, and more cost-effective. Learn how we can support your ISO 27001:2022 certification today.