Master ISO Certification Steps: Your Ultimate Guide
ISO Certification: A Practical Step-by-Step Guide
ISO certification proves your management system meets global requirements for quality, environment, information security, or AI governance. This guide walks you through the process—from selecting the right standard and running a gap analysis to internal audits, Stage 1 and Stage 2 assessments, and ongoing surveillance and recertification. You’ll find practical actions, realistic timelines, and decision points designed to reduce risk and speed certification. We also cover how AI is changing audit workflows, how an accredited certification body supports each phase, common pitfalls to avoid, and clear next steps for requesting a quote and booking an audit. Expect concise checklists, comparison tables, and readiness matrices to make the route to certification easier to follow.
What Are the Key ISO Standards and How Do You Choose the Right One?
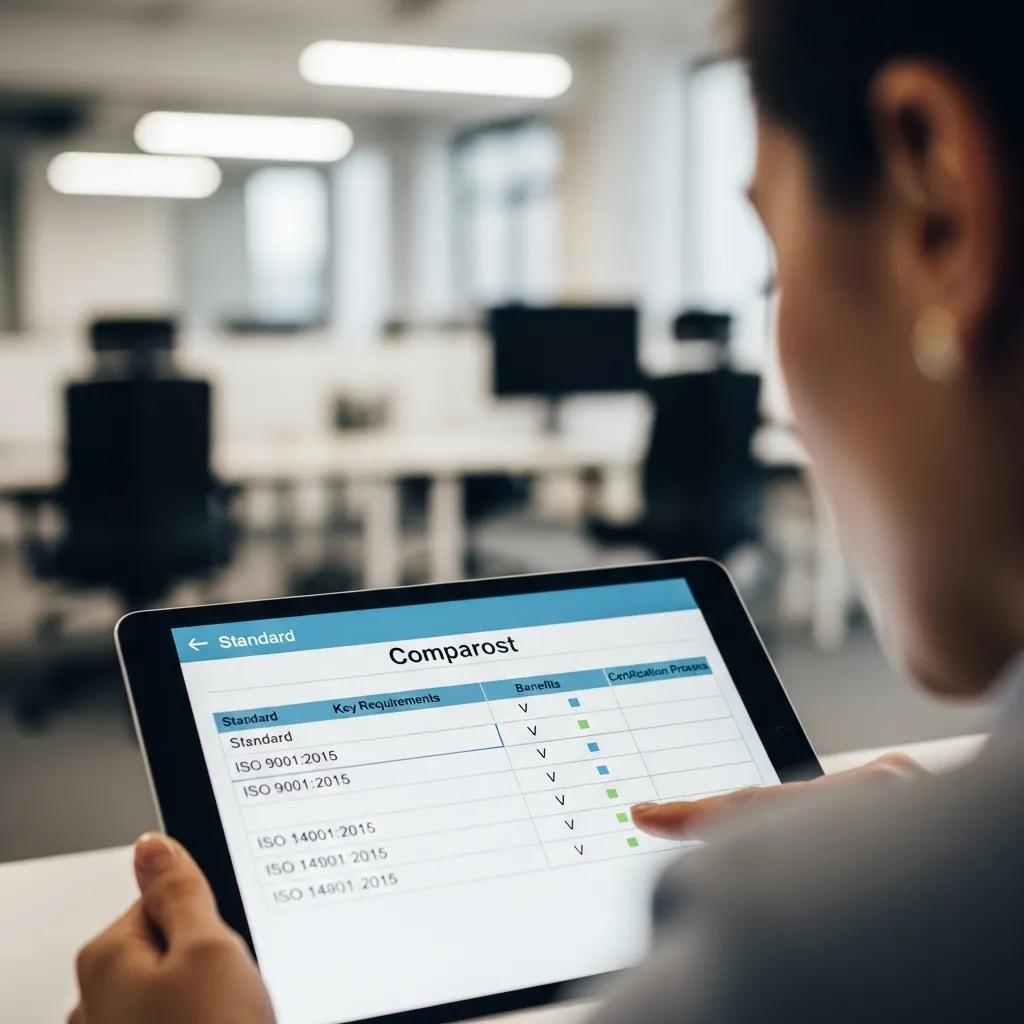
ISO standards turn management principles into auditable requirements. Choosing the right one depends on your business goals, regulatory needs, and exposure to specific risks. ISO 9001 is about quality management and customer satisfaction through controlled processes and continual improvement. ISO 14001 focuses on environmental management and legal compliance. ISO 27001 creates a formal information security management system to protect confidentiality, integrity and availability. ISO 42001 sets governance and risk controls for AI systems. Look at each standard’s controls, required risk assessments, and monitoring needs, and weigh customer or tender requirements, environmental or data risks, and strategic initiatives like responsible AI. The short comparison below helps match your priorities to the right standard.
The table below summarizes scope, primary requirements, and typical business outcomes to help your initial decision.
| Standard | Core Scope | Primary Requirements |
|---|---|---|
| ISO 9001 | Quality Management System (QMS) | Controlled processes, measurable objectives, customer focus, corrective action |
| ISO 14001 | Environmental Management System (EMS) | Identify environmental aspects, legal compliance, environmental objectives |
| ISO 27001 | Information Security Management System (ISMS) | Risk assessment, select controls, incident response and monitoring |
| ISO 42001 | AI Management System (AIMS) | Governance, risk mitigation, transparency and accountability for AI |
This comparison shows how each standard aligns with different business priorities and prepares you to match operational risks and market drivers to the standard’s scope.
What Is ISO 9001 and Its Role in Quality Management Systems?
ISO 9001 sets out requirements for a Quality Management System that helps organizations meet customer needs consistently and improve satisfaction. The standard emphasizes process mapping, objective-setting, performance monitoring, corrective action, and active leadership involvement to enable continual improvement. Implementing ISO 9001 clarifies responsibilities, reduces process failures, and strengthens supplier and customer relationships—delivering measurable operational gains and less rework. Typical steps are scoping, defining core processes, creating essential procedures and records, training teams, conducting internal audits, and resolving nonconformities before certification. Knowing these QMS building blocks helps you plan resources, timelines, and change activities ahead of an external assessment.
How Do ISO 14001, ISO 27001, and ISO 42001 Address Environmental, Information Security, and AI Management?
Each of these standards uses risk-based thinking and continual improvement, but they focus on different risk areas. ISO 14001 requires you to identify environmental aspects and legal obligations, implement operational controls, and set objectives to reduce impacts and improve resource efficiency. ISO 27001 requires a formal risk assessment, selection of security controls, incident handling, and evidence of monitoring to protect information assets. ISO 42001 centers on AI governance—documented oversight, strategies to reduce algorithmic harm, and mechanisms for transparency and accountability. If risks overlap, many organizations integrate multiple standards to create a single, resilient management system.
How to Prepare for ISO Certification: Gap Analysis and Management System Development
Preparation starts with a structured readiness assessment to identify where your current practices meet the standard and where remediation is needed. A gap analysis compares existing processes to the chosen standard’s clauses and produces prioritized corrective actions, required documentation, and resource estimates. Typical gap analysis steps include scoping, document review, process walkthroughs, interviews, and scoring observations to create an actionable plan for leadership approval. Effective preparation also defines a documentation hierarchy, assigns process owners, and trains staff on new controls so the system can show both implementation and effectiveness during audits. The readiness table below helps teams score and prioritize areas by documentation and control maturity.
Use this table to decide where to focus remediation and to build a prioritized action plan before booking external audits.
| Process Area | Documentation / Controls | Readiness Status |
|---|---|---|
| Management commitment | Policy, objectives, evidence of management review | Partially documented |
| Risk assessment | Risk registers, treatment plans, review records | Present |
| Operational controls | Procedures, work instructions, monitoring records | Partially documented |
| Incident handling | Reporting forms, response procedures, logs | Absent |
What Is a Gap Analysis and How Does It Assess Your Readiness?
A gap analysis is a structured comparison of your current practices against a standard’s requirements. It collects evidence—documents, records and observed outputs—maps processes to clauses, and scores conformity so you can distinguish critical nonconformities from minor observations. The result is a remediation roadmap with owners, deadlines and deliverables to move controls from partial or missing to implemented and effective. Running a gap analysis early reduces surprises in Stage 1 and Stage 2 audits by revealing evidence gaps and training needs. Once you document the gaps, sequence corrective actions to lower audit risk and show continual improvement to auditors.
Research and practical experience consistently show that a gap analysis is a practical first step for assessing ISO 9001 readiness and shaping clear recommendations for improvement.
ISO 9001 Certification Readiness & Gap Analysis
This study evaluates a company’s readiness for ISO 9001:2015 certification using a gap analysis methodology. The approach maps current practices to ISO requirements, highlights shortfalls, and provides recommendations to improve preparedness ahead of certification.
How to Develop Documentation and Build Your Management System
Documentation should follow a simple hierarchy—policy, objectives, procedures, work instructions and records—so the system is consistent and traceable. Start with a short, leadership‑approved policy, map high‑level procedures to core processes, and use templates for work instructions and records to speed consistent output. Apply version control, assign document owners, and keep a central repository for controlled documents to improve auditability. Where it helps, AI drafting tools can accelerate document creation and standardize terminology, but training and internal audits are still essential to confirm people follow the documented processes. Build the system iteratively so you can demonstrate both compliance and effectiveness at certification time.
What Are the Steps in the ISO Audit Process: Internal and External Audits Explained?
The audit path moves from internal verification to external certification through defined stages that confirm documentation, implementation and effectiveness. Internal audits validate conformance and surface corrective actions. Stage 1 external audits review documentation and readiness. Stage 2 audits verify implementation and effectiveness through evidence, interviews and observation. Surveillance audits keep the system in check between full recertification cycles. Auditors use sampling, interviews and records review to build objective evidence that controls are in place and working—reducing surprises and clarifying timelines for closing nonconformities. The table below shows typical durations and outputs to help plan resources before booking external auditors.
This table outlines expected timeframes and deliverables for each audit stage to guide scheduling and resource planning.
| Audit Stage | Typical Duration | Typical Outputs |
|---|---|---|
| Internal audit | 1–5 days (per cycle, depending on scope) | Internal audit report, findings, corrective actions |
| Stage 1 (documentation review) | 0.5–2 days | Readiness feedback, scope confirmation, findings |
| Stage 2 (on-site or remote verification) | 1–5 days | Nonconformity reports, corrective action timelines, recommendation |
| Surveillance audit | 1 day annually (per site) | Surveillance findings, ongoing conformity evidence |
How to Conduct Internal Audits and Management Reviews Effectively
Internal audits are proactive checks that verify process performance, uncover nonconformities and drive continual improvement. Build an internal audit program that specifies frequency, scope, competent auditors and reporting lines. Use concise checklists tied to standard clauses for consistent coverage. Management reviews should use audit results, performance metrics and change inputs to set objectives and assign resources; these reviews are key leadership evidence required by ISO. A good cadence combines regular internal audits, timely closure of corrective actions, and quarterly or semi‑annual management reviews to complete the feedback loop. Together, these practices create the operational discipline auditors expect in Stage 1 and Stage 2 assessments.
What Happens During Stage 1 and Stage 2 External Certification Audits?
Stage 1 is a documentation review and scope confirmation. Auditors assess readiness and point out areas that need remediation—this reduces risk before the full assessment. Stage 2 verifies implementation and effectiveness: auditors collect evidence through interviews, records and observation of operational controls to determine conformity. Nonconformities found in Stage 2 are classified by severity and come with deadlines to submit corrective responses and evidence of closure before a certificate is issued. When nonconformities are satisfactorily closed, the certification body recommends certificate issuance and explains the surveillance schedule for ongoing compliance. Knowing these different objectives helps you prepare targeted evidence and shortens the time from audit to certificate.
How Does Stratlane’s AI-Driven Auditing Enhance the ISO Certification Process?
AI-driven auditing complements traditional methods by automating evidence collection, speeding document review, and surfacing anomalies that need auditor attention—improving efficiency and coverage. The approach combines document parsing, anomaly detection in process data, and evidence aggregation so auditors spend less time on repetitive tasks and more time on judgment calls. Stratlane Certification pairs these AI tools with experienced auditors operating in over 29 countries to increase efficiency and cost‑effectiveness while preserving human judgement for interpreting findings and confirming closure. The result is faster audits, less on‑site time when remote verification is possible, and sharper auditor focus on high‑risk areas identified by AI. The table below maps AI features to typical benefits.
This table links AI auditing features to the practical benefits organizations commonly see during certification engagements.
| AI Feature | Attribute | Benefit / Metric |
|---|---|---|
| Automated evidence collection | Document parsing and indexing | Reduces time spent locating evidence; increases scope coverage |
| Anomaly detection | Pattern recognition in records | Flags outliers for auditor review; improves risk detection |
| Evidence aggregation | Centralized audit package | Speeds report compilation; shortens decision cycles |
In What Ways Does AI Improve Audit Efficiency, Accuracy, and Cost Savings?
AI boosts efficiency by automating repetitive evidence tasks and pre‑filtering documents, cutting auditor prep and on‑site time. Accuracy improves through pattern and anomaly detection that highlight risks humans may miss in large datasets, letting auditors focus on judgment and control effectiveness. Cost savings come from reduced travel, shorter audits, and more viable remote verification while keeping audit rigor intact. Stratlane blends automated analytics with professional sampling and auditor expertise so organizations gain both speed and reliable assurance. Many clients run a pilot audit to measure AI benefits against their specific systems and data maturity.
What Are Real-World Case Studies Demonstrating AI in ISO 9001 and ISO 27001 Audits?
Short anonymized summaries show how AI-assisted audits delivered results across standards and sectors. In a manufacturing quality engagement, AI indexing of production records and nonconformance logs sped evidence retrieval and exposed recurring root causes, enabling quicker corrective actions and improved KPIs. In an information security project, automated log analysis and anomaly detection prioritized critical incident trends so auditors could evaluate control effectiveness faster, reducing verification time. These cases show how AI shortens audit cycles and improves issue detection while human auditors validate system‑level effectiveness. Results vary by scope, data maturity and organizational context.
What Are the Benefits of ISO Certification and How to Maintain Compliance?
ISO certification gives third‑party assurance that your management system meets recognized standards. That improves credibility, helps access regulated markets and tenders, and standardizes risk management across the organization. The benefits come from consistent processes, measurable objectives, and documented evidence that reduce variability, build customer confidence, and mitigate operational and regulatory risk. Maintaining compliance requires surveillance audits, regular internal audits, timely closure of corrective actions, monitoring performance against objectives, and periodic management reviews to support continual improvement. The short checklist below captures the main benefits and maintenance steps.
Organizations keep certification valuable by collecting performance data, acting on audit findings, and embedding continual improvement into daily operations.
- Enhanced credibility: Third‑party validation boosts bids and customer trust.
- Market access: Certification meets supplier and tender requirements.
- Operational consistency: Standardized processes reduce defects and incidents.
- Risk reduction: Formal risk assessment and controls lower exposure to threats.
These outcomes explain why organizations invest in certification and why regular maintenance is essential to preserve those advantages.
How Does ISO Certification Enhance Credibility, Market Access, and Risk Management?
ISO certification signals to customers, partners and regulators that your organization follows externally verified practices—supporting contract eligibility and competitive differentiation. Third‑party assurance from an accredited certification body confirms controls are in place and effective, reducing buyer uncertainty in procurement and supply chains. Certification also reinforces internal risk frameworks by embedding routine risk assessment, incident handling and continual improvement into operations, lowering the chance of costly failures or compliance breaches. Many large tenders and preferred supplier lists require certification, so keeping the certificate current preserves market access and partner confidence.
What Are Surveillance Audits, Recertification, and Continuous Improvement Practices?
Surveillance audits are periodic checks—usually annual—to confirm the management system still meets the standard and that corrective actions remain effective. Recertification is a full reassessment, typically every three years. Ongoing conformity relies on internal audits, KPIs, management reviews, and timely closure of nonconformities to show continual improvement. Best practices include a documented audit program, centralized tracking of action items, and using management review outcomes to set realistic objectives and allocate resources. Making continual improvement part of your culture keeps the organization audit‑ready and shows stakeholders that certification is an active, valuable asset.
How to Get a Quote and Start Your ISO Certification Journey with Stratlane?
Requesting a quote and booking an audit starts with a clear scope and basic information so a certification body can estimate effort and cost accurately. Main cost drivers include scope (which standards and processes are in scope), number of sites, organizational complexity, and whether audits will be on‑site or remote. Combining standards into a single assessment can reduce duplication and cost. Stratlane Certification provides a structured intake and quote process as part of full ISO services that cover initial inquiry, audit execution (on‑site or remote), issue resolution, certificate issuance and ongoing certificate management. We operate professional auditors in over 29 countries to support multi‑site and global assessments. The list below shows typical information needed to request a tailored quote and what to expect for scheduling.
- Scope summary: Standards requested and high‑level process or site coverage.
- Sites and locations: Number of sites and whether audits will be combined.
- Staffing and processes: Approximate employee count and complexity indicators.
- Preferred audit mode: On‑site, remote, or hybrid approach.
Having this information ready shortens quote turnaround and helps the certification body design an efficient audit plan.
What Factors Influence ISO Certification Costs and How to Request a Personalized Quote?
Certification costs are driven by the effort needed to review documentation and verify implementation across your scope and locations. Key factors include number of sites, geographic spread, process complexity, multiple standards, audit duration, and travel requirements when remote auditing isn’t feasible. To get a personalized quote, provide a clear scope, site list, estimated employee numbers or shifts, and any customer or regulatory constraints that affect audit depth. Stratlane’s quote process considers these variables and offers remote audit and certificate management options to optimize cost and scheduling. With a clear intake, you can expect a tailored estimate and proposed timeline.
What to Expect During the Certification Process and How to Book an Audit Appointment?
After accepting a quote and confirming scope, we schedule audit dates, request documentation for Stage 1, and finalize logistics for Stage 2 verification. The timeline from quote to certificate typically spans several weeks to a few months, depending on remediation work. Client responsibilities include providing requested documents, making staff available for interviews, granting site or system access, and closing nonconformities within agreed timelines to allow certificate issuance. Booking an audit means confirming scope, choosing on‑site or remote modes, and aligning stakeholder availability for interviews and evidence review. Stratlane supports scheduling, audit execution, and post‑audit certificate management to guide clients from inquiry to issued certificate with clear expectations.
This guide has covered standards, preparation steps, audit stages, AI‑enhanced auditing, benefits and maintenance, and practical steps to request a quote and schedule certification services.
Frequently Asked Questions
What is the role of an accredited certification body in the ISO certification process?
An accredited certification body provides independent verification that your management system meets the chosen ISO standard. They run Stage 1 and Stage 2 assessments to evaluate documentation, implementation and effectiveness. Their independence and accreditation give the certificate credibility with customers and regulators. Certification bodies also offer practical guidance on audit readiness and help clients understand and close findings, smoothing the certification journey.
How often do organizations need to undergo surveillance audits after certification?
Surveillance audits are usually conducted annually after certification. Their purpose is to confirm the management system continues to meet the standard and that previous corrective actions remain effective. These audits maintain certification integrity and give organizations a chance to show continual improvement ahead of the full recertification audit, which commonly occurs every three years.
What are the common pitfalls organizations face during the ISO certification process?
Common pitfalls include insufficient preparation, weak leadership involvement, and limited employee engagement. Skipping a thorough gap analysis can lead to unexpected findings in audits. Poorly documented processes or slow closure of nonconformities also delay certification. To avoid these issues, prioritize planning, secure management commitment, train staff, and keep communication open throughout the project.
How can organizations ensure continuous improvement after obtaining ISO certification?
Continuous improvement relies on regular internal audits, meaningful management reviews, and tracking measurable objectives and KPIs. Collect feedback from employees and stakeholders, act promptly on audit findings, and feed lessons learned back into process changes. Making these activities part of routine operations helps sustain compliance and improves your management system over time.
What is the significance of documentation in the ISO certification process?
Documentation provides the evidence auditors need to confirm compliance. It maps policies, procedures and records that guide daily work and show traceability. Well‑structured documentation ensures consistency, supports training and makes audits smoother. In short, good documentation is essential to achieve and maintain certification and to demonstrate commitment to continual improvement.
How does AI-driven auditing differ from traditional auditing methods?
AI‑driven auditing supplements traditional methods by automating document review, evidence collection and anomaly detection. Instead of manually sifting large volumes of records, AI pre‑filters relevant evidence and highlights unusual patterns for auditor review. This reduces repetitive work, improves coverage, and lets auditors focus on assessing control effectiveness. The combination of AI tools and experienced auditors yields faster, more targeted audits without sacrificing judgment.
Conclusion
ISO certification gives your organization a proven framework to improve credibility, consistency and risk management. By understanding the certification steps and using AI‑enhanced audit tools where appropriate, you can streamline the path to compliance and sustain continuous improvement. Partnering with an accredited body like Stratlane simplifies the process and helps you capture the full value of certification. Start your ISO certification journey today by requesting a personalized quote and taking the first step toward stronger, more reliable operations.