Latest ISO Revisions: Key Compliance Changes You Should Know
Latest ISO revisions and compliance updates — Practical guidance for ISO 9001, 27001, 14001 and AI management systems
ISO standards have evolved significantly across 2023–2026, changing how organisations handle quality, information security, environmental management and AI governance. This guide breaks down confirmed and expected updates to ISO 9001, ISO 27001, ISO 14001 and ISO 42001, explains what they mean for businesses in the UK and EU, and gives concrete steps you can take to stay compliant and keep market access. You’ll find concise change summaries, transition timelines, control mappings and hands‑on checklists to align your management systems. We also cover how AI-driven auditing reshapes evidence collection and offer practical advice for managing certification journeys and certificate lifecycles. Keywords such as iso standard updates, latest iso revisions, compliance changes, AI-driven auditing and certificate management are included to help discoverability and provide a clear roadmap for compliance readiness (Dec 2025).
What are the key changes in the ISO 9001:2026 revision?
ISO 9001:2026 brings resilience, digital evidence and sustainability into sharper focus and widens expectations around supply‑chain risk and acceptable use of AI in quality processes. The revision increases emphasis on organisational knowledge, supplier oversight and traceable records when automated decisions affect conformity. In practice, you’ll need clearer records of AI-assisted decisions, demonstrable resilience planning, and explicit links between quality objectives and environmental or social outcomes. Below is a compact summary of the top changes and a clause-level comparison to help prioritise updates.
Key changes at a glance:
- Resilience and business continuity are explicit QMS outcomes that require documented preparedness.
- Greater supplier oversight and resilience obligations, with focus on critical dependencies.
- Digital transformation and AI are recognised as process enablers but require governance and audit evidence.
- Stronger alignment between quality objectives and sustainability performance.
This snapshot shows where operations and compliance owners should review existing QMS documents and controls; the following sections unpack resilience and the role of digital tools and AI.
Different clause emphases create specific action needs; the table below compares selected attributes from the 2015 edition to the 2026 orientation and where to focus efforts.
Table: Clause-level comparison and practical implications
| QMS Attribute | 2015 Orientation | 2026 Revision Focus |
|---|---|---|
| Resilience | Implicit through risk-based thinking | Documented resilience planning, testing and recovery |
| Supply-chain | Supplier evaluation and control | Critical-supplier resilience and dependency mapping |
| Digital/AI integration | Limited automation references | Governance, traceability and auditable AI evidence |
| Sustainability linkage | Optional alignment to objectives | Direct links between quality outcomes and sustainability goals |
Use this table to reallocate audit focus and update system documentation. The next section explains how resilience shapes operational QMS changes and provides practical checklists.
How does ISO 9001:2026 enhance quality management and resilience?
ISO 9001:2026 defines resilience as the ability to anticipate, respond to and recover from disruptions while maintaining quality outputs. The standard expects organisations to show preparedness through documented scenarios, recovery measures and evidence of learning. Resilient QMS reduce downtime, protect customer confidence and support supply‑chain continuity — so you should set resilience objectives, run scenario tests and record corrective learning. Practical measures include supplier dependency maps, alternative sourcing strategies and regular recovery-plan tests. For manufacturers, link production continuity plans to quality acceptance criteria; for service providers, show recovery of critical service levels after major incidents. Start with a focused gap analysis and iterative exercises that feed continuous improvement and audit evidence trails.
These resilience rules naturally increase the need for reliable digital evidence and oversight when automated tools are in use, which we address next.
What role does digital transformation and AI play in the new ISO 9001?
ISO 9001:2026 recognises digital tools and AI as valid enablers of quality management but requires governance, transparency and auditable evidence for automated decisions that affect conformity. Typical mechanisms include automated inspections, predictive maintenance models and AI-assisted nonconformity detection. The standard expects documented model purpose, validation records and human‑in‑the‑loop oversight for impactful decisions. The upside is faster detection and richer evidence; the obligation is traceability — versioned models, decision logs and performance metrics must be kept for audits. Practical steps: add an AI governance policy to your QMS, define acceptance criteria for model outputs, and feed model monitoring into corrective action workflows. Clear algorithmic evidence reduces auditor uncertainty and shows control alignment under the revised clauses.
These digital controls also intersect with information security and lifecycle responsibilities in ISO 27001 and ISO 42001, which we cover next.
How should organisations prepare for ISO 27001:2022 updates and transition?
ISO 27001:2022 consolidated Annex A controls (from 114→93) and adds focus areas aligned to cloud services, software security and data lifecycle governance. Preparation means mapping legacy controls to the new structure, running a gap analysis, updating risk assessments to include new categories, planning remediation and scheduling audits ahead of transition milestones. Below is a short transition checklist for immediate use, followed by a controls comparison table to clarify reworked areas and suggested actions.
Transition checklist (quick reference):
- Map your current controls to the ISO 27001:2022 control set and identify gaps.
- Prioritise remediation for cloud, endpoint and data‑lifecycle controls.
- Update your Statement of Applicability (SoA), refresh evidence repositories and schedule certification audits.
Treat this checklist as a live project plan and align resources to business‑critical assets. The table below compares notable control changes and practical remediation steps.
Control comparison: notable updates and recommended actions
| Control Domain | Key Change (pre-2022 → 2022) | Recommended Action |
|---|---|---|
| Asset management | Controls re‑categorised | Remap assets to new categories and update inventory evidence |
| Cloud and virtualization | New cloud‑focused controls | Apply cloud configuration baselines and continuous monitoring |
| Software security | Greater emphasis on secure development | Embed secure SDLC practices and retain code‑review records |
| Data lifecycle | Stronger lifecycle governance | Define retention, minimisation and deletion controls with logs |
This mapping helps you allocate remediation effort; the next sections unpack major control changes and outline the official transition timeline.
What are the major control changes in ISO 27001:2022?
ISO 27001:2022 streamlines overlapping controls into broader objectives that align better with modern IT architectures — reducing fragmentation and emphasising cloud, application security and data lifecycle responsibilities. Practically, you’ll need to update inventories and SoA entries, show secure cloud configurations, adopt secure development practices and document data minimisation and disposal procedures. For example, a SaaS provider should present configuration‑as‑code evidence, vulnerability metrics and deployment test records. Recommended remediation actions include policy updates, enforcing technical baselines and using automated evidence collection to support continuous assurance.
These changes affect your transition schedule, which the next subsection sets out with a priority framework.
What is the deadline and process for transitioning to ISO 27001:2022?
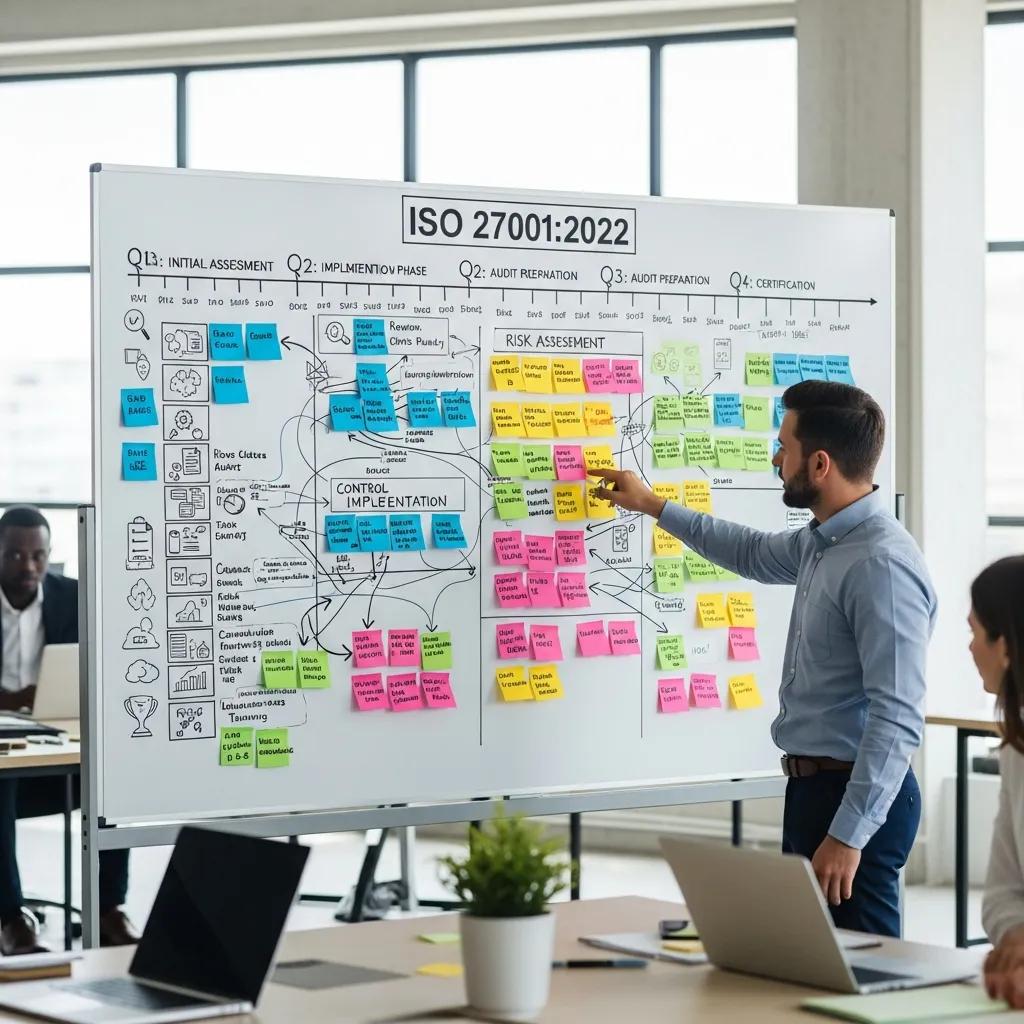
The transition process requires a gap analysis, prioritized remediation, updated risk treatment plans and certification audits scheduled to meet accreditation timelines. Treat the revision as a time‑bound programme with clear checkpoints: map existing controls to the 2022 objectives, prioritise by risk and business impact, update documentation and evidence storage, then book Stage 1/Stage 2 audits with an accredited body. Prioritise controls protecting critical assets and cloud exposure, then tidy procedural artifacts like policies and retention schedules. Early engagement with your certification body reduces rework and helps clarify evidence expectations.
This transition planning links directly to environmental and sustainability updates in ISO 14001, which increasingly influence cross‑standard compliance.
What are the environmental and sustainability focuses in ISO 14001:2025?
ISO 14001:2025 raises the bar on climate action, emissions accountability and circular‑economy thinking, integrating environmental risk and lifecycle perspectives into EMS requirements. The revision pushes for measurable environmental objectives, lifecycle impact assessments, and procurement rules that favour resource efficiency and reuse. Organisations must show how environmental objectives sit inside operational controls, procurement and supplier selection — and demonstrate progress with quantifiable metrics. The table below summarises key attributes and compliance implications, with later sections on climate action, circular economy measures and UK/EU regional considerations.
Table: Environmental focus comparison and operational implications
| EMS Attribute | 2015 Orientation | 2025 Revision Focus |
|---|---|---|
| Climate action | General environmental objectives | Explicit mitigation/adaptation planning and emissions accounting |
| Lifecycle perspective | Optional LCA use | Lifecycle considerations mandatory for key products/services |
| Circular economy | Encouraged practices | Procurement and design controls to enable reuse and recycling |
| Reporting alignment | Variable | Closer alignment with regulatory ESG reporting expectations |
EMS owners must extend documentation and measurement systems to meet lifecycle and climate requirements; the next sections explain how to operationalise these expectations.
How does ISO 14001:2025 address climate action and the circular economy?
ISO 14001:2025 asks organisations to embed climate mitigation and adaptation into environmental objectives and operational controls, using lifecycle assessment to prioritise interventions and to show measurable emissions reductions where relevant. The approach is evidence‑driven: baseline emissions, reduction targets, monitoring methods and adaptation plans should be recorded. Circular economy requirements require procurement criteria that favour reusable or recyclable materials, design‑for‑reuse principles and documented waste‑reduction programmes. Practical actions include targeted LCAs for high‑impact products, updating procurement specs with circularity criteria, and supplier engagement to improve material reuse. These steps yield auditable metrics and align EMS performance with sustainability commitments.
Putting these measures in place — especially circular‑economy practices — delivers tangible gains in control and resource efficiency.
ISO 14001:2025 — Environmental management and circular economy
Implementing the 2025 guidance simplifies the detection and recovery of priority areas, tightens control and monitoring processes, and encourages more efficient use of resources within a circular‑economy framework. The model offers a practical structure for environmental management aligned to the updated standard.
Operationalising these environmental aims also requires understanding how ISO 14001:2025 intersects with UK and EU regulation, which we outline next.
What are the compliance implications for UK and EU businesses?
For organisations operating in the UK and EU, ISO 14001:2025 is more closely linked to regional regulatory expectations around emissions reporting, ESG disclosures and extended producer responsibility. That means EMS outputs should be harmonised with statutory reporting and stakeholder disclosures. Authorities increasingly expect traceable emissions accounting, lifecycle evidence for certain products and procurement transparency. Practical steps: map EMS indicators to regulatory metrics, centralise environmental data, align measurement methods to common standards and coordinate supplier reporting to secure reliable upstream data. This alignment helps your EMS serve both certification and regulatory needs.
These environmental and regulatory requirements sit alongside AI governance expectations in ISO 42001, discussed next.
What is ISO 42001:2023 and how does it govern AI management systems?
ISO 42001:2023 sets out requirements for AI Management Systems (AIMS), providing a framework to design, implement and govern AI systems with emphasis on ethics, risk governance, transparency and lifecycle risk management. The standard requires clear AI purpose and scope, lifecycle risk assessments, documentation for model development and deployment, and human oversight for critical decisions. Core obligations include ethical principles, traceability of outputs and validation records — making ISO 42001 a practical governance layer that connects to ISO 27001 and ISO 9001. A short definition and three core requirements follow to make the essentials clear.
ISO 42001 is quickly becoming the go‑to operational framework for responsible AI development and deployment.
ISO 42001 — auditing and building responsible AI systems
The standard provides a certifiable AI management framework that clarifies ethical and legal considerations, helping organisations implement and demonstrate responsible AI practices throughout the model lifecycle.
Definition and three key requirements (quick summary):
ISO 42001:2023 is an AI Management System standard that prescribes governance, lifecycle risk management and ethical controls for AI systems. Its three core requirements: clear ethical AI principles (transparency, fairness, accountability), documented lifecycle risk governance, and demonstrable model traceability and validation.
What are the ethical AI and risk governance requirements in ISO 42001?
ISO 42001 expects organisations to adopt explicit ethical principles — transparency, fairness and accountability — and to put those principles into operation through governance, role definitions and documented controls that manage risk across data, model development and deployment. The governance loop converts policy into risk assessments, mitigation, monitoring and stakeholder communication. You must show dataset provenance, bias checks, validation results and decision‑logging to support auditability. A pragmatic governance model includes an AI steering committee, owners for risk treatment and regular review cycles. These artefacts give auditors a clear trail from principle to implemented control and measured outcome.
This governance framework also maps to regulatory regimes such as the EU AI Act, which we compare next.
How does ISO 42001 align with the EU AI Act and other regulations?
ISO 42001 complements the EU AI Act by offering operational controls and lifecycle processes that demonstrate due diligence and readiness. While ISO 42001 helps satisfy many conformity expectations for higher‑risk AI systems, statutory duties under the EU AI Act remain legal obligations that may go beyond voluntary standard conformance. Practical steps: map ISO 42001 clauses to regulatory articles, document gaps and use ISO 42001 audit evidence to support regulatory records and supplier assurance. This combined approach helps multinational organisations harmonise AIMS governance across jurisdictions.
How is AI transforming ISO auditing and certification processes?
AI is reshaping ISO auditing through continuous monitoring, automated evidence analysis and risk‑based sampling that widen audit scope and frequency while cutting manual effort. Techniques include automated log analysis, anomaly detection and NLP review of records to surface inconsistencies for human auditors. Benefits are efficiency, broader coverage and faster trend detection; limits centre on the need for human oversight, model validation and governance to avoid false positives and context errors. Below we list benefits and show a typical AI‑assisted audit workflow.
Shifting from periodic checks to continuous assurance matters because traditional compliance approaches struggle with real‑time, distributed operations and evolving regulation.
AI-driven compliance: data privacy, environmental standards and audit challenges
The rise of connected operations creates compliance complexity across data privacy (e.g., GDPR), safety and environmental rules. Traditional, periodic compliance methods often lack the speed and scale required for real‑time environments, increasing regulatory and reputational risk.
AI‑driven auditing offers measurable benefits:
- Efficiency gains: Automated evidence collection and analysis reduce routine manual work.
- Improved accuracy: Pattern detection flags anomalies manual sampling can miss.
- Continuous monitoring: Near‑real‑time surveillance speeds remediation and prevention.
These shifts move audit practice toward continuous assurance and create new expectations for evidence retention and model governance. A typical AI‑assisted audit workflow looks like this:
- Automated data ingestion and normalisation from operational systems.
- Machine analysis to flag anomalies, control gaps and trends.
- Human auditor review and contextual validation of AI‑flagged items.
- Consolidated audit report combining AI evidence summaries and human conclusions.
This workflow shows how AI expands coverage while keeping human judgement for material decisions. The next subsection explains how Stratlane Certification applies AI practically and responsibly.
What are the benefits of AI‑driven auditing for ISO compliance?
AI‑driven auditing increases audit scope, speeds evidence processing and improves detection of systemic issues through pattern recognition, delivering measurable time savings and earlier risk detection. The model pairs algorithmic triage with targeted human review: AI narrows focus and highlights areas needing deeper assessment, improving accuracy and reducing time‑to‑report. Use cases include continuous log analysis for ISO 27001, predictive quality failure detection for ISO 9001 and emissions‑trend validation for ISO 14001. Organisations report faster audit prep, earlier detection of issues and quicker corrective action — all improving management‑system resilience and, where governance is strong, reducing audit cycles.
How does Stratlane Certification leverage AI tools for efficient audits?
Stratlane Certification uses AI tools to accelerate evidence analysis and sharpen auditor focus while preserving human oversight. Our workflow pairs AI‑assisted evidence collection with lead auditor validation and consolidated reporting, cutting time spent on manual evidence assembly and deepening audit coverage. Clients benefit from shorter audit timelines, clearer evidence trails and pragmatic remediation guidance delivered by experienced auditors across Europe and the UK. Organisations can request quotes or book AI‑assisted readiness reviews and, after certification, access our certificate database and download services.
What are the steps and benefits of navigating the ISO certification journey?
ISO certification follows a clear path — gap analysis, implementation and remediation, Stage 1 documentation review, Stage 2 effectiveness audit, then ongoing surveillance — and each phase delivers measurable business benefits like market access, risk reduction and process improvement. Certification is evidence‑based validation: you must show consistent implementation and effective control operation. The list below outlines a typical timeline and actions, followed by a table showing how Stratlane supports each step with AI and audit expertise.
Certification steps overview:
- Gap analysis: Identify deviations from the standard and prioritise remediation by risk.
- Implementation & remediation: Close control gaps, update documentation and enable monitoring.
- Stage 1 audit: Documentation review to confirm readiness for the full audit.
- Stage 2 audit & certification: On‑site or remote validation of control effectiveness and certificate issuance.
- Surveillance & recertification: Ongoing audits to retain certification and drive continual improvement.
These steps show how certification delivers ROI through stronger controls and stakeholder assurance. The table below compares audit phases with Stratlane support and expected outcomes.
Service support comparison (audit step | Stratlane support | expected outcome/time/cost note)
| Audit Phase | Stratlane Support | Expected Outcome / Note |
|---|---|---|
| Gap Analysis | AI‑assisted gap mapping plus lead auditor review | Clear remediation roadmap; faster prioritisation |
| Implementation | Practical guidance on controls and supplier engagement | Less rework and aligned evidence collection |
| Stage 1/2 Audit | AI‑augmented audits delivered by professional auditors | Efficient validation and focused findings |
| Certificate Management | Certificate database and download services | Centralised access to issued certificates |
This table highlights where Stratlane’s AI‑driven audit capabilities and post‑certification services add value while keeping the focus practical. The next H3 sections describe step details and certificate lifecycle advice.
What is the step‑by‑step process for achieving ISO certification?
Start with a comprehensive gap analysis to identify nonconformities, then prioritise remediation and consolidate evidence. Next, complete a Stage 1 documentation review and a Stage 2 effectiveness audit leading to certification and surveillance cycles. Timelines vary by scope: a focused programme might include a 2–8 week gap‑analysis and remediation sprint, a documentation readiness check and a scheduled Stage 2 window; larger scopes take longer. To speed readiness: automate evidence collection, engage auditors early for alignment and use risk‑based priorities to focus on critical controls. Clear documentation, indexed evidence and pre‑audit internal reviews improve the chance of first‑pass success.
These operational steps lead into strategies for maximising ROI and managing certificate lifecycles effectively.
How can businesses maximise ROI and manage certificates effectively?
To maximise ROI from certification, measure outcomes like fewer incidents, improved customer satisfaction and faster contract wins. Certificate lifecycle management means secure storage, renewal scheduling and stakeholder visibility. An ROI checklist includes tracking incident‑reduction rates, contract conversion lift post‑certification and savings from streamlined processes. Certificate best practices are centralised repositories, automated renewal alerts and evidence‑ready documentation for surveillance audits. Stratlane supports these needs with a certificate database and AI‑assisted audit workflows that shorten audit time and help reduce compliance costs. Applying these practices accelerates value capture and keeps certificates current across renewal cycles.
This section closes the article after covering all planned topics and practical integrations.
Frequently asked questions
What is the significance of ISO 42001:2023 for organisations using AI?
ISO 42001:2023 gives organisations a practical, certifiable framework for managing AI responsibly. It clarifies expectations on ethical principles, lifecycle risk governance and traceability. Following the standard helps you document processes, run risk assessments and maintain oversight — steps that improve compliance readiness and build stakeholder trust.
How can organisations ensure compliance with the new ISO standards?
Start with a detailed gap analysis to map current practices to new requirements, then prioritise remediation by risk and update documentation. Invest in staff training and regular internal audits, and engage your certification body early for guidance. Treat compliance as an ongoing programme, not a one‑off project.
What are the benefits of integrating AI into ISO auditing processes?
AI speeds evidence collection and analysis, increases audit coverage and surfaces trends human reviewers might miss. It allows auditors to focus on judgement and context, reducing preparation time and enabling earlier corrective action. Proper model governance and human oversight are essential to avoid false positives and maintain audit quality.
How do the changes in ISO 14001:2025 impact environmental management practices?
ISO 14001:2025 tightens expectations around climate action, emissions accounting and circular‑economy measures. Organisations must set measurable objectives, run lifecycle assessments for key products and embed circularity into procurement and design. The result is more auditable EMS outputs that align with regulatory and stakeholder reporting.
What steps should organisations take to prepare for ISO 27001:2022 updates?
Conduct a comprehensive gap analysis, update risk assessments to reflect new control categories (cloud, software security, data lifecycle), revise your Statement of Applicability and refresh evidence repositories. Prioritise remediation for controls protecting critical assets and schedule audits to meet transition timelines. External expertise can speed the process.
How does the transition process for ISO certifications typically unfold?
Transitions follow a familiar sequence: gap analysis, remediation, Stage 1 documentation review, Stage 2 effectiveness audit, and ongoing surveillance. Each phase validates that controls are implemented and operating effectively. Planning, automation and early auditor engagement reduce friction and improve first‑pass success rates.
Conclusion
Keeping pace with ISO revisions is essential to protect market access, reduce risk and improve operational resilience. Understanding the key changes in ISO 9001, 27001, 14001 and 42001 lets you align systems with evolving regulatory and stakeholder expectations. Start now — run focused gap analyses, prioritise high‑impact remediations and engage auditors early. If you’d like help, explore our resources or contact Stratlane for hands‑on guidance through your certification journey.