What is ISO Certification? Key Insights for Newcomers
ISO Certification — A practical primer: benefits, common standards, and the path to certification
ISO certification is an independent, third‑party confirmation that an organisation’s management system meets the requirements of a specific ISO standard. In short: an accredited certification body reviews your processes, evidence and controls, then issues a certificate when those elements meet the standard. Certification reduces risk, brings consistency to operations and signals trust to customers and regulators. This guide breaks ISO certification down for newcomers — why companies pursue it, which standards are most common, and a clear, step‑by‑step route to certification. You’ll also find practical comparisons (including how AI is changing auditing), and side‑by‑side notes on ISO 9001, ISO 27001, ISO 14001 and the emerging ISO 42001 to help you choose next steps.
What is ISO Certification and why it matters
Put simply, ISO certification verifies that a management system — for quality, environment, or information security — conforms to a published ISO standard. The process is straightforward: an accredited certification body audits your systems and issues a certificate when evidence shows compliance. Organisations seek certification to win tenders, reduce variation in delivery, and make a formal commitment to managing risk and compliance. The sections that follow clarify who writes standards versus who issues certificates, and list the immediate, practical benefits that prompt organisations to start the certification journey.
ISO stands for the International Organization for Standardization. ISO develops and publishes international standards but does not certify companies — independent certification bodies carry out audits and award certificates. Standards are developed by global technical committees, agreed by consensus, and periodically reviewed so requirements stay current. Standards are referenced using identifiers such as ISO 9001:2015 (number and year indicate subject and revision) and include clauses on leadership, risk management and continual improvement. Knowing this split — ISO as standard‑setter and certifiers as assessors — helps you pick the right certification partner and maintain the value of your certificate.
Organisations typically pursue ISO certification for three measurable reasons:
- Stronger credibility: a certificate is documented assurance you meet recognised practices.
- Market access: many tenders and international supply chains require accredited certification.
- Greater operational resilience: standardised processes reduce errors and support continuous improvement.
Those drivers usually lead to a gap analysis and internal readiness checks — the practical first steps before implementation.
What does ISO do and what is its role?
The International Organization for Standardization is an independent, non‑governmental body that coordinates global standards across industries. Its role is to create consensus‑based standards that capture best practice and enable interoperability, safety and quality across borders. Standards are drafted by experts from industry, regulators and academia, then reviewed and updated to reflect technology and regulation. Organisations adopt ISO standards as a common framework for their management systems — but ISO does not perform certification; accredited third‑party organisations do.
Because ISO standards are neutral and internationally recognised, they form the backbone of trusted third‑party certification used in procurement and regulation. Understanding a standard’s structure — scope, normative references, terms and requirements — helps you map your existing processes to clauses and identify the documentation auditors will expect. Choosing an accredited certification body matters because accreditation confirms the certifier’s competence and impartiality, preserving your certificate’s recognition in international markets.
How ISO certification benefits your business
ISO certification turns standards into tangible business results: it aligns processes, clarifies roles and introduces regular measurement and review cycles. That consistency reduces defects, improves supplier oversight and gives you reliable metrics for continuous improvement. The impact shows up in procurement success, stronger customer relationships and operational efficiency — certified organisations often report fewer failures, clearer accountability and firmer proof of regulatory compliance. These gains deliver both immediate operational wins and long‑term strategic advantage.
Here’s a quick mapping of common benefits to measurable outcomes:
| Benefit | Measurable attribute | Business impact / example |
|---|---|---|
| Credibility | Certificate accepted in tenders | Higher tender success and new contracts |
| Efficiency | Fewer process deviations | Lower rework costs and faster delivery |
| Risk reduction | Documented risk assessments | Fewer compliance incidents and improved insurance position |
Linking benefits to metrics helps teams choose which standard to pursue and shapes how you present certification value to stakeholders. With clear objectives, you can move into implementation and audit planning with realistic cost‑benefit expectations.
Common types of ISO certification
A small set of ISO standards accounts for the majority of certification requests because they address core management needs. The standards most businesses consider are ISO 9001 (quality), ISO 14001 (environment), ISO 27001 (information security) and ISO 42001 (AI governance). Each focuses on different risks and outcomes, so pick the one that matches your priorities — product quality, data protection, environmental performance or responsible AI. The table below summarises purpose, typical requirements, who benefits and example use cases to help decision‑makers.
Quick comparison of commonly sought standards:
| Standard | Purpose | Typical requirements | Who benefits | Example use‑cases |
|---|---|---|---|---|
| ISO 9001 | Quality management | Process controls, customer focus, continual improvement | SMEs to large manufacturers | Consistent products, supplier performance |
| ISO 14001 | Environmental management | Identify environmental aspects, ensure compliance, set improvement plans | Manufacturers, facilities, service providers | Waste reduction, regulatory alignment |
| ISO 27001 | Information security | Risk assessments, ISMS controls, incident response | Any organisation handling sensitive data | Data protection, cloud services, finance |
| ISO 42001 | AI management | Governance, risk management, monitoring of AI systems | Tech firms and organisations deploying AI | Responsible AI, algorithm transparency |
This overview helps you match business drivers to the right standard. Next we cover practical steps to certification and how AI‑enhanced audits differ from traditional approaches.
What is ISO 9001 and how it improves quality management
ISO 9001 sets out requirements for a Quality Management System (QMS) designed to help organisations consistently meet customer and regulatory needs. It stresses customer focus, leadership commitment, a process approach and continual improvement using Plan‑Do‑Check‑Act. Implementing ISO 9001 typically means documenting key processes, assigning responsibilities, setting measurable quality objectives and establishing monitoring to track performance. The result: fewer defects, clearer supplier expectations and better customer satisfaction metrics that support retention and growth.
When preparing for ISO 9001, prioritise mapping processes that affect product or service quality, set measurable objectives and run internal audits to verify effectiveness. These steps prepare your team for the external assessment and build operational discipline that improves day‑to‑day performance. Typical audit evidence includes procedures, records and performance data — having those organised ahead of time reduces the chance of nonconformities during certification.
Why ISO 27001 matters for information security
ISO 27001 specifies requirements for an Information Security Management System (ISMS) using a risk‑based approach to identify and treat information risks. The standard requires systematic risk assessments, implementation of appropriate controls and ongoing monitoring and improvement. For organisations that hold customer data, intellectual property or core business systems, ISO 27001 provides a structured way to demonstrate strong data protection and support privacy compliance. An ISMS also clarifies incident response roles and documentation so recovery is faster and reputational damage is reduced.
The section below highlights how ISO 27001 structures information protection across different organisational settings.
ISO 27001 — an operational framework for information security
ISO 27001 provides a practical, scalable framework to help organisations of any size manage information security in a methodical and cost‑effective way. It is part of the ISO/IEC 27000 family and guides businesses through risk assessment, control selection and continual improvement to achieve and maintain certification.
Adopting ISO 27001 leads to clearer asset classification, tighter access controls and documented processes for vulnerability management and secure configuration. Those improvements reduce breach risk and make security spending easier to justify to boards, customers and insurers. The ISMS cycle ensures controls evolve as threats and business needs change — a vital advantage in today’s fast‑moving threat landscape.
How to get ISO certified — step‑by‑step
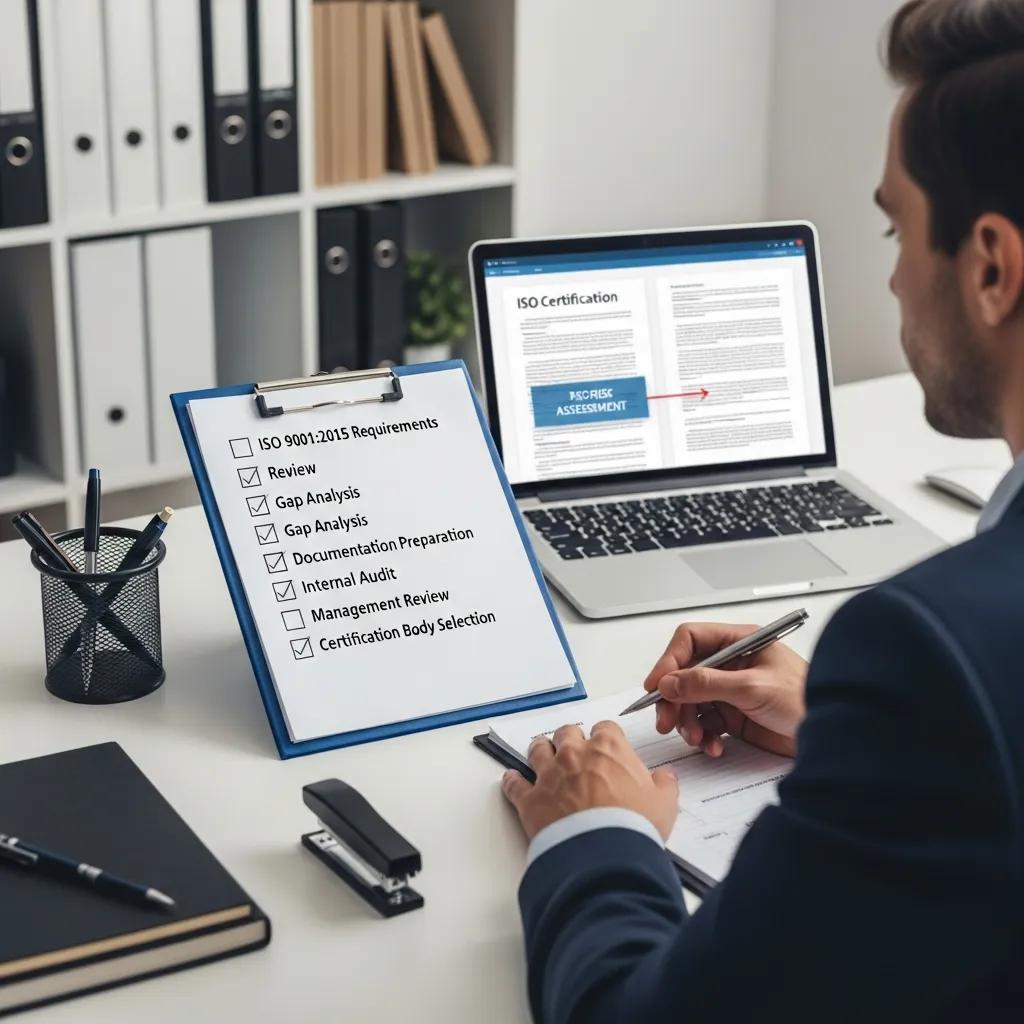
The certification path follows four phases: prepare, implement, audit and maintain. Preparation starts with a gap analysis that compares current practice to standard requirements and identifies documentation and process gaps. Implementation means creating policies, procedures and controls, then running internal audits and management review to confirm readiness. The external certification audit — carried out by an accredited body — checks conformity and, if successful, results in certificate issuance followed by surveillance audits to maintain certification. Each phase emphasises evidence collection and continual improvement so your management system stays effective over time.
Use this numbered checklist to plan the project and communicate with stakeholders:
- Run a gap analysis to map current practices to standard clauses and highlight priority actions.
- Create documentation and implement controls — policies, procedures, records and clear responsibilities.
- Conduct internal audits and a management review to confirm readiness and close nonconformities.
- Engage an accredited certification body for the external audit (stage 1 documentation review, stage 2 full assessment).
- Resolve any audit findings, obtain the certificate, and schedule surveillance audits with ongoing improvement activities.
These are the conventional steps; AI‑driven auditing is changing how evidence is analysed and reported, which we compare in the following table.
Audit‑phase comparison: the table below contrasts traditional and AI‑enhanced approaches, typical durations and expected outputs so you can see where technology adds value and where human judgement stays central.
| Phase | Traditional approach | AI‑enhanced approach | Typical duration | Key outputs |
|---|---|---|---|---|
| Gap Analysis | Manual document review and interviews | Automated document parsing and KPI gap highlights | 1–3 weeks | Gap report, prioritised actions |
| Implementation | Human‑led process updates | AI suggests control templates and evidence mapping | 2–6 months | Documented procedures, evidence list |
| Internal Audit | Sample‑based interviews and record checks | Broader sampling via data analytics and NLP review | 1–4 weeks | Internal audit findings, corrective plans |
| External Audit | On‑site sampling and evidence review | Hybrid on‑site assessment plus AI evidence aggregation | 1–5 days (assessment) | Certification decision, audit report |
| Surveillance | Annual or periodic manual checks | Continuous monitoring alerts plus periodic review | Ongoing | Surveillance reports, alerts |
The table shows AI’s strengths in scaling evidence review and surfacing anomalies while human auditors retain responsibility for interpretation and context. Next, we summarise the ISO 9001‑specific steps teams commonly follow.
Key steps in the ISO 9001 certification process
The ISO 9001 route focuses on documenting processes that affect product or service quality and proving they work with objective evidence. Typical actions: map core processes, produce a quality manual and procedures, define metrics and objectives, train staff, run internal audits and hold management reviews to close gaps before the external audit. Common pitfalls are under‑documenting, failing to measure objectives properly, and not showing corrective action for findings. For many small and medium organisations, a realistic timeline from gap analysis to external audit is three to six months, depending on complexity and resources.
When gathering evidence, prioritise records that show consistent operation — control charts, monitoring logs, supplier evaluations and nonconformity records — since auditors frequently sample these. Readiness signs include completed internal audits with closed findings, a documented management review and measurable progress against quality objectives. These checks reduce the risk of major nonconformities at certification and smooth the path to issuance.
How AI‑driven auditing enhances the certification process
AI‑driven auditing complements traditional audit work by automating evidence aggregation, detecting patterns across larger datasets and using natural language processing to flag inconsistencies in documentation. That increases sampling breadth, reduces time spent on routine evidence checks and highlights anomalies that deserve auditor attention — improving speed and accuracy. Crucially, AI acts as an assistant, not a replacement: human judgement remains essential for context, risk assessment and final certification decisions. In practice, AI frees auditors to focus on high‑risk areas and improves overall audit quality.
With modern certification providers, AI‑assisted workflows can parse policies and logs to create an evidence map, flag potential control gaps and generate an initial report for auditor review. If you’re ready to explore a hybrid audit, many certifiers offer direct options to Book your audit or Request a Get A Quote to begin scoping a blended assessment.
Benefits of ISO certification for different organisations
ISO certification brings value across company sizes and sectors, though the emphasis varies. SMEs often pursue ISO 9001 or ISO 27001 to access new clients and public tenders where certification is required. Larger organisations may pursue multiple standards to harmonise supplier management, environmental performance and data security across regions. Research and academic bodies may prioritise ISO 27001 for data protection or ISO 42001 as AI governance becomes central. Mapping benefits to measurable outcomes helps stakeholders decide which standard to implement first and what KPIs to track.
Here’s a benefits table tying common gains to measurable attributes and business impact:
| Benefit | Measurable attribute | Business impact / example |
|---|---|---|
| Tender eligibility | Certificate recognised by procurers | Access to new revenue streams |
| Operational efficiency | Reduced cycle time / error rate | Lower costs and faster delivery |
| Risk management | Fewer incidents / less downtime | Reduced financial and reputational loss |
| Supplier performance | On‑time delivery rate | Improved supply chain reliability |
These mappings support investment decisions and help teams set realistic KPIs for post‑certification monitoring. The next sections explain how certification improves credibility and operational performance in practice.
How ISO certification increases credibility and market access
A certified management system signals to customers, partners and procurement teams that your organisation follows recognised best practices. That often removes barriers in competitive tendering and international supply chains. Certification provides auditable proof that processes are controlled and risks are managed — a common trust criterion for buyers. For exporters and suppliers to multinationals, accredited certificates simplify vendor qualification and can shorten onboarding timelines. Displaying certificates and offering validity checks on proposals reinforces trust during commercial evaluations.
Because certification is frequently a market prerequisite, achieving and maintaining accredited status directly expands opportunity. Track metrics such as tender win rate and new‑client conversion after certification to quantify market access benefits; those figures feed back into your continual improvement cycle.
Operational improvements ISO certification delivers
ISO‑based management systems create operational consistency by codifying processes, assigning responsibilities and adding measurement systems that spot deviations early. Typical improvements include lower process variability, fewer customer complaints, better supplier performance and clearer escalation paths for corrective action. These gains are measurable — reduced defect rates, lower rework costs and improved throughput times — and they directly improve margins and customer satisfaction. Regular internal audits and management reviews keep these improvements on track and surface new optimisation opportunities.
Formalised supplier management — selection criteria, performance reviews and documented agreements — reduces supply chain surprises. As operations stabilise under a management system, teams can shift energy from firefighting to strategic work like product innovation or market expansion, creating compounding value over time.
Why choose Stratlane for ISO certification?
Stratlane Certification is an accredited certification body operating in 27+ countries, offering ISO 9001, ISO 14001, ISO 27001 and ISO 42001 services. We combine accreditation and global reach with AI‑augmented auditing tools and local audit teams across Europe and the UK to deliver consistent, efficient assessments. Our service suite includes centralised certificate management — a searchable certificate database, validity checks and authorised downloads — to support tenders and marketing needs. If you want a partner that blends technology into the audit workflow while preserving accredited third‑party assessment, Stratlane offers a practical, time‑saving approach that extends audit coverage.
Stratlane’s model emphasises auditor expertise supported by AI tools that aggregate evidence and detect anomalies without replacing human judgement. That increases sampling breadth and report clarity while keeping certification decisions with trained auditors. Organisations can engage through clear next steps: Request a Get A Quote or choose to Book your audit — both start a structured intake and scoping process to align certification with business priorities.
What makes Stratlane’s AI‑driven auditing different?
Stratlane’s AI‑driven audit toolkit combines automated document parsing, data analytics and anomaly detection to streamline pre‑audit work and support auditors on site. The AI aggregates evidence across systems, surfaces inconsistencies for targeted inspection and drafts reporting that auditors validate — typically shortening administrative time. Importantly, AI increases auditor effectiveness by expanding sampling and revealing patterns humans may miss, while auditors retain authority to classify nonconformities and decide certification outcomes. This hybrid model boosts efficiency without diluting the contextual judgement needed for robust certification.
Clients using AI‑augmented audits report faster readiness assessments and clearer corrective action guidance, enabling quicker gap closure. If you’re exploring this workflow, Stratlane supports scheduling and scoping via our quote and booking processes.
How Stratlane supports certificate management and global accreditation
After certification, Stratlane provides certificate management services to simplify validity checks and marketing use: a central certificate database allows authorised downloads, and validation tools support tender submissions where proof of accreditation is required. Our accreditation footprint across 27+ countries helps ensure cross‑border recognition and eases vendor qualification in international supply chains. Practical support includes issuance workflows, accessible records for stakeholders and surveillance planning to maintain compliance and readiness for renewal.
These services reduce administrative friction and keep your organisation audit‑ready for tenders and inspections. If certificate management and long‑term compliance are priorities, Stratlane’s accredited network and service set give you an integrated path from first audit to ongoing surveillance.
Ready to get certified? next steps with Stratlane
Start with a focused gap analysis and a prioritised action plan that addresses the most critical clauses of your chosen standard. If you’re interested in an AI‑augmented audit path and centralised certificate management, Stratlane provides accredited services, cross‑country audit capability and post‑certification support to simplify procurement and marketing requirements. To move forward, Request a Get A Quote to scope your project or Book your audit to schedule a readiness assessment and external audit. Those first steps turn the promise of certification into measurable business results and sustained operational improvement.
Frequently asked questions
What’s the difference between ISO standards and certification bodies?
ISO standards are consensus‑based documents created by the International Organization for Standardization that describe best practices for different management systems. Certification bodies are independent, accredited organisations that assess whether a company’s management system meets a specific ISO standard and issue certificates when requirements are met. ISO writes the standards; third‑party certifiers perform audits and award certification.
How long does the ISO certification process usually take?
Timing varies with organisation size, complexity and readiness. Typically, the full process — gap analysis, implementation, internal audits and external certification audit — takes around three to six months. Organisations with existing management systems and good preparation can often move faster; those starting from scratch will need more time.
What costs are involved in getting ISO certified?
Costs vary by organisation size, system complexity and the chosen certification body. Typical expenses include certification body fees, internal audit and training costs, and any implementation work needed to meet the standard. Treat certification as an investment in operational efficiency and market credibility when budgeting.
Can small businesses benefit from ISO certification?
Yes. Small businesses often use ISO 9001 or ISO 27001 to compete for tenders and win clients that require certified suppliers. Certification also helps streamline processes, reduce errors and improve efficiency, which can lower costs. Adopting ISO standards signals a commitment to quality and continuous improvement that strengthens customer trust.
What role does continuous improvement play in ISO certification?
Continuous improvement is central to ISO standards, especially ISO 9001. Organisations must regularly review and improve their management systems by setting measurable objectives, monitoring performance and taking corrective action when needed. A culture of continuous improvement helps organisations adapt, stay compliant and enhance efficiency over time.
How does AI affect the ISO certification process?
AI is improving audit efficiency and accuracy by automating evidence collection, analysing large datasets for patterns and spotting documentation inconsistencies. This lets auditors focus on high‑risk areas and increases assessment quality. AI augments the audit process; human judgement remains essential for interpretation and certification decisions.
What should organisations do after achieving ISO certification?
After certification, focus on maintaining compliance and continuous improvement: perform regular internal audits, hold management reviews and participate in surveillance audits as required. Track performance metrics to find improvement opportunities and run ongoing training to keep staff aligned with the management system. These activities preserve certification value and support long‑term operational gains.
Conclusion
ISO certification brings clear benefits: stronger credibility, improved operational efficiency and broader market access. By aligning processes with widely recognised standards, organisations demonstrate a commitment to quality and risk management that boosts customer confidence and competitive positioning. Taking the first step toward certification — a focused gap analysis and a practical action plan — can deliver measurable improvements. To explore how ISO certification can work for your organisation, Request a Get A Quote or Book your audit today.