Build Resilience: Master Crisis Management with ISO 22301
Build operational resilience with ISO 22301 certification
Business resilience is an organization’s ability to anticipate, prepare for, respond to, and recover from disruption while keeping critical operations and stakeholder confidence intact. This guide shows how ISO 22301 — the international standard for Business Continuity Management Systems (BCMS) — turns resilience into a repeatable, auditable capability. You’ll get a clear view of the standard’s requirements, the tangible benefits of certification, a PDCA-based implementation roadmap, how AI-assisted audits change the certification lifecycle, and how continuity planning ties into crisis response and disaster recovery. If downtime, supplier interruptions, or unclear recovery priorities threaten your operations, this article gives practical steps to prioritize assets, set recovery objectives, and validate plans to cut downtime and compliance risk. Sections cover the standard’s scope and structure; measurable benefits and cost impacts; step-by-step implementation; AI-enabled auditing; BCMS alignment with incident response and DR; and who should pursue certification and how to start with a qualified partner. Throughout, we link BCMS, business impact analysis (BIA), PDCA, incident response, and AI-driven auditing to real-world decision making.
What ISO 22301 is — and why it matters for resilience
ISO 22301 defines the requirements for a Business Continuity Management System that helps organizations plan for, respond to, and recover from disruptive incidents. By requiring risk assessment, business impact analysis (BIA), documented continuity plans, and management review inside a PDCA framework, the standard moves resilience from ad hoc firefighting to a governed, auditable process. Certification signals to customers, regulators, and partners that you’ve set recovery priorities and tested your objectives, reducing uncertainty and financial exposure. Consider ISO 22301 when downtime, supply-chain fragility, regulatory rules, or contract obligations create material risk — the standard standardizes how you set priorities and allocate resources. The next section explains the BCMS concept and the core components you’ll need to assemble.
What a BCMS looks like under ISO 22301
A BCMS is a coordinated set of policies, procedures, people, and technology designed to keep critical functions running or restore them quickly after disruption. ISO 22301 requires you to define scope and context, assign leadership and roles, run a BIA and risk assessment, pick continuity strategies, and document incident response, recovery, and communications procedures. Core BCMS artifacts include a continuity policy, process-level procedures, recovery teams and owners, emergency contact lists, recovery time objectives (RTOs), and training/exercise logs that prove preparedness. For example, a BCMS may prioritize finance, communications, and operations; appoint recovery owners; and schedule quarterly tabletop exercises to validate procedures. Knowing these elements helps teams convert BIA outputs into targeted recovery actions and measurable objectives — a theme we continue when we outline the standard’s clauses and principles.
Core principles and scope in practice
ISO 22301 maps to familiar management-system clauses: context, leadership, planning, support, operation, performance evaluation, and improvement. Its core principles are leadership commitment, risk-based planning, documented operational controls, competence and awareness, evidence-based records, and continual improvement through PDCA. The standard fits organizations of any size and lets you set scope boundaries (products, sites, services) and justify exclusions. That means small firms can apply proportionate controls to critical processes, while larger organizations often integrate BCMS with existing systems. Mapping clauses to day-to-day activities helps teams focus effort where audits and operations intersect — the implementation guide that follows shows how to do that practically.
What certification delivers: measurable benefits for your business
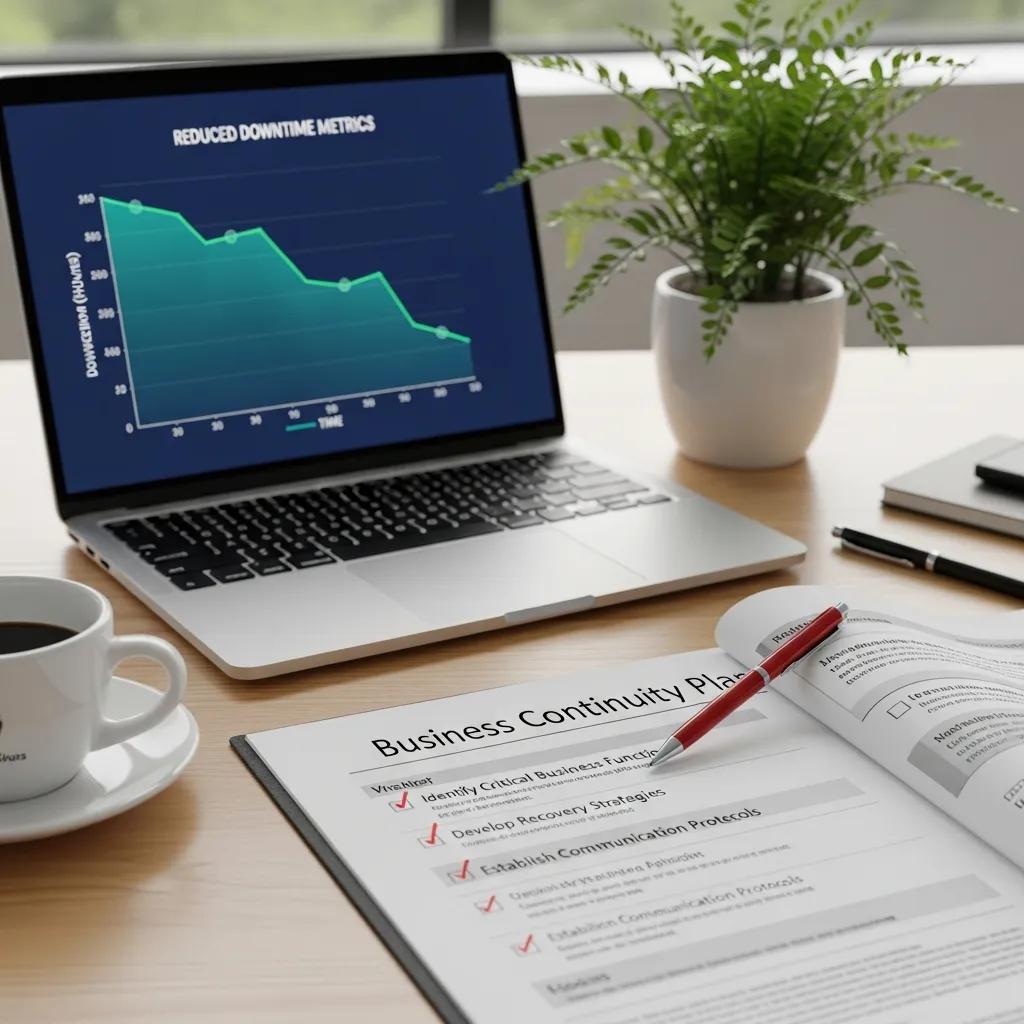
ISO 22301 certification delivers concrete benefits: less downtime, clearer recovery priorities, and greater stakeholder confidence backed by independent verification. Certification converts reactive behavior into a repeatable, auditable system that supports contractual and regulatory requirements, safeguards reputation, and can reduce insurance and outage-related costs. Below are the primary benefits and the mechanisms that produce measurable outcomes and KPIs.
- Faster recovery, less downtime: Prioritized recovery plans and tested procedures shorten mean time to recovery (MTTR) so services return faster.
- Regulatory and contractual certainty: A certified BCMS demonstrates due diligence to regulators and customers and supports continuity clauses in contracts.
- Operational efficiency and cost control: Standardized processes and risk-based investments reduce duplicated controls and avoid expensive emergency fixes.
- Stronger stakeholder trust: Independent certification shows preparedness and helps protect customer relationships during incidents.
Tracking outcomes quantitatively makes these benefits actionable. The table below links benefits to mechanisms and measurable outcomes so decision makers can set realistic KPIs.
Certification benefits operate through distinct mechanisms and produce specific business improvements.
| Benefit | Mechanism | Outcome / Metric |
|---|---|---|
| Reduced Downtime | Recovery objectives defined by BIA | Lower MTTR; fewer SLA breaches |
| Compliance Confidence | Documented controls and independent audit | Fewer regulatory findings; contract retention |
| Cost Efficiency | Streamlined incident workflows and exercises | Lower emergency spend; better resource allocation |
| Reputational Protection | Third‑party certification and tested plans | Improved stakeholder trust; reduced churn after incidents |
This comparison shows how structured BCMS practices translate to measurable reductions in risk and cost. Next we explain how the standard strengthens resilience through risk management and BIA.
How ISO 22301 improves resilience and risk management
ISO 22301 forces a systematic approach to identify and prioritize critical activities via BIA and risk assessment, so you can focus mitigation and recovery where it matters most. A BIA quantifies financial and operational impacts per process and sets recovery time and point objectives (RTO/RPO) to guide your strategy. Risk assessment layers likelihood and consequence to target controls at high-impact scenarios — for example, aligning redundancy to key suppliers or services. Cross-functional planning prevents silos: IT disaster recovery, physical security, and vendor management should all align with BCMS objectives to create coherent recovery paths. That lets leadership invest limited resources in the highest-value resilience steps and measure results with meaningful KPIs.
Compliance wins and cost savings you can expect
Certification typically reduces exposure to fines and contractual penalties by documenting capabilities and proving readiness in audits, while lowering direct costs tied to unplanned downtime. Common savings come from smaller emergency vendor premiums, fewer expedited shipments or overtime, and lower insurance rates when underwriters recognize a formal BCMS. Useful KPIs include MTTR, continuity incidents per year, percentage of critical processes with tested RTOs, and cost per incident. Tracking these figures before and after BCMS rollout builds a quantifiable business case and helps prioritize exercises and automation where ROI is highest. That leads into a practical, PDCA-aligned implementation roadmap.
Implementing ISO 22301: a step-by-step BCMS roadmap
Implementation follows a PDCA project: scope and gap analysis, risk and impact assessment, strategy and plan development, then testing and continuous improvement. The steps below provide a clear sequence teams can follow to move from readiness to certified BCMS.
- Define scope and secure leadership buy‑in: Document what the BCMS covers and get executive sponsorship.
- Run gap analysis and BIA: Identify critical activities, dependencies, and acceptable downtime.
- Assess risks and choose strategies: Score threats and select mitigation and recovery options.
- Write plans and procedures: Document incident response, recovery, and communication steps with owners assigned.
- Test, exercise, and review: Use tabletop exercises and live tests, then update plans based on findings.
- Embed continual improvement: Feed audit results, incidents, and management reviews into corrective actions.
These steps mirror ISO 22301 clauses and form a PDCA approach that balances governance with operational readiness. The table below maps clauses to practical deliverables so teams can turn requirements into audit-ready outputs.
| Clause Area | Requirement | Deliverable |
|---|---|---|
| Context & Scope | Define organizational context and BCMS scope | Scope statement, stakeholder register |
| Leadership | Top management commitment and roles | Policy, appointed BCMS manager, roles matrix |
| Planning | Risk assessment and objectives | Risk register, BIA report, recovery objectives |
| Support & Operation | Resources, procedures, and controls | Continuity procedures, training records, communication templates |
| Performance Evaluation | Monitoring and internal audit | Audit schedule, exercise reports, management review minutes |
| Improvement | Nonconformity handling and corrective actions | Corrective action log, improvement plan |
This mapping helps teams produce deliverables that serve as audit evidence and enable continuous improvement. Next we outline the PDCA cycle in daily BCMS operations and the documentation auditors expect.
PDCA in practice: essential requirements and records
Plan: set a continuity policy and scope, run BIA and risk assessment, and set objectives. Do: implement strategies, assign roles, document procedures, and train teams. Check: monitor performance, run internal audits, and exercise plans to validate effectiveness. Act: implement corrective actions, conduct management review, and update plans. Key documents auditors look for include the BCMS policy, BIA report, risk register, continuity procedures, exercise logs, and audit records. Strong record-keeping and version control demonstrate continual improvement during audits. Applying PDCA regularly ensures lessons from exercises and incidents are fed back into controls — which leads us to how risk assessments and BIAs should be run.
Research reinforces PDCA’s role as the backbone of effective crisis management within a BCMS.
BCMS Lifecycle: PDCA for Crisis Management
Business continuity management provides the structure organizations need to plan for and respond to unexpected events — from natural disasters to technical failures. Applying a systemic BCMS approach, based on the PDCA cycle, helps identify critical processes and define actions to secure and restore them. This paper demonstrates how the BCMS lifecycle and PDCA are applied in a military context, showing managed activation and evaluation of resources during emergency response.
Application of business continuity management system into the crisis management field, H Malachová, 2016
Running effective risk assessments and BIAs
Good risk assessments classify threats by likelihood and impact and link them to the assets and processes identified in the BIA. A BIA quantifies downtime consequences across financial, operational, legal, and reputational dimensions. Steps: identify critical activities, map dependencies (people, systems, suppliers), estimate downtime impacts, and set RTO/RPO targets. Use a simple risk matrix to score scenarios and prioritize recovery strategies where impact and likelihood intersect. Involve stakeholders across functions to validate dependencies; documented sign-off strengthens audit evidence. Convert outputs into prioritized, tested recovery actions so plans are usable under pressure — and consider how modern audit tools, including AI, can streamline evidence collection and maintain continuous compliance.
How AI-driven auditing changes ISO 22301 certification
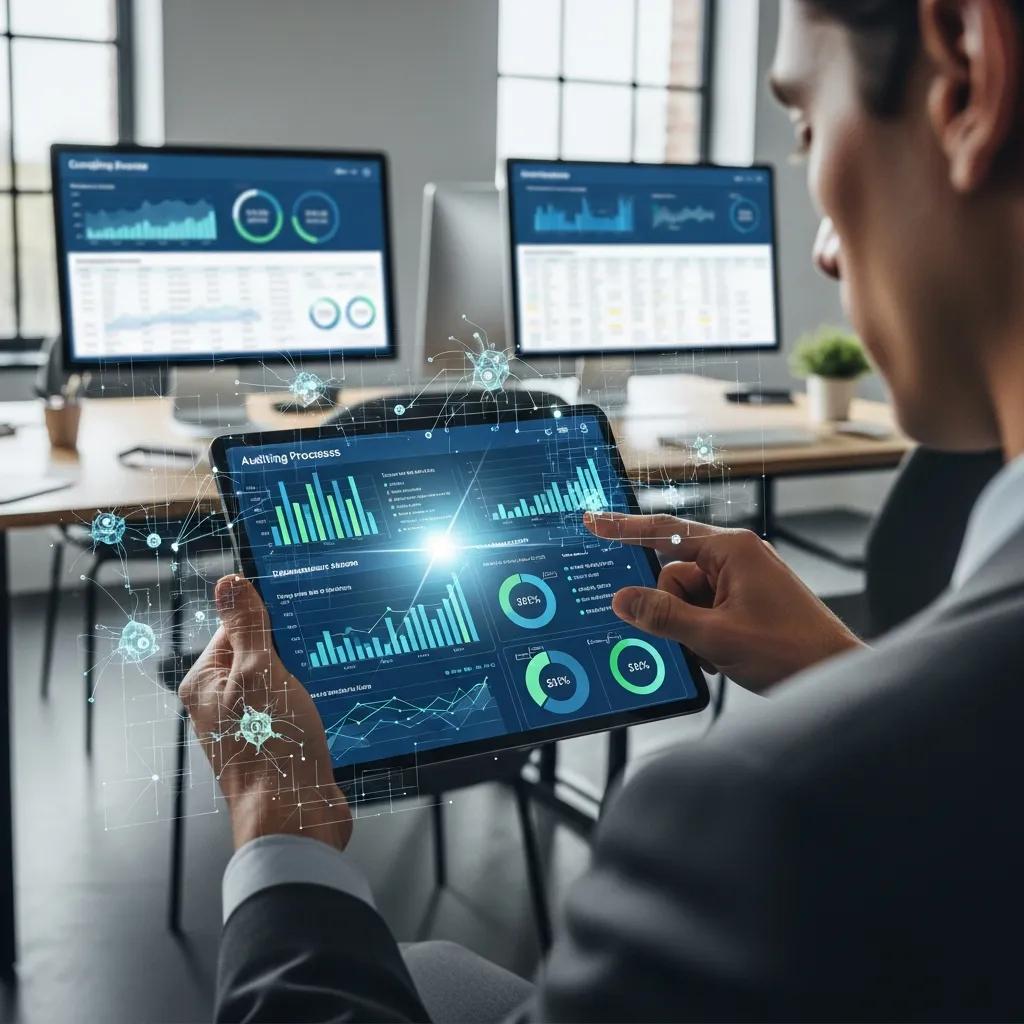
AI-driven auditing speeds ISO 22301 certification by automating evidence collection, surfacing patterns that reveal latent risks, and enabling remote or continuous audit models that lower on-site time and cost. Machine-assisted tools can match control evidence (policies, logs, test results) to clause requirements to highlight gaps and prioritize remediation. Predictive analytics spot recurring weaknesses before they become formal nonconformities, while automated indexing and anomaly detection accelerate auditor review. These capabilities make audits more focused on high-risk areas, improve accuracy, and free human auditors to use judgment on nuanced issues. Below we list concrete AI advantages and the improvements organizations can expect.
AI advantages: efficiency, accuracy, and clarity
AI reduces repetitive checks, improves consistency in evidence evaluation, and surfaces anomalies that human reviewers may miss — lowering error rates and speeding report generation. Automated evidence matching can cut manual review hours, pattern recognition highlights recurring issues across cycles, and AI dashboards provide near-real-time compliance views for continuous monitoring. Faster reports and prioritized findings let teams concentrate corrective actions where they yield the biggest risk reduction, improving audit return on investment and making the audit process less disruptive and more actionable.
Below is a concise mapping of AI features to audit improvements and tangible benefits.
| AI Feature | Audit Improvement | Benefit / Example |
|---|---|---|
| Automated evidence aggregation | Faster evidence collection | Less auditor time on-site; a consolidated audit trail |
| Anomaly detection | Earlier nonconformity identification | Fewer surprise findings during formal audits |
| Predictive analytics | Risk prioritization | Focused remediation reduces repeat issues |
| Continuous monitoring dashboards | Ongoing compliance visibility | Shorter remediation cycles; clearer management reporting |
These examples show how targeted AI features convert into concrete audit improvements and business value. Next, we explain how a provider can put these capabilities into practice.
How Stratlane’s AI audit tools support continuous compliance and lower cost
Stratlane Certification combines AI-driven tooling with experienced auditors to streamline BCMS certification while preserving strong assurance. Automated evidence collection and AI-assisted gap analysis reduce manual audit effort and support remote or hybrid audit models that cut travel and scheduling costs. Stratlane provides audit planning, accredited auditors across jurisdictions, and certificate management workflows that guide organizations from quote to certificate download with clear milestones. Accredited to issue certificates in over 27 countries and with auditors operating in 29+ countries, Stratlane aligns AI tools with global accreditation rules to support continuous compliance and scalable certificate management. The result is a shorter, lower-cost path from readiness assessment to certification — useful context when you evaluate certification partners and plan next steps.
How ISO 22301 supports crisis management and disaster recovery
ISO 22301 gives you a governance framework that ensures incident response and disaster recovery are planned, documented, and tested as part of an auditable BCMS. The standard requires defined incident roles, communication templates, escalation criteria, and integration between IT disaster recovery and operational continuity. Testing validates both incident response and DR plans and captures lessons that feed into corrective actions. Embedding incident management in the BCMS reduces ambiguity in a crisis, improves cross‑functional coordination, and helps ensure recovery actions reflect the priorities set in your BIA.
ISO 22301’s role in incident response planning
The standard guides incident response by requiring clear roles, escalation paths, and documented communications that align with BIA-defined recovery objectives. An effective incident response plan includes detection and activation criteria, emergency contacts, responsibilities for containment and escalation, and prewritten external communications for stakeholders and regulators. Regular tabletop exercises uncover gaps and generate exercise logs and corrective actions that form part of the audit trail. Linking response actions to prioritized recovery tasks makes sure resources go where they reduce the most harm and helps integrate IT disaster recovery into broader continuity efforts.
Bridging disaster recovery and business continuity
Integrating IT disaster recovery (DR) with BCMS work means aligning RTO/RPO values across business and technical owners, documenting supplier continuity plans, and running coordinated tests that validate end‑to‑end recovery. Practical steps include mapping application dependencies to business processes, agreeing shared recovery objectives, embedding backup and failover strategies in continuity procedures, and scheduling joint DR/BCMS exercises. Include supplier continuity checks and contractual clauses in procurement so external partners support recovery targets. Coordinated testing uncovers hidden dependencies and confirms DR technology meets operational needs identified in the BIA — essential preparation before choosing a certification path and provider.
Who should pursue ISO 22301 and how to get started with Stratlane
ISO 22301 suits many organizations, especially where service availability, regulation, or supply‑chain continuity are critical. Finance, healthcare, utilities, transportation, and logistics often require formal continuity arrangements; SMEs can also use certification to win contracts and control outage costs. The decision depends on risk exposure, contract obligations, and the strategic value of resilience. For teams ready to act, the following section lists priority industries and SME use cases to help scope your project.
Industries and SME scenarios that gain the most
Sectors with high operational, financial, or safety consequences from downtime benefit most: finance and banking need transaction continuity; healthcare requires access to patient records and services; utilities and critical infrastructure affect societal safety; and logistics providers work across partner networks where disruptions cascade. SMEs in these areas can use certification to show contractual readiness, reduce client churn risk, and make outage costs more predictable. Organizations relying on third‑party platforms or complex supplier networks benefit from a BIA that clarifies dependencies and supports stronger SLAs and supplier resilience strategies. These drivers help define project scope and the justification for certification.
How to request a quote and book an ISO 22301 audit with Stratlane
Starting certification with Stratlane follows a straightforward sequence: request a quote with scope details, complete a readiness assessment or gap analysis, schedule a pre‑audit or initial certification audit, then progress to the certification audit and certificate issuance with certificate management. Provide scope, number of sites, headcount involved in continuity activities, and existing documentation to get an accurate quote and audit plan. Typical timelines include planning and readiness, scheduled audits, and post‑audit certificate management for multi‑country accreditation. Stratlane pairs AI tools with experienced auditors to streamline planning and evidence collection so organizations move efficiently from quote to certificate download while keeping compliance across jurisdictions. To accelerate planning, prepare scope documents, BIA and risk registers, and exercise logs before requesting a quote.
- Prepare scope and key documents: BIA, risk register, continuity policy.
- Request a quote with scope details: List sites, services, and expectations.
- Schedule readiness review and audit dates: Agree on remote, hybrid, or on‑site model.
- Complete audit and certificate management: Receive findings and certified BCMS evidence.
These steps clarify what teams must prepare and the timelines to expect for a smooth certification journey. Below is a concise call to action for teams ready to engage a certification partner.
If you’re ready to pursue ISO 22301, Stratlane Certification combines AI-assisted audit planning with auditors operating in 29+ countries and accreditation to issue certificates in over 27 countries. Prepare your scope, BIA, and key continuity records to request a quote and begin scheduling audits with transparent timelines and clear deliverables.
Frequently Asked Questions
Who should consider ISO 22301 certification?
Any organization facing material operational risk should evaluate ISO 22301. It’s especially relevant for sectors where uptime, safety, or regulatory compliance are critical — finance, healthcare, utilities, logistics — but SMEs can also use certification to demonstrate reliability and win business. If downtime or supplier failure would significantly impact customers or contracts, certification is worth considering.
How can organizations measure BCMS effectiveness after implementation?
Measure BCMS performance with KPIs such as mean time to recovery (MTTR), number of continuity incidents per year, percentage of critical processes with tested RTOs, and cost per incident. Regular internal audits, exercises, and management reviews also indicate effectiveness. Tracking these metrics over time supports continuous improvement and shows the business value of the BCMS.
What role does leadership play in successful ISO 22301 implementation?
Leadership is essential. Top management must provide resources, define scope, set policy, and demonstrate ongoing commitment. Their sponsorship ensures continuity planning aligns with strategic goals, secures budget, and drives organization-wide engagement. Leadership also reinforces a culture of preparedness through training and visible support for the BCMS.
How often should organizations audit their BCMS?
Conduct internal audits at least annually and more often if major changes occur. External certification audits follow the chosen certification cycle but maintain regular internal checks after incidents or exercises. Frequent reviews help spot gaps early and keep the BCMS responsive to evolving risk.
What common challenges appear during ISO 22301 implementation?
Typical challenges include gaining leadership buy‑in, allocating resources, and securing company‑wide engagement. Teams sometimes struggle with accurate BIAs and risk assessments. To overcome these hurdles, invest in training, communicate clear benefits, and involve stakeholders across functions so plans reflect real dependencies and operational needs.
How does ISO 22301 integrate with other management systems?
ISO 22301 integrates well with standards like ISO 9001 (quality) and ISO 27001 (information security). Integration reduces duplicate processes, aligns objectives, and improves efficiency. By mapping common clauses and controls, organizations can create a unified governance framework that supports resilience across functions.
Conclusion
ISO 22301 certification gives organizations a structured, auditable way to reduce downtime, strengthen response capabilities, and meet regulatory and contractual requirements. Adopting the standard builds stakeholder confidence and aligns incident response, DR, and business priorities. If you’re ready to strengthen resilience, engage a qualified certification partner to guide scope, readiness, and audit planning. Start the journey toward a more resilient operation by exploring certification options and preparing your key continuity records.