Conducting a Security Risk Analysis for ISO 27001:2022
ISO 27001:2022 Risk Assessment: Building an Auditable ISMS
An ISO 27001:2022 risk assessment is a repeatable, auditable process that identifies, analyzes, evaluates and records risks to information assets so an organization can operate a defensible ISMS. This guide explains why a rigorous assessment matters for compliance and resilience, and how modern techniques — including AI-assisted analysis — improve accuracy and consistency. You’ll find a clear walk-through of Clause 8.2 requirements, methodology choices, practical asset and threat discovery tips, steps to build a living risk register, and how to turn findings into a risk treatment plan mapped to Annex A. We also cover audit‑readiness practices and tooling approaches that cut manual work while preserving traceable evidence. Follow these sections to get templates, comparison guides, and checklists that make your risk assessment repeatable and defensible.
Practitioners often combine ISO 27001:2022 with complementary frameworks such as ISO 31000:2018 to broaden the risk management context and align enterprise risk practices with information security analysis.
Information Security Risk Analysis with ISO 27001:2022 & ISO 31000:2018
This paper examines information security risks at the Central Statistics Agency (BPS) of Lhokseumawe by applying ISO/IEC 27001:2022 and ISO 31000:2018. The authors use a descriptive qualitative approach with a case study to compare the standards’ practical fit.
Information Security Risk Analysis Using ISO 31000: 2018 and ISO 27001: 2022, A Ulya, 2018
What are the core requirements of ISO 27001 Clause 8.2 for risk assessment?
Clause 8.2 expects organizations to operate a documented, repeatable risk assessment process that sets the context and criteria, defines the chosen methodology, identifies and analyzes risks, evaluates them against acceptance thresholds, and retains records of decisions. The outcome must provide evidence that risks were assessed against organization‑specific criteria and that the results informed risk treatment choices — preserving traceability and auditability. In practice, auditors look for a written methodology, a populated risk register, and decision records showing how analysis led to treatment actions. Knowing these expectations upfront helps teams design assessments that meet both compliance and operational needs while enabling continuous improvement.
Quick reference: the following list captures Clause 8.2’s core deliverables.
- Documented assessment context and risk acceptance criteria set by the organization.
- A chosen and recorded risk assessment methodology aligned to scope and risk appetite.
- Identified assets, threats and vulnerabilities with traceable evidence sources.
- Analyzed and evaluated risks to establish likelihood, impact and prioritization.
- Results recorded in a risk register with retained records of analysis and decisions.
Those bullets summarize auditor expectations; next we unpack Clause 8.2 into practical steps and ownership for each stage of the process.
How does Clause 8.2 define the risk assessment process?
Clause 8.2 frames risk assessment as an organizational activity that starts with context, scope and criteria, then moves through identification, analysis and evaluation before recording results. Practically, teams should document who owns each activity, how often assessments run, and which data sources (inventories, scans, threat feeds) are used so the process is reproducible. The approach should specify qualitative or quantitative scoring rules and a residual‑risk acceptance threshold tied to governance. Good practice also captures assumptions, limitations and the evidence chain — items auditors will check to confirm the assessment produced defensible outcomes.
Clear role definitions and scope upfront prevent ambiguity later and ensure the risk register reflects the decisions made during analysis.
What documentation is required for an ISO 27001 risk assessment?
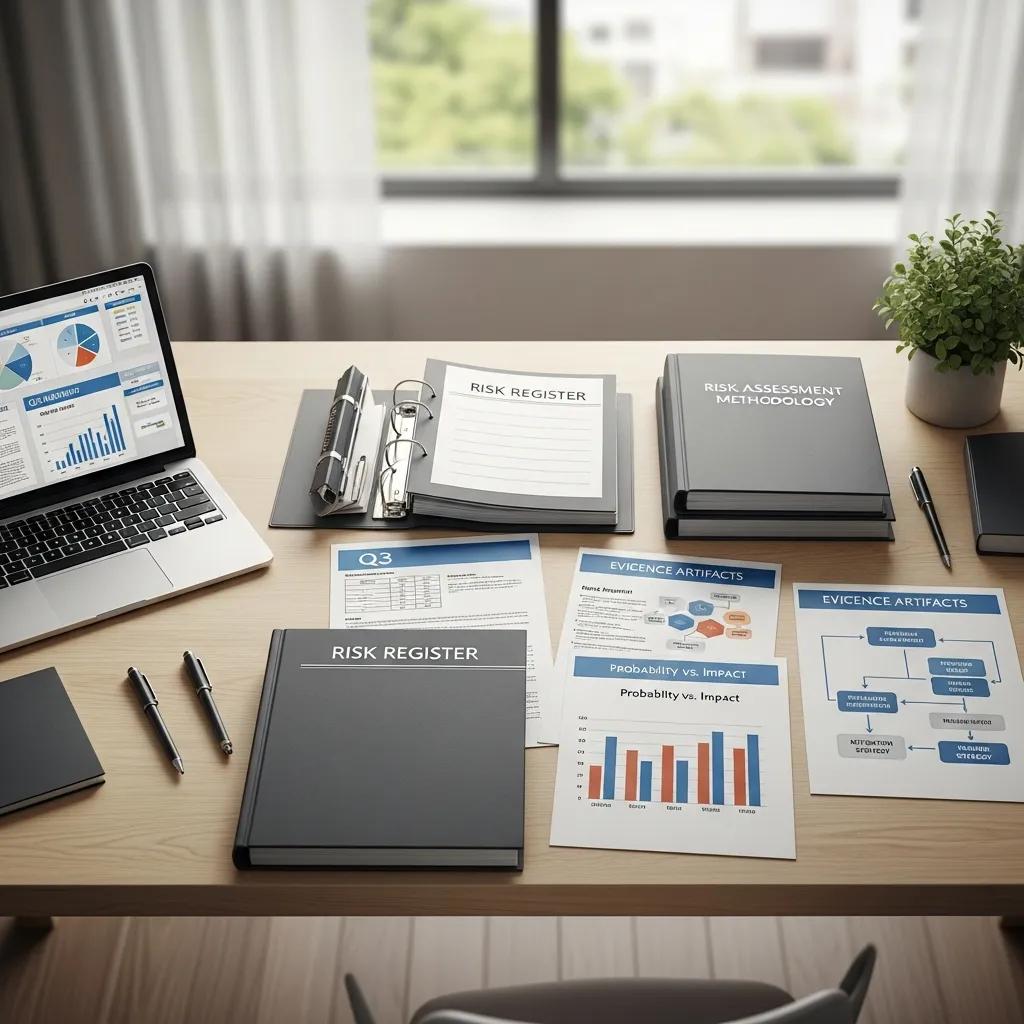
A compliant assessment needs a written methodology, risk criteria, a populated risk register, risk treatment plans, and records of analysis and approvals that show decision‑making. The methodology should describe inputs, scoring logic, treatment selection rules and review cadences so auditors can verify repeatability. Typical evidence artifacts include inventories, scan and test reports, threat‑intelligence snapshots, scoring worksheets, meeting minutes documenting acceptance, and SoA updates linking controls to residual risks. Maintaining clear links between risks, controls, owners and artifacts is essential to demonstrating conformance.
Well‑organized documentation not only satisfies auditors but also makes the output actionable for teams implementing and monitoring treatments.
How to establish an effective information security risk assessment methodology?
An effective methodology defines scope, risk criteria, data sources, roles, scoring rules and expected outputs so assessments produce consistent, auditable results aligned with business objectives. The method maps assets to threat/vulnerability pairings, applies scoring that reflects business impact and likelihood, and yields prioritized risks that feed a treatment plan and the Statement of Applicability. Choose asset‑based, scenario‑based, qualitative or quantitative approaches depending on your data, resources and the balance between precision and speed. A repeatable method supports periodic re‑evaluation, integrates automation where useful, and creates evidence bundles auditors can review.
Practical steps to build a methodology your team can use now:
- Set the context, scope and risk acceptance criteria tied to business goals.
- Pick an assessment technique and record scoring scales and calculation rules.
- Identify required inputs and evidence sources (inventories, scans, logs, intelligence).
- Assign roles, establish review cadence, and define output artifacts (register, SoA).
- Pilot the approach on a representative scope and refine scoring and thresholds.
Piloting confirms the method yields consistent outputs; next we compare asset‑based and scenario‑based approaches to help you choose.
Use the table below to compare methods and identify the best fit for your maturity and evidence availability.
| Method | Process Steps | Best-for Use Cases |
|---|---|---|
| Asset-based risk assessment | Inventory assets → classify value → map threats/vulnerabilities → score likelihood/impact → prioritize risks | Environments with mature asset inventories and clear asset value metrics |
| Scenario-based risk assessment | Define threat scenarios → map sequence and controls → estimate impact and likelihood → model residual risk | Complex attack paths, supply‑chain risks, and business process analysis |
| Qualitative analysis | Use descriptive scales and stakeholder judgment → rank risks → document rationale | Fast assessments, limited numeric data, executive decision needs |
| Quantitative analysis | Apply numeric probabilities and loss metrics → compute expected loss → prioritize by financial impact | High‑data environments with measurable loss metrics and actuarial inputs |
This comparison helps you match a method to your team’s maturity; the next section explains the two primary techniques in more detail.
What are asset‑based and scenario‑based risk assessment techniques?
Asset‑based assessments catalogue assets, assign value or criticality, and link threats and vulnerabilities to those assets to produce risk scores — a practical option when inventories are reliable. Scenario‑based assessments model realistic attack or failure sequences, evaluate control effectiveness and estimate aggregate impact — useful for complex processes or supply‑chain exposures. Asset‑based outputs tend to be prioritized asset lists and control mappings; scenario‑based outputs include attack trees, process impact narratives and consolidated risk estimates. Many teams adopt a hybrid approach: inventory rigor plus scenario testing for higher‑fidelity prioritization.
Knowing these trade‑offs helps you pick the right mix of techniques for your risk appetite and evidence base.
How to identify information assets, threats and vulnerabilities?
Start with a structured inventory that captures hardware, software, data flows, third‑party dependencies and key business processes, then classify confidentiality, integrity and availability requirements. Identify threats using logs, threat‑intelligence feeds, industry reports and stakeholder workshops to surface likely adversaries and environmental risks. Find vulnerabilities through authenticated scans, penetration tests, patch status reports and CVE mapping, and link weaknesses back to assets and scenarios. Store the result in a single source‑of‑truth inventory that feeds your risk register and supports automated update hooks.
With a populated inventory and mapped weaknesses, apply your scoring logic to prioritize remediation by likelihood and business impact.
How does AI improve ISO 27001:2022 risk assessment accuracy and efficiency?
AI speeds and sharpens assessments by automating data collection, enriching signals with context, spotting patterns and anomalies, and applying consistent prioritization that reduces assessor variance. Techniques such as NLP parse reports and logs, machine learning correlates events across sources, and statistical models normalize likelihood and impact estimates — improving repeatability and auditability. AI augments analyst productivity and surfaces correlations humans might miss, but governance and human review remain essential for defensibility. When applied with controls, AI becomes a practical multiplier across identification, analysis, evaluation and register upkeep.
Used appropriately, AI and automation can cut the manual burden of ISO 27001 assessments while preserving traceable evidence and reproducible outputs.
ISO 27001 Risk Assessments & AI‑Driven Security Scoring
This paper discusses how ISO 27001’s documentation demands can be eased with automation. In trials, SAST/DAST tooling cut manual security checks significantly and AI‑driven scoring improved prioritization consistency.
The Influence of ISO 27001 Standards on Agile Methodology—Trade‑offs and
Implications, V Naserinia, 2025
Key AI capabilities that deliver concrete gains during assessments include:
- Automated ingestion and normalization of inventories, vulnerability data and threat feeds to cut manual reconciliation time.
- Pattern recognition and anomaly detection that surface emerging threats and hidden attack chains.
- Consistent scoring and prioritization algorithms that improve repeatability and reduce assessor variance.
Below is a mapping of AI capability to practical benefits and required data inputs so you can evaluate adoption needs.
| AI Capability | Benefit | Data Source / Requirement |
|---|---|---|
| Automated data ingestion | Reduces manual reconciliation time | Asset inventories, scan outputs, logs |
| Pattern detection / anomaly recognition | Identifies novel attack indicators | Historical telemetry, threat intelligence |
| NLP for evidence extraction | Produces structured findings from unstructured reports | Audit logs, tickets, incident reports |
| Automated prioritization | Consistent ranking of risks | Scoring rules, impact matrices, business context |
| Evidence bundling and reporting | Faster audit preparation with reproducible artifacts | Change logs, analysis outputs, versioned reports |
This mapping clarifies where AI adds the most value and what operational inputs are required; next we outline how AI enhances risk identification during audits.
What are the benefits of AI‑driven auditing in risk identification?
AI‑driven auditing increases coverage and speed by continuously correlating multiple data sources to find threats and vulnerabilities that manual reviews might miss, shortening time‑to‑discovery. It supports frequent, scalable assessments while maintaining a historical trail of findings and analyst decisions that auditors can review. For example, AI can quickly map a newly disclosed CVE to an internal inventory and rank exploitability to prioritize remediation. Important caveats include model validation, explainability and safeguards against bias or data poisoning to keep outputs defensible.
Those caveats reinforce the need for governance: human review and approval remain required controls in risk treatment decisions.
How does Stratlane’s AI technology streamline risk analysis and evaluation?
Stratlane Certification is an accredited certification body offering ISO services, including ISO 27001:2022 audits. We combine experienced auditors across sectors with AI‑enabled tooling that ingests inventories, vulnerability scans and threat feeds, applies standardized scoring and generates prioritized findings and evidence bundles that map into the risk register and SoA. The approach speeds readiness validation and clarifies audit trails while keeping auditors in control to review AI‑derived evidence during conformity assessments.
This description shows how AI can support the assessment lifecycle without replacing human oversight; below we return to practical risk‑register practices and templates that incorporate AI outputs.
What are best practices for building and managing an ISMS risk register?
A best‑practice register uses a consistent taxonomy for assets, threats, vulnerabilities, likelihood, impact, owner, status, treatments and evidence links so you can trace each risk from discovery through remediation and verification. Enforce standardized fields, controlled vocabularies and unique IDs so auditors can follow a risk’s lifecycle. Make ownership and review cadence explicit and add automation hooks (scanner integrations, change‑management triggers) to keep entries current. Link register items to Annex A controls and the SoA to show how risks map to selected controls and why any residual risk is accepted.
The table below shows common register fields with example values to help design your schema.
| Register Field | Attribute | Example Value |
|---|---|---|
| Asset | Type/Identifier | “Payroll DB / DB-PAY-01” |
| Threat | Source/Vector | “Phishing leading to credential theft” |
| Vulnerability | Description | “Unpatched web framework (CVE-XXXX-YYYY)” |
| Likelihood | Scoring | “Likely (4/5)” |
| Impact | Business effect | “High — payroll data exposure” |
| Owner | Responsible party | “IT Security Lead” |
| Treatment | Action | “Apply patch; enable MFA for admin accounts” |
| Evidence | Artifact links | “Scan report v2025-11; change ticket #4567” |
This example shows how structured fields support traceability and audit evidence; the following subsection explains processes and automation to keep entries current.
How to document and continuously update identified risks?
Keep the register alive with governance that defines triggers, owners and automation points so it’s a living artifact rather than a static snapshot. Triggers include new vulnerability disclosures, incidents, configuration changes or vendor updates. When triggered, automation should create or flag entries, attach evidence and notify owners for assessment. A practical review cadence is monthly for high risks, quarterly for medium and semi‑annually for low. Approval workflows must record acceptance decisions and residual‑risk rationale. Documenting and proving these processes creates the evidence auditors expect for Clause 8.2 conformity.
Automation and clear governance reduce stale entries and improve your ability to show continuous risk management during audits.
What role does the risk register play in ISO 27001 compliance?
The risk register is primary evidence that your organization identified, analyzed, evaluated and treated information security risks per Clause 8.2. It should link to the Statement of Applicability and show timelines for treatment implementation and monitoring. Auditors review register completeness, decision records, owner assignments and evidence of treatment execution to assess conformity and control sufficiency. High‑quality registers enable traceability from a risk to the Annex A control(s), the SoA entry and subsequent monitoring outputs that demonstrate effectiveness. Weak registers — missing owners, stale evidence or poor control linkage — commonly lead to findings.
Maintaining register quality and traceability is both an operational necessity and a compliance imperative.
How to develop and implement an ISO 27001 risk treatment plan?
A risk treatment plan records whether you’ll mitigate, avoid, transfer or accept each prioritized risk, maps chosen controls to Annex A, assigns owners and defines monitoring and verification steps. Use assessment outputs to pick control families, document implementation timelines and update the SoA with justification for any acceptance. Monitoring should include KPIs, verification activities and review cadences to confirm residual risk stays within tolerance. Management approval and retained records are essential evidence that treatment decisions were deliberate and accountable.
After treatments are selected, schedule implementation and measurement activities and ensure evidence flows back into the register for audit trails.
What strategies exist for mitigation, avoidance, transfer and acceptance?
Mitigation reduces likelihood or impact via controls such as patching, access controls or encryption and is chosen when proportionate and cost‑effective. Avoidance removes exposure by changing processes or discontinuing a service. Transfer shifts financial or operational exposure via insurance or contracts with suppliers. Acceptance documents management’s informed decision to retain a risk, backed by residual‑risk calculations and contingency planning. Each choice needs selection criteria, approval records and monitoring steps to confirm it remains valid over time.
Pick the appropriate strategy based on cost, feasibility, residual risk and alignment with business objectives — and document the decision so it’s auditable.
How are Annex A controls integrated into risk treatment?
Map each identified risk to relevant Annex A controls, record the rationale in the SoA and describe how control implementation will measurably reduce likelihood or impact. Cross‑reference register items to control identifiers, note implementation status and capture evidence (policy updates, configuration baselines, test results) so auditors can verify effectiveness. Common technical control families include access control, cryptography and vulnerability management; organizational controls cover governance and supplier relationships. Updating the SoA and the register together preserves traceability and shows that treatments directly address assessed risks.
A consistent mapping approach improves audit readiness by making the link from risk to control and to evidence explicit and easy to review.
Integrating Annex A controls is central to the treatment process and ensures identified risks are addressed by appropriate measures under ISO 27001.
ISO 27001 Clause 8.2.3: Risk Assessment & Treatment
This guidance outlines how risks identified by the assessment and treatment process should be linked to Annex A controls and monitored. It highlights monitoring activities and security control requirements relevant to Clause 8.2.3 and related Annex A clauses.
Implementing information security based on ISO 27001/ISO 27002, 2020
How to prepare for an ISO 27001:2022 audit focused on risk assessment?
To be audit‑ready for Clause 8.2 you should be able to produce the methodology document, a current and traceable risk register, risk treatment records with implementation evidence, and approvals showing management review. The practical readiness step is a pre‑audit self‑assessment that validates scoring logic, checks evidence links, confirms ownership and review cadences, and samples treatment effectiveness. Tools and AI can assemble evidence bundles, generate reproducible scoring outputs and produce change logs auditors appreciate — but teams must validate AI outputs and keep human approvals in the chain. Preparing these artifacts ahead of the external audit limits scope creep and improves the chances of a smooth conformity assessment.
Use this short checklist of primary artifacts auditors typically inspect.
- Methodology Document: Documented assessment process, scoring rules, scope and roles.
- Current Risk Register: Structured entries with owners, evidence links and treatment statuses.
- Risk Treatment Records: Implementation evidence and monitoring results for selected controls.
- SoA and Control Mapping: Explicit mapping from risks to Annex A controls and residual‑risk rationale.
This checklist helps prioritize pre‑audit work; next we highlight common pitfalls to avoid when preparing Clause 8.2 evidence.
What common audit pitfalls relate to Clause 8.2 risk assessment?
Frequent pitfalls include undocumented assessment criteria, weak traceability between register items and controls, inconsistent scoring that prevents repeatability, and missing evidence of treatment implementation or owner approval. Other common issues are stale inventories, unclear ownership and evidence scattered across unversioned systems, which complicate auditor verification. Remediations include documenting scoring logic, consolidating evidence references, enforcing review workflows and validating automated inputs before they update the register. Addressing these areas proactively reduces findings and supports a defensible ISMS.
Avoiding these mistakes focuses effort on governance, evidence management and clear decision records — exactly what auditors prioritize.
How can AI tools help with audit readiness and compliance?
AI tools can produce audit‑ready artifacts such as normalized inventories, prioritized findings, change logs and evidence bundles that compile scan outputs, analyst notes and treatment records into reproducible reports auditors can review. Configure AI pipelines to tag sources, attach timestamps and include rationale fields that explain scoring decisions for transparency. Validation remains essential: sample AI outputs, reconcile them with source data and keep human approvals to ensure defensibility. Properly governed AI speeds readiness by automating repetitive tasks while preserving the documentation auditors need for Clause 8.2 verification.
When AI outputs are governed, validated and reviewed, they become a high‑value asset for accelerating audits without sacrificing transparency or accountability.
Stratlane Certification is an accredited certification body providing ISO certification services, including ISO 27001:2022. We operate in over 27 countries, pair experienced auditors with AI‑enabled tooling, and manage a streamlined workflow from quote to audit to certificate issuance. Organizations preparing for Clause 8.2 assessments can use our external readiness reviews to improve evidence packaging and reduce administrative friction prior to formal conformity assessment.
The paragraph above keeps the focus technical while offering a practical option to engage third‑party certification services for a readiness check.
If your team is ready to act, use automated tools to assemble evidence bundles, validate scoring rules on samples and run mock audits to confirm register entries and SoA mappings meet auditor expectations. These steps will shorten the external audit timeline and improve the quality of findings presented during assessment.
Stratlane Certification provides ISO certification services, including ISO 27001:2022. Our process combines AI‑enabled evidence collection with experienced auditor oversight. Organizations can request a quote to schedule an audit and pursue certification through a managed quote → audit → certificate workflow designed to reduce administrative friction.
This brief call‑to‑action places next steps after the technical content while keeping the article’s primary focus on assessment best practice.
Frequently Asked Questions
What is the importance of a risk treatment plan in ISO 27001 compliance?
A risk treatment plan documents how the organization will address identified risks by specifying chosen strategies — mitigate, avoid, transfer or accept — and mapping those choices to Annex A controls. It creates accountability for decisions and sets out monitoring and verification steps so you can demonstrate effectiveness. Auditors rely on treatment plans to confirm risks are being managed deliberately and consistently.
How can organizations ensure continuous improvement in their risk assessment process?
Continuous improvement comes from regularly reviewing and updating the risk register, treatment plans and methodology. Build feedback loops that capture lessons from audits, incidents and changes in the threat landscape. Use validated AI to surface patterns, run periodic pilots to refine scoring, and keep staff trained so processes evolve with new risks. Regular reviews and evidence of corrective actions close the loop for auditors.
What role does employee training play in ISO 27001 risk assessments?
Training ensures staff understand their roles in identifying and managing information security risks. Programs should cover the assessment process, how to spot threats and vulnerabilities, and the importance of accurate evidence capture. Well‑trained teams improve detection, reduce errors in inventories and support a proactive risk culture that strengthens overall ISMS performance.
How often should organizations conduct risk assessments under ISO 27001?
Conduct risk assessments regularly — typically at least annually — and whenever significant changes occur, such as new technology, major process changes, regulatory updates or after incidents. You should also reassess when new threats are identified. Regular cadence plus event‑driven assessments keeps the risk picture current and aligned with Clause 8.2 expectations.
What are the challenges organizations face when implementing ISO 27001 risk assessments?
Common challenges include limited understanding of standard requirements, resource constraints, resistance to change, and keeping inventories and evidence current. Integrating assessment activities into existing workflows and ensuring stakeholder engagement are also frequent hurdles. Address these issues with clear leadership, documented processes, automation where sensible and ongoing training.
How can technology improve the efficiency of ISO 27001 risk assessments?
Technology automates data collection, normalizes inputs, speeds analysis and streamlines reporting. AI‑driven analytics can highlight patterns and anomalies across large datasets, improving prioritization accuracy. Risk management platforms centralize registers and evidence, making audits faster and more reliable. By reducing manual work, technology frees teams to focus on strategic remediation and governance.
Conclusion
ISO 27001:2022 risk assessments give organizations a structured, auditable way to identify and manage information risks, improving compliance and operational resilience. Applying clear methodologies and leveraging validated AI tools can increase accuracy and reduce manual effort, while keeping human oversight ensures defensible decisions. Engaging expert certification services can help streamline readiness and packaging of evidence for auditors. When you’re ready, explore our ISO certification services to move from assessment to certified ISMS with confidence.