Prepare for Your ISO Audit: Top Tips and Checklist
ISO Audit Prep: Practical Guide to Confident Certification
An ISO audit checks whether your management system meets a standard’s requirements and whether controls are delivering the results they should. Preparing thoroughly cuts audit time, lowers the chance of non‑conformities, and speeds up certification. This guide gives clear, practical steps and ready-to-use checklists: a structured readiness framework, document-control best practices, internal-audit guidance, team training plans, and practical ways AI can speed the work. Many organizations trip over scattered records, unclear clause-to-process links, and loose corrective-action closure—issues we address with concrete remediation tasks and measurable success criteria. You’ll find a prioritized sequence (gap analysis → remediation → internal audits → management review → external readiness), mappings for ISO 9001/14001/27001/42001, document and evidence templates, internal-audit techniques, training outlines, and targeted AI use cases. The sections that follow are written to be used directly during mock audits and pre‑certification rehearsals.
What Are the Key Steps in ISO Audit Preparation?
Preparing for an ISO audit is a repeatable sequence that aligns your management system to the standard, closes gaps, and produces objective evidence for auditors. The approach is simple: set scope, run a gap analysis, fix findings, verify through internal audits and management review, then confirm readiness for the external audit. The payoff is predictable certification outcomes, fewer findings, and shorter audit time. Below is a compact workflow you can apply right away to scope an ISO project and assign responsibilities.
Follow these prioritized steps when preparing for certification:
- Define scope, objectives, and process maps so audit boundaries and responsibilities are clear.
- Perform a gap analysis against your chosen ISO standard to identify missing controls and documentation.
- Close gaps by implementing corrective actions and updating procedures, records, and metrics.
- Run internal audits, hold management review, and verify corrective-action effectiveness before scheduling the external audit.
These four stages form the readiness backbone; next we explain how to run an objective readiness assessment that shows progress and signals when to book the external assessment.
How to Conduct an Effective ISO Readiness Assessment
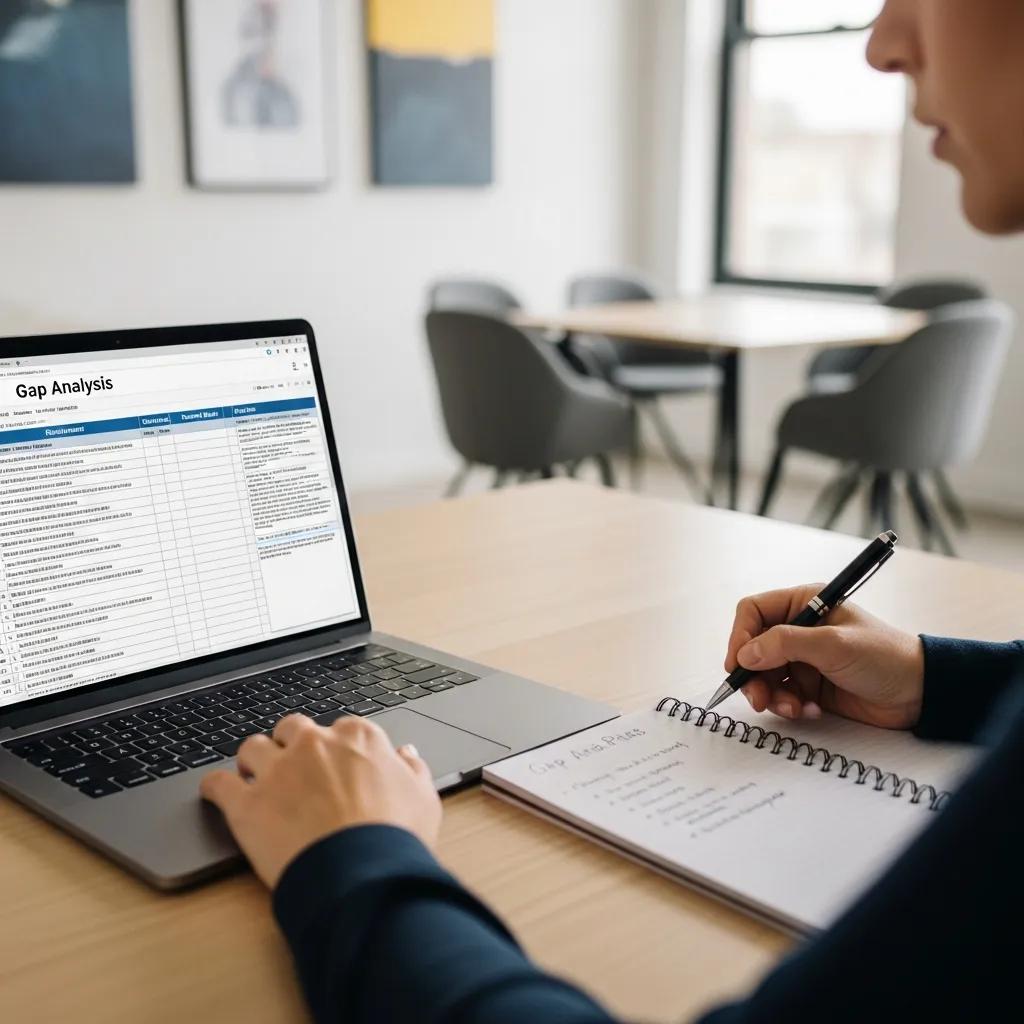
A readiness assessment evaluates conformity against the standard’s clauses and produces a prioritized remediation plan with clear acceptance criteria. Run by a competent lead (internal or external), a good assessment uses a scored gap template and blends document review, process walkthroughs, and sample evidence checks. Track metrics such as percent of closed gaps, open minor/major findings, and verified corrective actions—hitting >90% closure on critical gaps with verifiable evidence is a practical readiness signal. Tools range from spreadsheets to AI-assisted platforms that collate evidence and reveal patterns, but the method stays the same: measure, remediate, verify. The final report should list prioritized actions, owners, deadlines, and objective acceptance criteria to drive internal audits and management review.
What Does a Complete ISO Certification Audit Checklist Include?
A certification checklist lists the documents, records, process evidence, and interview topics auditors expect, and it pairs each item with acceptance criteria. Use five categories—Management, Processes, Records, Evidence, Personnel—to make sure you cover policies, procedures, objective evidence, sampled records, and individual competence. During mock audits, apply concrete acceptance rules (for example: “versioning present, reviewed in last 12 months, approvals logged”) so auditors get consistent answers. Below is a practical checklist you can adapt for rehearsals.
The core checklist covers five categories:
- Management: policy, objectives, and management-review records showing leadership involvement.
- Process: process maps, inputs/outputs, KPIs, and proof of monitoring and control.
- Records: versioned procedures, training logs, calibration and maintenance records, and CAPA files.
- Evidence: sampled outputs, process metrics, test results, and records traceable to clauses.
- Personnel: role descriptions, competence evidence, and interview-prepared process owners.
Use this checklist in mock audits to confirm each item has verifiable evidence and a named owner ready to demonstrate conformity on audit day.
| Preparation Step | Expected Deliverable | Practical Check Items |
|---|---|---|
| Scope Definition | Scope statement, process map | Confirm boundaries, included/excluded sites, process owners |
| Gap Analysis | Gap matrix with scores | List nonconformities, severity, evidence required |
| Remediation | Updated procedures, CAPA records | Assign owners, set deadlines, retain closure evidence |
| Internal Audit | Audit reports, NCR logs | Sampling evidence, interviews, follow-up verification |
| Management Review | Minutes, decisions, resource allocation | Action items with due dates and metrics |
How to Understand and Comply with Your Specific ISO Standard
Making a standard actionable means mapping its clauses to your operational processes and focusing on audit-relevant controls that affect risk and outcomes. The core activity is clause-to-process mapping: identify which processes satisfy each clause, gather objective evidence, and assign KPIs that show controls work. The outcome is a traceable system where each clause links to controls, records, and owners—reducing auditor uncertainty and demonstrating continual compliance. Below we summarize core requirements and show how to align processes so evidence is available during the audit.
What Are the Core Requirements of ISO 9001, ISO 14001, ISO 27001, and ISO 42001?
Each standard targets different risks and controls: ISO 9001 focuses on quality and customer outcomes; ISO 14001 addresses environmental aspects and legal obligations; ISO 27001 centers on information security and risk treatment; ISO 42001 targets AI governance and responsible AI management. Typical auditor requests include policy documents, risk registers, control-test records, incident logs, and evidence of leadership oversight. Mapping these requirements to your processes clarifies who provides which evidence and reduces category gaps during interviews.
How to Align Your Management System with ISO Standard Clauses
Alignment is a deliberate exercise: list clauses, link each to a process owner, define required records, and set KPIs to measure effectiveness. Build a clause-to-process matrix, embed controls in procedures, and surface key metrics in dashboards for management review. Example: map the “competence” clause to HR processes, training records, and assessments, then track a KPI for training completion and demonstrated competence. Keep mappings current when processes change and preserve version history so auditors can trace decisions. This turns abstract clauses into verifiable, operational practices auditors can check quickly.
| Clause Area | Mapped Process | Evidence / KPI |
|---|---|---|
| Leadership & Commitment | Management review process | Minutes, action closure rate |
| Operational Control | Core process procedures | Process KPIs, sampling records |
| Risk Management | Risk assessment workflow | Risk register, mitigation status |
| Competence | HR training & evaluations | Training completion, competence tests |
How to Manage Documentation and Control Records for ISO Audits
Good document control centralizes authoritative files, enforces versioning and approvals, and gives auditors fast access to required evidence—reducing search time and preventing disputes. The core process is a controlled document lifecycle: create, review, approve, distribute, archive—backed by access controls and audit trails that show who changed what and when. The result is auditable traceability for every documented control, faster evidence retrieval during on-site or remote audits, and fewer findings tied to missing or outdated records.
Clear, auditable documentation and record control are foundational to achieving and maintaining certification.
Documenting Controls for Audit Compliance
Clear control documentation makes compliance verifiable. Organizations that lack structured records or the skills to document controls often struggle to demonstrate conformity.
Internal control audit and compliance: documentation and testing under the new COSO framework, 2015
Best practices include a document master list, enforced electronic version control, retention schedules, and linking training records to relevant procedures. The next section lists essential documents auditors typically request and examples of acceptable evidence and storage locations.
What Documents Are Essential for ISO Audit Compliance?
Auditors expect a short set of mandatory documents plus commonly requested records that prove your system is implemented and effective. Mandatory items usually include policy statements, scope, documented procedures for key processes, and records of monitoring and measurement. Frequently requested records include training logs, calibration files, supplier evaluations, and CAPA evidence. Acceptable formats range from signed PDFs and versioned Word files to exportable audit logs and protected database extracts—so long as they show authenticity, review dates, and approvals. Storing these in a searchable repository with consistent naming and indexed fields helps auditors find evidence quickly and boosts confidence in your control environment.
Below is a scannable table summarizing core documents and where auditors commonly expect to find them.
| Document Type | Required? (Y/N) | Typical Evidence / Storage Location |
|---|---|---|
| Policy Statements | Y | Signed policy PDF in controlled repository |
| Scope & Process Maps | Y | Versioned diagrams and scope statement |
| Procedures & Work Instructions | Y | Approved procedures with revision history |
| Training Records | Y | Training log exports, competency checklists |
| Corrective Action Records | Y | CAPA system entries with closure evidence |
How to Implement Effective Document Control for ISO Audits
Implement document control with defined approval workflows, strict version rules, role-based access, and preserved audit trails that capture changes and reviewer identities. Start with a document-control procedure that sets revision intervals, approval authorities, and storage locations, then manage documents through a register and electronic controls where possible. Digital systems should use immutable logs and access restrictions; paper environments should retain stamped approvals and a registrar index. Regular internal checks and a standing document-control item in management review keep the system effective. These steps make documentary evidence robust and credible during auditor verification.
After you’ve established document control, consider services to maintain post-certification records and make certificates available to stakeholders. Stratlane Certification offers certificate management and a centralized Certificate Database/Downloads service to help teams keep verified copies of issued certificates and related documentation for ongoing compliance and stakeholder requests.
What Is the Role of Internal Audits in ISO Certification Readiness?
Internal audits act as rehearsals that verify control implementation, uncover non‑conformities early, and confirm corrective actions are effective before the external certification audit. The cycle is iterative: schedule audits by risk and criticality, perform evidence-driven testing and interviews, report graded findings, and track corrective actions through to verified closure. The result is a stronger management system that demonstrates continual improvement and lowers the chance of major external findings. Well-scoped internal audits expose systemic weaknesses and focus remediation where it matters most for certification.
An internal-audit program should include a risk‑based schedule, impartial auditors, clear sampling methods, and escalation paths for serious findings. The next section breaks down planning and execution steps you can apply immediately to make internal audits efficient and meaningful.
How to Plan and Execute an Internal ISO Audit Process
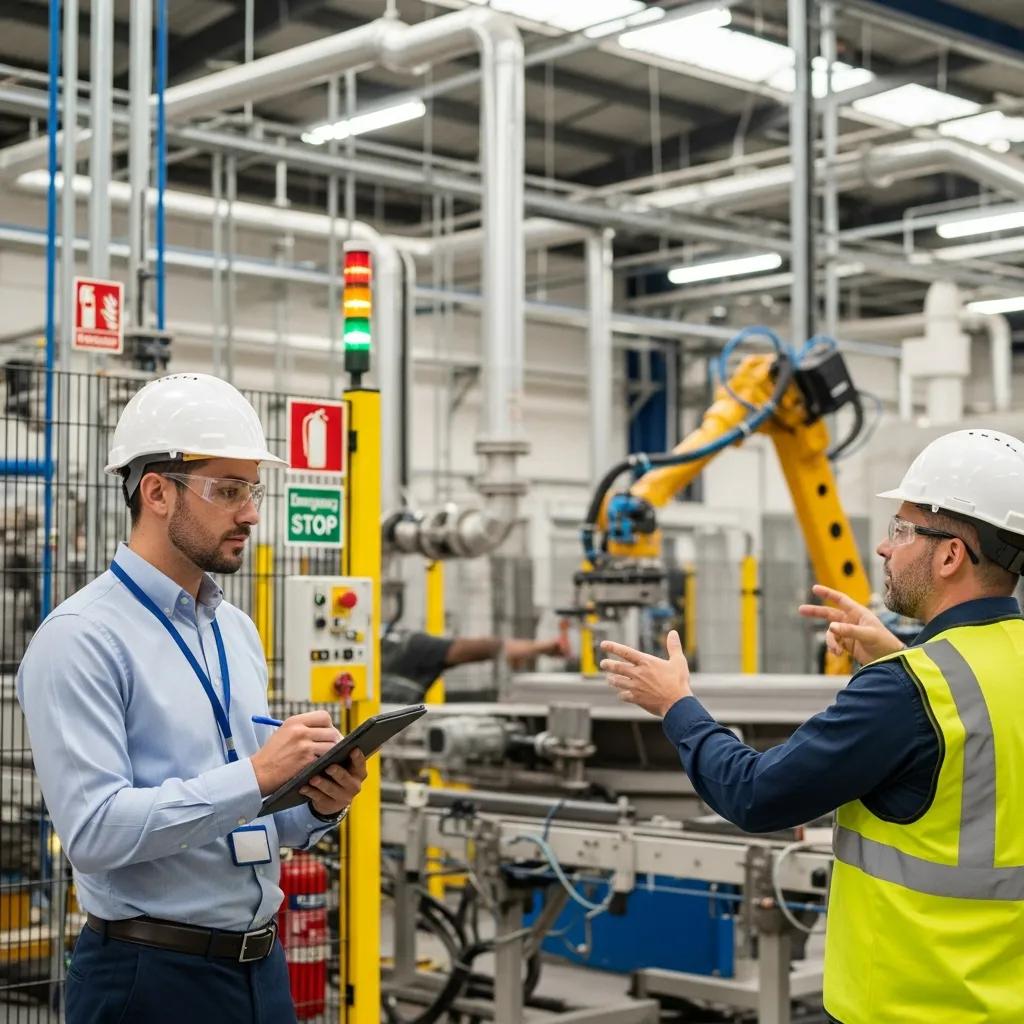
Start audit planning by defining scope from a risk perspective, selecting competent auditors, and building a sampling plan that covers outputs and supporting records. In the field, use structured interviews, observe operations, and cross-check procedures against actual practice to collect objective evidence. Reports should grade findings (minor/major), require root-cause analysis, and assign owners with deadlines for corrective actions. Follow-up must verify fixes and keep closure evidence to show sustained correction. A typical internal-audit agenda includes opening meeting, process walkthrough, interviews, evidence review, closing meeting, and a written report with action items.
Good internal audits reduce surprises at certification by proving corrective actions are implemented and effective.
When internal audits reveal gaps, many teams bring in external help to accelerate readiness. Stratlane Certification provides internal-audit support and AI-driven readiness assessments that prioritize gaps and assemble objective evidence—helping you close findings faster and move smoothly to the external audit.
How to Identify and Address Non-Conformities During Internal Audits
Identify non‑conformities with clear grading rules—separate minor observations from major non‑conformities—and use root‑cause tools like 5 Whys or fishbone diagrams to find underlying causes. Log corrective actions with owners, timelines, and measurable closure criteria; verification should include proof the action was implemented and that it fixed the issue. Triage high‑severity items with immediate containment and medium‑term corrective plans, and track recurring trends through management review for systemic fixes. Retain before/after evidence, effectiveness test results, and auditor confirmation so closures remain verifiable over time.
Corrective actions deliver real improvement only when they align closely with the ISO standard and your internal procedures.
Effective Corrective Actions for ISO Improvement
Corrections and corrective actions work when they map to the reference standard and the organization’s procedures. Aligned actions drive lasting improvement rather than temporary fixes.
Corrections and corrective actions–instruments for the continuous improvement of a management system, E CONDREA, 2020
A robust corrective-action process reduces repeat findings and shows external auditors that your organization learns from issues and continuously tightens controls.
How to Engage and Train Your Team for Successful ISO Audits
Engaging and training staff makes sure people understand the controls, can find and present evidence during interviews, and keep compliance part of everyday work. Combine role‑based training, targeted awareness campaigns, and interview rehearsals for process owners. The payoff is fewer surprises, consistent answers across staff, and stronger proof that procedures are embedded in daily routines. Tie training outcomes to KPIs and use feedback loops so content evolves with process changes.
Design training for different audiences—leadership, process owners, operators—and favor short micro‑learning modules to reinforce key controls. The next section lists required training topics and delivery approaches to get teams audit-ready quickly.
What Employee Training and Awareness Are Required for ISO Audit Preparation
Training should be role‑specific: leadership needs awareness of policy and resource commitments; process owners need procedural competence and evidence retrieval skills; operators need clear work instructions and demonstrated competence. Deliver content as short e‑learning, practical sessions, and interview prep to build confidence. Align refresher frequency to risk—critical processes get annual or semi‑annual refreshers; lower‑risk tasks follow a lighter cadence. Use readiness checks and knowledge assessments to measure effectiveness and feed gaps back into CAPA before audits.
Structured role‑based training reduces inconsistent auditor responses and helps maintain conformity across the organization.
How to Foster a Culture of Continuous Improvement and Compliance
Build continuous improvement with simple mechanisms: a frontline suggestions system, recognition for implemented ideas, regular leadership updates, and KPIs that reward both conformity and innovation. Make non‑conformance reporting straightforward and emphasize learning over blame. Track metrics like corrective‑action closure rate and quality of root‑cause analyses to measure progress. Leadership should share audit results and improvement plans in management review, and recognize teams that close meaningful gaps. Over time these practices make audit readiness routine rather than last‑minute firefighting.
These habits help sustain compliance and steadily strengthen controls between certification cycles.
How Does AI-Driven Auditing Enhance ISO Audit Preparation?
AI-driven auditing complements traditional preparation by automating gap scoring, speeding evidence collation, and surfacing patterns humans might miss. Techniques like natural‑language processing, pattern detection, and automated sampling reduce manual effort and broaden coverage. Benefits include faster readiness assessments, more consistent sampling, and earlier detection of systemic issues—leading to shorter audits and fewer findings. AI isn’t a substitute for professional judgment; it’s a force multiplier that lets audit teams focus on high‑risk remediation while automation handles repetitive evidence tasks.
Below is a concise mapping of AI capabilities to practical audit outcomes and use cases you can adopt to boost efficiency.
| AI Feature | Benefit | Practical Use Case |
|---|---|---|
| Automated gap scoring | Rapid prioritization of gaps | Score controls against clauses to prioritize remediation |
| Evidence collation | Faster assembly of documentation | Gather versioned docs, training logs, and change histories |
| Pattern detection | Early risk identification | Flag recurring issues across similar processes for root-cause focus |
What Are the Benefits of Leveraging AI Tools in ISO Audits?
AI tools deliver measurable wins: less time assembling evidence, more consistent sampling, and earlier anomaly detection that could otherwise become audit findings. Useful metrics include percentage reduction in prep hours, fewer repeat NCRs thanks to better root‑cause detection, and broader sampling across datasets. Maintain governance: keep human oversight, document AI logic, and validate AI findings with sampled manual checks. Combining AI speed with auditor judgment gives you both efficiency and defensible results.
These advantages make AI especially valuable for complex systems with large volumes of records, provided governance keeps outputs auditable.
How Stratlane’s AI-Driven Audit Tools Improve Efficiency and Accuracy
Stratlane Certification applies AI to readiness assessments, evidence collation, and audit planning to cut manual work while preserving auditor oversight. Capabilities include rapid gap scoring, automated assembly of versioned documents and training records, and risk‑pattern alerts that focus internal audits. In practice, these tools shorten the time from gap detection to corrective-action assignment and deliver organized evidence packages that streamline external assessment. If you want tailored help, Stratlane Certification can support you from a quote to audit booking and certificate issuance—request a Get a Quote or Book your audit to see how AI-augmented readiness fits your timeline and risk profile.
Teams that pair Stratlane’s AI with disciplined internal processes typically move to certification faster and present cleaner evidence trails to external auditors.
Frequently Asked Questions
What is the difference between internal and external ISO audits?
Internal audits are performed by your organization to check compliance and find improvement opportunities—essentially a rehearsal. External audits are conducted by an independent certification body that verifies conformity for certification. Both are necessary: internal audits prepare you and reduce surprises; external audits confirm whether you meet the standard.
How often should internal audits be conducted?
Frequency depends on size, complexity, and risk. At minimum, audit key processes annually; higher‑risk areas need more frequent checks. Use a risk‑based schedule so critical processes are reviewed regularly and resources target the areas that matter most.
What are common challenges faced during ISO audit preparation?
Common issues include incomplete documentation, inconsistent staff training, and weak corrective‑action closure. Other problems are scattered records and unclear responsibilities. Address these with structured documentation practices, role‑based training, and regular internal audits to identify and fix gaps early.
How can organizations ensure continuous compliance after certification?
Maintain a strong management system with regular internal audits, ongoing training, and a continuous‑improvement mindset. Set up clear monitoring, CAPA processes, and document‑update routines. Keep leadership engaged through management review and transparent communication about compliance work.
What role does management play in ISO audit preparation?
Management sets direction, provides resources, and demonstrates commitment. Leaders define scope, ensure processes align to the standard, and follow up on audit findings and corrective actions. Visible leadership engagement drives accountability and keeps the program effective.
How can technology assist in ISO audit preparation?
Technology speeds documentation, simplifies data collection, and improves team coordination. AI platforms can streamline gap analysis, evidence collation, and reporting, while document-management systems make records searchable and current. The right tools reduce manual work and make audit readiness repeatable.
Conclusion
Preparing for an ISO audit sharpens your controls and makes certification predictable. By following the structured steps here—clear scope, focused gap analysis, disciplined remediation, thorough internal audits, and leadership review—you reduce non‑conformities and shorten audit time. Use targeted training, solid document control, and selective AI to boost efficiency. Start your certification journey with a repeatable readiness program and leverage available resources and services to keep compliance sustainable. If you need help, explore Stratlane’s resources or reach out for tailored support.