How to Select Your ISO Certification Body for Success
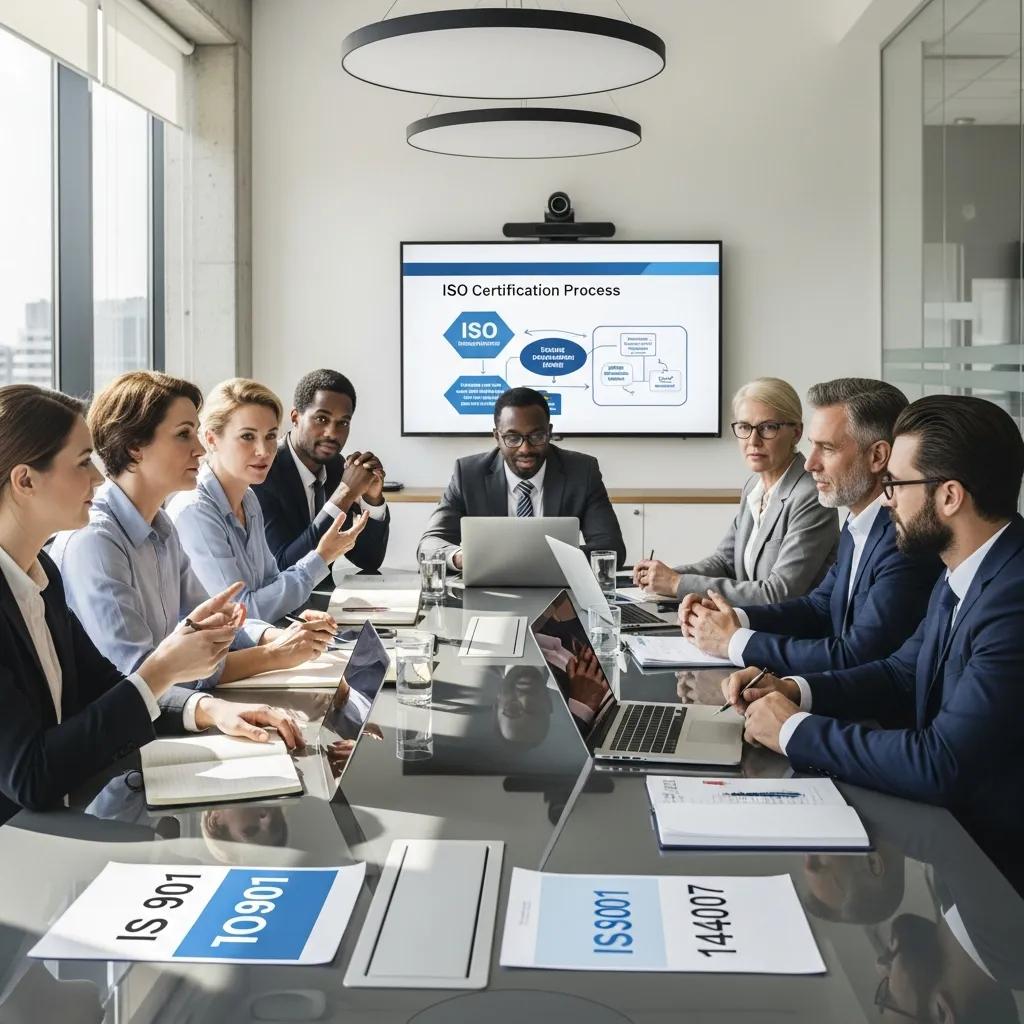
How to Choose the Right ISO Certification Body: Practical Criteria and AI-Enabled Benefits
Choosing the right ISO certification body is about more than a framed certificate — it affects regulatory acceptance, customer confidence, and how your processes improve over time. This guide explains what a certification body does, why accreditation matters, and how AI-assisted auditing is changing the landscape to deliver faster, more reliable outcomes. You’ll get an actionable checklist, a clear audit lifecycle with typical timelines, a look at how AI supports auditors, and a framework to compare registrars objectively. Practical tools — comparison tables and step-by-step timing — help procurement, quality, and security teams shortlist providers that match their technical scope and industry needs.
Why Is Choosing the Right ISO Certification Body Crucial for Your Business?
A certification body provides independent confirmation that your management system meets a specific ISO standard — and that confirmation affects market credibility, contract eligibility, and regulatory acceptance. The right registrar ensures your certificate is recognized by customers, regulators, and procurement teams, reducing the risk of rejected bids or cross-border non-acceptance. A competent registrar also improves audit quality: skilled auditors deliver actionable findings, not checkbox reports. Below we unpack the concrete impacts on credibility and compliance so you can see how certificate acceptance translates to business outcomes.
What Impact Does Certification Body Selection Have on Credibility and Compliance?
Picking a well-recognized registrar strengthens stakeholder trust by pairing your certificate with impartial, accredited oversight. In markets where procurement rules require accredited certification, the registrar’s recognition directly influences whether you qualify for tenders and supply chains. Choosing a non-accredited or poorly regarded body can lead to reputational risk and repeat audits if customers or regulators question the certificate. Knowing these risks helps teams prioritize accreditation and scope checks when selecting vendors.
How Does an Accredited Certification Body Ensure Trust and Recognition?
Accreditation is a formal assessment by an accreditor that confirms a certification body’s impartiality, competence, and adherence to accepted methods — and it supports mutual recognition between markets. Recognized accreditors and IAF signatories create a framework that makes certificates easier to accept across jurisdictions. Accreditation also enforces standards for auditor qualifications, audit methodology, and complaint handling, protecting audit integrity and reducing conflicts of interest. With accreditation clarified, the next step is applying practical selection criteria to compare providers.
What Are the Key Criteria for Selecting an Accredited ISO Certification Body?
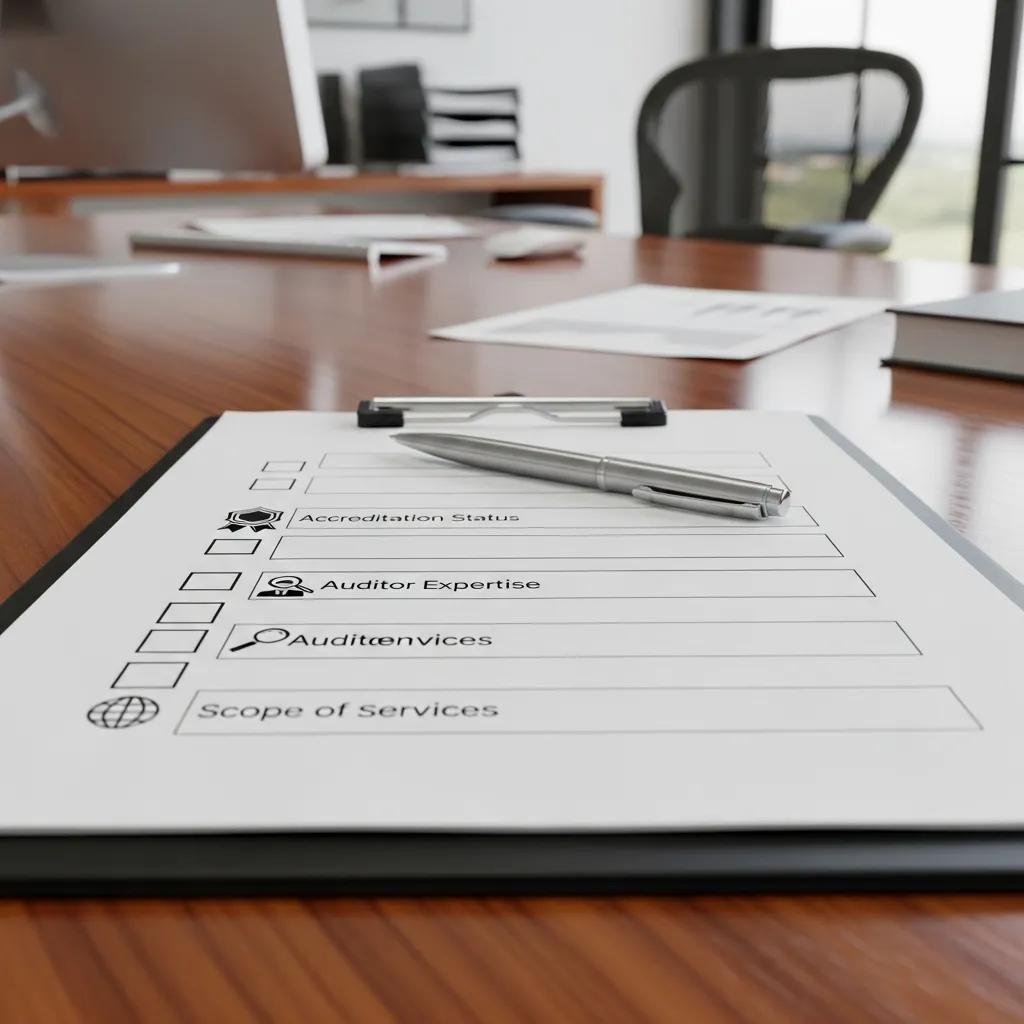
Choose a registrar using a systematic assessment that balances accreditation, auditor expertise, scope capabilities, transparent fees, and post-certification support. A consistent checklist lets you compare providers for your standard (ISO 9001, ISO 27001, ISO 14001, ISO 45001). Below is a practical checklist to use when reviewing quotes and proposals; the following sections explain how to verify accreditation and evaluate auditor experience.
Research has examined methods to rank the service quality factors that matter when selecting certification bodies.
Evaluating Certification Body Service Quality
This study outlines a methodology for weighting the factors from the ISO-10015 guidelines that affect certification body service quality. The authors applied the fuzzy analytic hierarchy process (FAHP) to identify which factors most influence perceived service performance.
Relative importance of the factors under the ISO-10015 quality management guidelines that influence the service quality of certification bodies, PL Huang, 2017
- Accreditation status and recognized accreditors: Confirm official accreditation for the specific standard.
- Industry and technical experience: Verify auditors understand your sector’s risks and controls.
- Scope and integrated audit capability: Make sure the registrar can cover multiple standards if needed.
- Cost transparency and scheduling flexibility: Request itemized fees and realistic timelines.
- Post-certification support and certificate management: Review surveillance planning and validity services.
This checklist sets up the comparison table below, which maps core attributes to the responses you should expect from reputable registrars.
Intro to comparison table: Use the table to compare certification bodies across essential attributes and score providers objectively.
| Attribute | What to Verify | Expected Provider Response |
|---|---|---|
| Accreditation | Named accreditor and certified scope (e.g., management systems) | Accredited by a recognized body with a searchable listing |
| Auditor Competence | Sector experience, formal qualifications, language skills | Auditors with sector-specific experience and demonstrable competence |
| Geographic Reach | Local auditor availability and cross-border recognition | Multi-country authorization or an established local auditor network |
| Cost Transparency | Itemized fees, travel, and reassessment costs | Clear fee breakdown and predictable surveillance charges |
| Post-Certification Support | Certificate management, surveillance scheduling | Ongoing surveillance plan and a validity-check database |
Summary: This table gives procurement teams a repeatable, evidence-based way to compare registrars and prioritize those that meet both accreditation and operational needs. Next, we cover how to verify accreditation registries and assess auditor experience when you shortlist providers.
Why Is Accreditation by Bodies Like IAF, ANAB, or UKAS Essential?
Accreditation from recognized bodies such as IAF signatories, ANAB, or UKAS provides mutual-recognition frameworks that increase the likelihood a certificate is accepted internationally. Practically, request the registrar’s accreditation certificate and confirm the scope in the accreditor’s online registry to avoid surprises during contract reviews. Accreditation also signals that the registrar follows strict rules for auditor competence, impartiality, and audit methodology — reducing the chance of low-quality certification. Knowing how to check accreditation helps you filter out providers that offer low-cost but non-recognized certificates.
How Does Industry Experience of ISO Auditors Influence Certification Quality?
Auditors with relevant industry experience spot sector-specific risks, technical controls, and regulatory nuances more quickly. Ask registrars for anonymized auditor CV summaries, references (where allowed), or examples of audits in your sector to verify competence. Experienced auditors focus on critical controls rather than generic checklists, improving the usefulness of audit reports and shortening audit time. Pairing accreditation checks with auditor expertise ensures both recognition and substantive audit quality.
How Does the ISO Audit Process Work and What Should You Expect?
The ISO audit follows a clear lifecycle: pre-audit preparation, stage 1 (documentation review), stage 2 (conformity assessment), ongoing surveillance audits, and recertification. Each stage has a defined objective — readiness assessment, implementation verification, continuous assurance, and certificate renewal. Understanding typical timelines and deliverables helps you plan management reviews, corrective actions, and audit logistics. The section below breaks the process into steps with expected timing.
A concise numbered overview of audit stages:
- Pre-audit preparation and scoping: Agree scope, timelines, and required documentation.
- Stage 1 – Documentation review: Auditor checks policies, procedures, and readiness evidence.
- Stage 2 – On-site/remote conformity assessment: Auditor verifies implementation and effectiveness.
- Surveillance audits: Periodic checks to confirm continued conformity and improvement.
- Recertification: Full reassessment at the end of the certification cycle.
Intro to timing table: The table below links each audit phase to typical timings and expected deliverables so teams can plan resources and deadlines.
| Phase | Typical Timing | Deliverable / Objective |
|---|---|---|
| Pre-audit / Scoping | 1–3 weeks | Agreed scope, audit plan, documentation list |
| Stage 1 (Documentation) | 1–2 days | Readiness report and identified gaps for Stage 2 |
| Stage 2 (Conformity) | 2–5 days (varies by scope) | Audit report, list of nonconformities, and certification decision |
| Surveillance (annual) | 1–2 days per year | Surveillance report and follow-up on corrective actions |
| Recertification | Every 3 years (typical) | Full reassessment and renewed certificate |
Summary: The lifecycle shows when to prepare documents, allocate resources, and expect audit reports so teams can minimize disruption. Next, we explain how AI-driven auditing can shorten timelines and focus auditor effort, with a practical example of how modern registrars use AI.
What Are the Steps Involved in the ISO Certification Audit Process?
The process starts with scoping and preparation, where your organization shares management system documentation and the registrar confirms scope and timing. Stage 1 identifies readiness gaps so stage 2 isn’t wasted on documentation issues. Stage 2 is the evidence-driven check — interviews, record sampling, observations, and control testing — resulting in an audit report and any nonconformities. After certification, annual surveillance audits verify ongoing effectiveness; recertification requires a full reassessment. Planning corrective actions and regular management reviews keeps your system audit-ready.
How Does AI-Driven Auditing Enhance the ISO Audit Process?
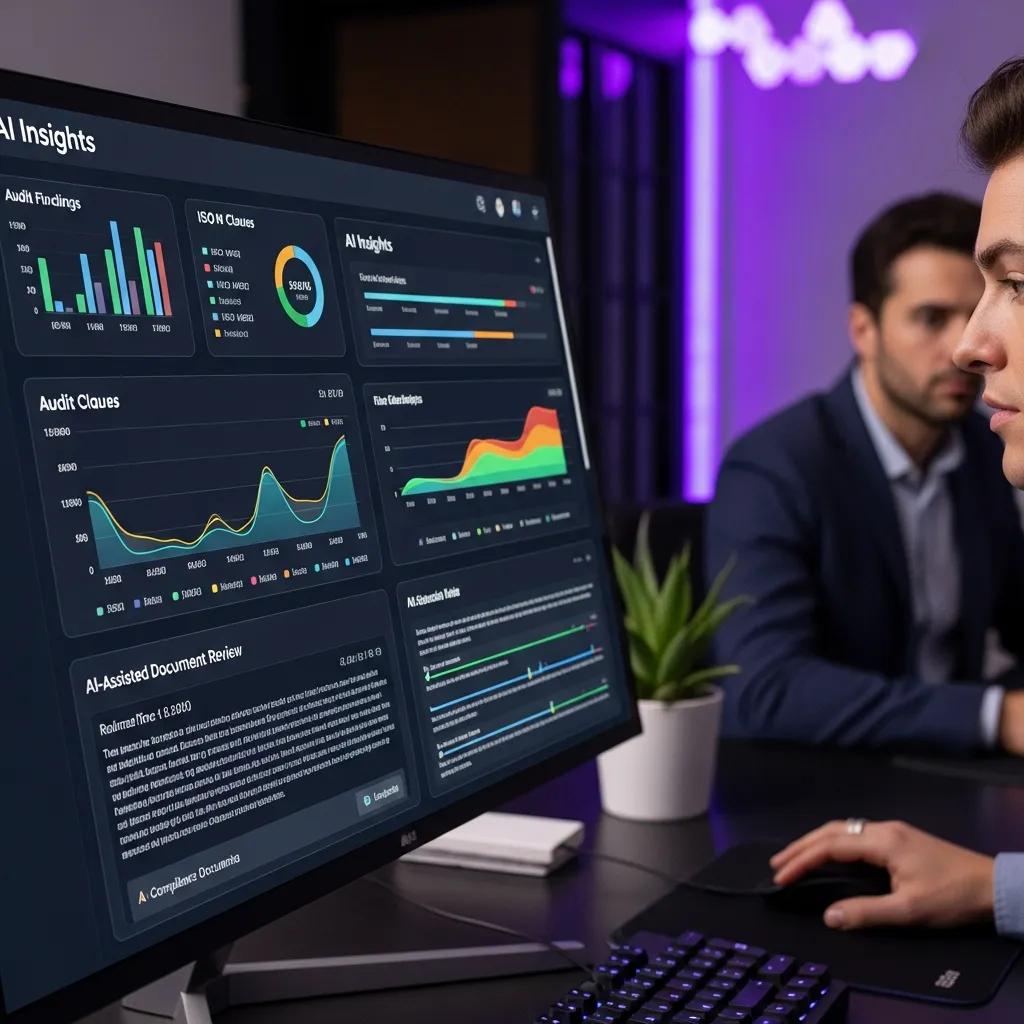
AI-driven tools automate routine document checks, detect patterns in evidence, and surface higher‑risk areas for auditors to prioritize — improving efficiency and consistency. Predictive analytics and pattern recognition flag anomalies that would otherwise need manual review, allowing auditors to spend more time on substantive testing. Crucially, AI augments auditor judgment rather than replaces it: human experts interpret AI outputs, validate findings, and shape corrective actions. This combination shortens low-value work, sharpens sampling, and reduces overall audit duration.
Research supports the role of AI in improving audit efficiency and accuracy while preserving the need for human judgment.
AI in Auditing: Efficiency, Accuracy & Auditor Role
This paper examines AI adoption in auditing, highlighting challenges, strategies, and measurable outcomes. Using qualitative case studies, it shows how machine learning, NLP, and RPA can improve audit efficiency, accuracy, and risk management. While automation increases consistency, auditors remain essential for interpretation, judgment, and stakeholder trust. Building internal capability through targeted upskilling and certification is important.
Implementing AI in auditing in organizations, K Singh, 2025
Practical example: A registrar using AI can shift time from document sifting to targeted interviews and control testing, cutting on-site days and accelerating report delivery. The next section outlines measurable benefits when you choose accredited registrars that use AI tools.
What Are the Benefits of Choosing an Accredited Certification Body with AI Capabilities?
Combining accreditation with AI tools delivers recognized assurance plus operational efficiency: shorter audits, more consistent findings, and less disruption to day-to-day work. Organizations often see reduced manual review time, quicker corrective action cycles from near-real-time insights, and consistent results across multiple sites or standards. These gains matter for integrated management systems (quality, security, environment) because AI supports consolidated sampling and evidence review. Below is a table that links AI capabilities to measurable impacts so you can estimate potential ROI when comparing registrars.
Intro to AI EAV table: The table connects specific AI features with practical benefits and likely impacts so decision-makers can quantify advantages.
| AI Capability | Benefit | Expected Impact |
|---|---|---|
| Automated document analysis | Faster evidence validation | Up to 30–50% reduction in manual review time |
| Predictive risk analysis | Targeted audit focus | Higher detection rate of material issues |
| Continuous monitoring / dashboards | Early detection of drift | Faster corrective action and fewer repeat findings |
| Integrated multi-standard sampling | Efficient combined audits | Reduced total audit days for combined scopes |
Summary: Mapping AI features to outcomes helps procurement teams estimate time and cost savings and weigh those against accreditation and auditor competence. The next sections explain how AI improves day-to-day audit efficiency and cost, and give a real-world example of an AI-enabled provider.
How Does AI-Driven Auditing Improve Audit Efficiency and Accuracy?
AI speeds up repetitive checks — document completeness, version control, and traceability — removing human error and shortening the documentation phase. Accuracy improves through consistent rule-based checks and statistically guided sampling that reveal anomalies auditors might miss. Real-time dashboards consolidate evidence and make corrective-action validation faster, reducing back-and-forth with clients. The net effect is less admin work for your team and more auditor time focused on risk-based scrutiny, which increases the practical value of audit reports.
In What Ways Does AI Reduce Certification Costs and Audit Time?
AI lowers billable audit days and logistics by enabling remote evidence collection, automated document checks, and prioritized sampling. Predictive analytics guides auditors to high-risk areas, shortening the overall audit and reducing rework from poor sampling. Organizations experience fewer operational interruptions because AI-supported audits need less staff time for interviews and evidence gathering. When calculating total certification cost, include fewer on-site days, fewer administrative cycles, and faster corrective-action closure as direct savings from AI-enabled processes.
Note: Some accredited registrars pair AI capabilities with certificate management platforms that provide validity checks and downloadable certificates, simplifying post-certification administration. The next section gives a repeatable evaluation framework to compare registrars beyond price and reputation.
How Can You Evaluate and Compare ISO Registrars Effectively?
Use a repeatable evaluation framework with weighted criteria — accreditation, auditor expertise, technology, cost transparency, and post-certification services — to score registrars against your priorities. Request standardized proposals and require clear statements of accreditation scope, anonymized auditor profiles, and sample audit plans to compare vendors fairly. For high-risk certifications (like ISO 27001), give accreditation and auditor competence more weight; for multi-site operations, emphasize scheduling flexibility and certificate management. The sections below list red flags and explain how geographic reach and support affect ongoing costs.
Key checklist for comparing registrars:
- Accreditation documents and confirmation in the accreditor’s registry.
- Clear scope for each ISO standard and capability for integrated audits.
- Auditor qualifications and relevant sector experience.
- Transparent fee schedules and travel cost policies.
- Post-certification tools such as certificate validity checks and surveillance planning.
Using this checklist standardizes vendor responses so procurement and compliance teams can make objective comparisons.
What Factors Should You Consider Beyond Price and Reputation?
Look past price and reputation to evaluate contract terms, scheduling flexibility, impartiality safeguards, and transparency of findings and nonconformity reports. Seek service-level agreements that state timelines for report delivery, corrective-action follow-up, and dispute resolution to avoid downstream delays. Verify conflict-of-interest policies and auditor independence statements to ensure impartial assessments. Prioritizing these operational and contractual elements prevents hidden costs and protects the certificate’s credibility.
How Does Geographic Reach and Post-Certification Support Influence Your Choice?
Geographic reach matters when you operate in multiple countries: local auditors reduce travel time and bring local regulatory understanding to surveillance audits. A registrar with multi-country authorization or a reliable local network can schedule surveillance faster and reduce logistical friction for multi-site recertification. Post-certification support — a certificate management database, validity checks, and downloadable certificates — streamlines procurement checks and customer due diligence. When a registrar provides these tools, your team spends less time on administrative verification and more on running the business.
Intro to certificate management table: The table below shows how certificate management features translate into operational benefits.
| Feature | Attribute | Operational Benefit |
|---|---|---|
| Central certificate database | Searchable validity checks | Faster customer verification and fewer queries |
| Downloadable certificates | Standardized formats | Simpler supply-chain documentation |
| Surveillance scheduling | Automated reminders | Better audit readiness and fewer missed audits |
Summary: Strong geographic reach combined with reliable post-certification services reduces administrative friction and supports smoother surveillance cycles, lowering long-term compliance costs. The final section gives a concise example of an accredited, AI-enabled provider to show these criteria in practice.
How Does Stratlane Certification’s AI-Driven Approach Transform ISO Certification?
Stratlane Certification is an accredited, AI-enabled certification body operating in more than 27 countries with professional auditors in 29+ countries. We certify management systems such as ISO 9001, ISO 14001, ISO 27001, and ISO 45001. By embedding AI-driven audit tools, Stratlane accelerates document review and prioritizes sampling so audits finish sooner while preserving auditor judgment and impartiality. We also offer certificate management services — a searchable validity database and downloadable certificates — to simplify post-certification administration. Below we summarize what sets our AI approach apart and how the end-to-end service flow works.
What Makes Stratlane’s AI Auditing Technology Unique in the Certification Industry?
Stratlane’s AI focuses on automated compliance checks, predictive risk-based sampling, and integrated dashboards that consolidate evidence for auditors and clients. That consolidation helps with integrated audits by correlating evidence across standards and highlighting cross-standard dependencies, reducing redundant checks. AI guides auditors to high-impact areas while auditors retain final judgment on findings and corrective actions, keeping accreditation requirements for impartiality and competence intact. The result is better focus and consistent outcomes without sacrificing oversight.
How Does Stratlane Manage the Certification Journey from Quote to Certificate?
Our typical process starts with a tailored quote and scoping exercise, followed by audit planning that defines scope, timelines, and documentation needs. During execution, AI-assisted tools streamline document review and flag priority areas for auditor assessment; auditors then carry out focused evidence verification and publish a comprehensive audit report with any nonconformities. After a successful assessment, Stratlane issues certificates and supports clients via a certificate management platform that enables validity checks and certificate downloads, with scheduled surveillance planning to maintain compliance. For organizations seeking accredited, technology-enabled certification, Stratlane’s model reduces administrative burden while delivering recognized assurance.
- Quick Quote and Scoping: Clear scope and transparent pricing to avoid surprises.
- AI-Assisted Audit Execution: Faster document validation and targeted sampling.
- Certificate Issuance and Management: Searchable validity and downloadable certificates for easy verification.
This example shows how accredited registrars can combine technology, global reach, and certificate management to deliver efficient, trusted certification outcomes.
Frequently Asked Questions
What is the difference between ISO certification and accreditation?
ISO certification is the process that shows your organization’s management system meets a specific ISO standard. Accreditation is the formal recognition that a certification body is competent to perform those certifications. In short: certification applies to the certified organization; accreditation applies to the body that issues the certificate. Knowing this distinction helps you choose a credible registrar whose certificates will be accepted where you operate.
How long does the ISO certification process typically take?
Duration depends on factors like company size, system complexity, and the ISO standard. Typically the process can take from a few months up to a year. Key phases are pre-audit preparation, documentation review, and the conformity assessment. Remember to budget for annual surveillance audits and recertification (commonly every three years).
What are the common challenges organizations face during the ISO certification process?
Common challenges include incomplete documentation, low employee engagement, and unclear understanding of the standard’s requirements. Aligning existing processes to standards can be time-consuming and may require extra resources for audits and corrective actions. To reduce delays, use a clear project plan, involve staff early, and consider guidance from experienced consultants or certification bodies.
How can organizations prepare for an ISO audit?
Prepare by running an internal audit to surface gaps, ensuring documentation is current and accessible, and training staff on their roles in the audit. Establish corrective-action plans for identified issues and consider a pre-audit or readiness review with the certification body to smooth the formal assessment.
What role does management play in the ISO certification process?
Management’s commitment is critical. Leaders set direction, allocate resources, and promote a culture of continuous improvement. Their active involvement in developing the management system, participating in reviews, and addressing nonconformities is essential to achieving and maintaining certification.
Can organizations pursue multiple ISO certifications simultaneously?
Yes. Many organizations pursue multiple certifications at once, often using an integrated management system to reduce duplication (for example, ISO 9001, ISO 14001, and ISO 45001). Integrated approaches streamline processes, but they require careful planning and sufficient resources to meet each standard’s requirements.
Conclusion
Choosing the right ISO certification body protects market credibility, supports regulatory acceptance, and improves operational efficiency. Accredited registrars that use AI tools can shorten audit timelines, increase consistency, and reduce administrative overhead. Use the checklist and evaluation framework in this guide to compare providers and pick a certification partner that aligns with your technical needs and business priorities. Ready to move forward? Start by shortlisting registrars that meet your accreditation and audit requirements.