Maintain ISO Certification: Tips for Continuous Improvement
Keeping Your ISO Certification: A Practical Guide to Ongoing Compliance and AI-Powered Auditing
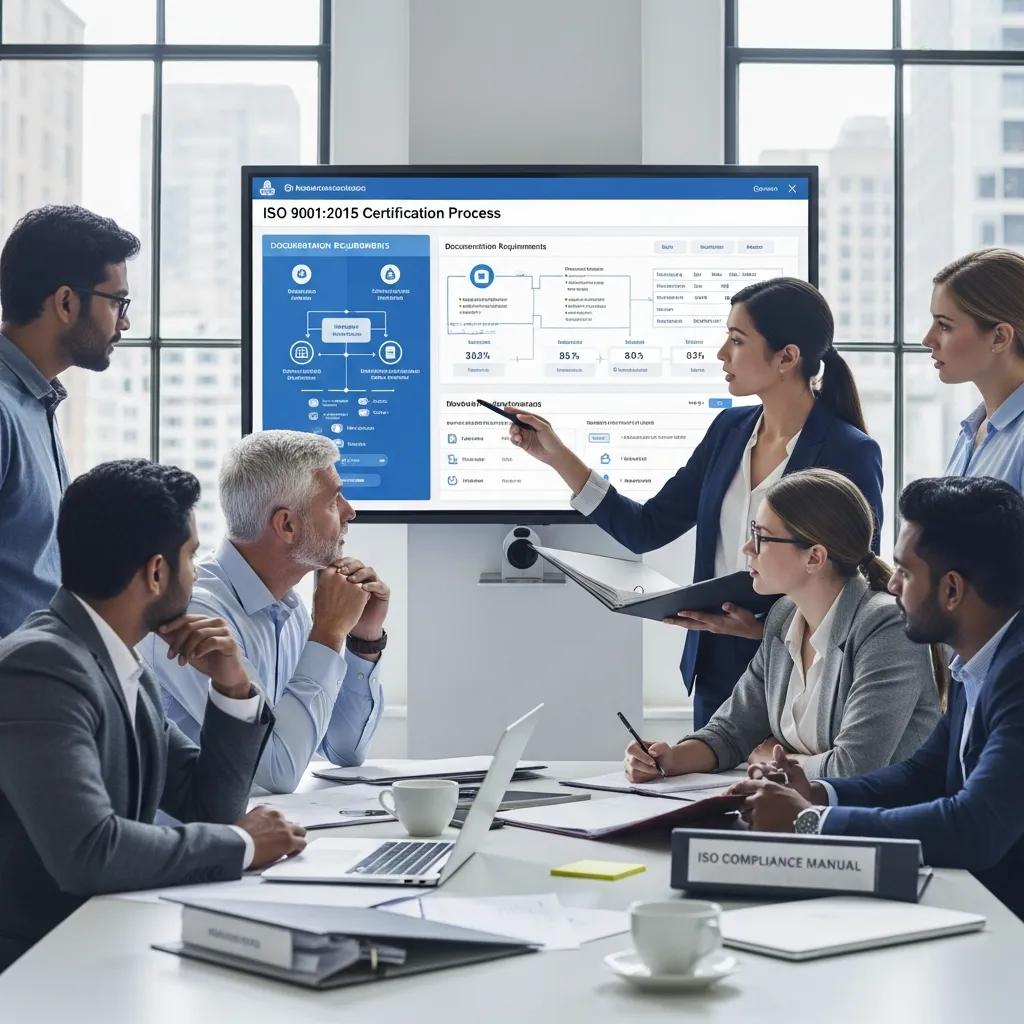
An ISO certificate is more than a plaque — it’s evidence that your systems work. Staying certified takes regular surveillance, tight document control, and a culture of continuous improvement so customers, regulators, and partners can rely on you. This guide walks you through the certification maintenance lifecycle, the everyday practices that keep systems compliant, how AI speeds readiness and auditing, and specific upkeep for standards like ISO 9001:2015 and ISO/IEC 27001:2022. We cover the common reasons organizations lose certification — documentation drift, weak CAPA, or gaps in management review — and give clear, practical steps to avoid those traps. Inside you’ll find lifecycle and maintenance checklists, comparison tables for quick reference, and ready-to-use templates for internal audits, management reviews, and recertification preparation.
What Is the ISO Certification Maintenance Lifecycle?
The maintenance lifecycle is the repeating set of activities that keep your management system aligned with the standard: initial certification, periodic surveillance audits, ongoing monitoring and improvement, and the triennial recertification. These stages confirm that requirements are met, corrective actions are effective, and performance metrics show the system works. Treat the timeline — year 0 certification, years 1–2 surveillance, year 3 recertification — as a planning tool for resources, internal audits, and evidence collection. Clear deadlines also help assign responsibility for document control, CAPA tracking, and management review inputs so readiness is consistent across the cycle.
Surveillance audits are the regular checkpoints that connect everyday operations to the certification cycle. They typically verify that past findings were addressed, process metrics meet objectives, and the system still meets the standard. Surveillance is narrower and more frequent than recertification, which is a full-system re-evaluation. To prepare for surveillance, keep records current, show internal-audit evidence, document CAPA follow-through, and keep recent management review minutes handy. The lifecycle then feeds continuous improvement activities that set you up for a successful recertification at the end of the three-year period.
How Do Surveillance Audits Ensure Continuous Compliance?
Surveillance audits keep compliance on track by sampling records and processes on a regular basis to confirm controls work and corrective actions hold. Auditors typically review internal audit reports, nonconformity logs, CAPA plans, performance metrics, and selected operational records to check ongoing conformity. Most surveillance is annual and focuses on high-risk areas or previously flagged issues; auditors look for trend data and evidence that corrective actions are closed rather than re-auditing the whole system. A frequent finding is incomplete CAPA documentation, which triggers a short corrective timeline and a focused follow-up — a clear example of how surveillance enforces discipline and continuous improvement.
Maintain a rolling evidence pack — recent audit checklists, management review minutes, and dashboards — to avoid a last-minute scramble. Organized evidence speeds auditor sampling, shortens on-site time, and reduces disruption, while making it easier to demonstrate consistent compliance.
What Are the Steps in the ISO Recertification Process?
Recertification is the planned, full audit at the end of the three-year cycle to renew your certificate and confirm the whole management system still meets the standard. Start with a readiness review that pulls together internal audit results, CAPA closure evidence, updated scope documentation, and the latest management review outputs. Assign owners and timelines early. The audit often combines remote evidence review with on-site verification, interviews, and record sampling; the auditor’s report will either recommend renewal or list nonconformities that need correction. After the audit you must close any required corrective actions within agreed timeframes and provide evidence of closure before the certification body issues or renews the certificate.
Treat recertification like a project with milestones: finish internal audits, verify CAPA closure, collate evidence, and get final management sign-off. Confirm scope, keep policies current, and ensure version control so you can close findings quickly and renew the certificate smoothly.
Which Key Practices Support Effective ISO Certification Maintenance?
Long-term certification depends on repeatable practices: scheduled internal audits, focused management reviews, reliable document control, rigorous CAPA, and routine training and monitoring. Together these create an operating rhythm that produces the evidence auditors expect and fuels continual improvement through PDCA. Assign clear owners, track timelines, and use measurable indicators to prevent drift and keep conformity through organizational change. The table below helps teams prioritize maintenance activities, set frequencies, and gather the typical evidence auditors want.
CAPA plans are central — they show how you diagnose root causes, act on them, and prevent recurrence.
CAPA Plans: Essential for ISO Audit Compliance
CAPA plans document how the auditee will address audit observations: they outline root-cause analysis, corrective and preventive actions, target completion dates, and the person accountable for each action. The CAPA plan gives an overview of intended activities and sits alongside the CAPA register that tracks individual closures.
| Activity | Frequency | Typical Evidence |
|---|---|---|
| Internal Audits | Quarterly or by process criticality | Audit reports, nonconformity logs, corrective action records |
| Management Review | At least annually | Minutes, action plans, KPI dashboards, resource decisions |
| Document Control | Ongoing | Document revision history, approval records, distribution lists |
| CAPA Management | As issues occur | CAPA register, root cause analysis, verification records |
Internal audits and management reviews are the primary sources of evidence; keeping them current lowers audit risk. Prioritize by risk and maintain a single source of truth for documents and records to improve audit efficiency and support continuous improvement.
Internal audits act as your early-warning system. A risk-based schedule targets high-risk processes more often and uses objective checklists tied to KPIs to produce actionable findings. Record findings with clear owners, due dates, and verification steps so CAPAs move to closure and create the evidence auditors expect. Building auditor competency — internal or external — and using a consistent scoring method improves audit reliability and prepares teams for surveillance.
Why Are Regular Internal Audits Crucial for ISO Compliance?
Regular internal audits spot weaknesses early, confirm corrective actions are effective, and give management objective evidence of performance. Audits should follow a risk-based plan where critical processes get more attention, and each report should connect findings to root causes and corrective steps. Keep a digital audit trail with timestamps, assigned owners, and verification notes for traceability and to reduce admin work when auditors request evidence. Consistent internal auditing also promotes organizational learning, helping teams prevent recurrence and stay prepared for external surveillance.
To be effective, internal audit programs need trained auditors, impartial audit teams, and a clear scoring rubric for findings. Remote audits can work well if document control and sampling plans are solid. Feed audit results into management review and CAPA workflows to create a continuous feedback loop that drives measurable improvement and strengthens readiness for surveillance and recertification.
How Do Management Reviews Drive Continuous Improvement?
Management reviews turn data into decisions. They evaluate performance metrics, audit results, customer feedback, and resource needs to authorize corrective and improvement actions. Typical inputs include internal audit summaries, nonconformity status, risk registers, and process KPIs; outputs should record decisions on objectives, resource allocation, and follow-up actions. Use a structured agenda and record minutes with assigned owners and deadlines to create an auditable trail and ensure accountability. Management reviews should feed directly into PDCA, turning gaps into prioritized projects and measurable objectives for the next cycle.
A practical agenda covers performance vs objectives, audit results, customer feedback trends, CAPA effectiveness, and changes that could affect the management system. Track action items in a system to ensure closure and show continual improvement during surveillance. When reviews are consistent, evidence-based, and action-oriented, they become a core lever for certification health and system maturity.
How Does AI-Driven Auditing Enhance ISO Certification Maintenance?
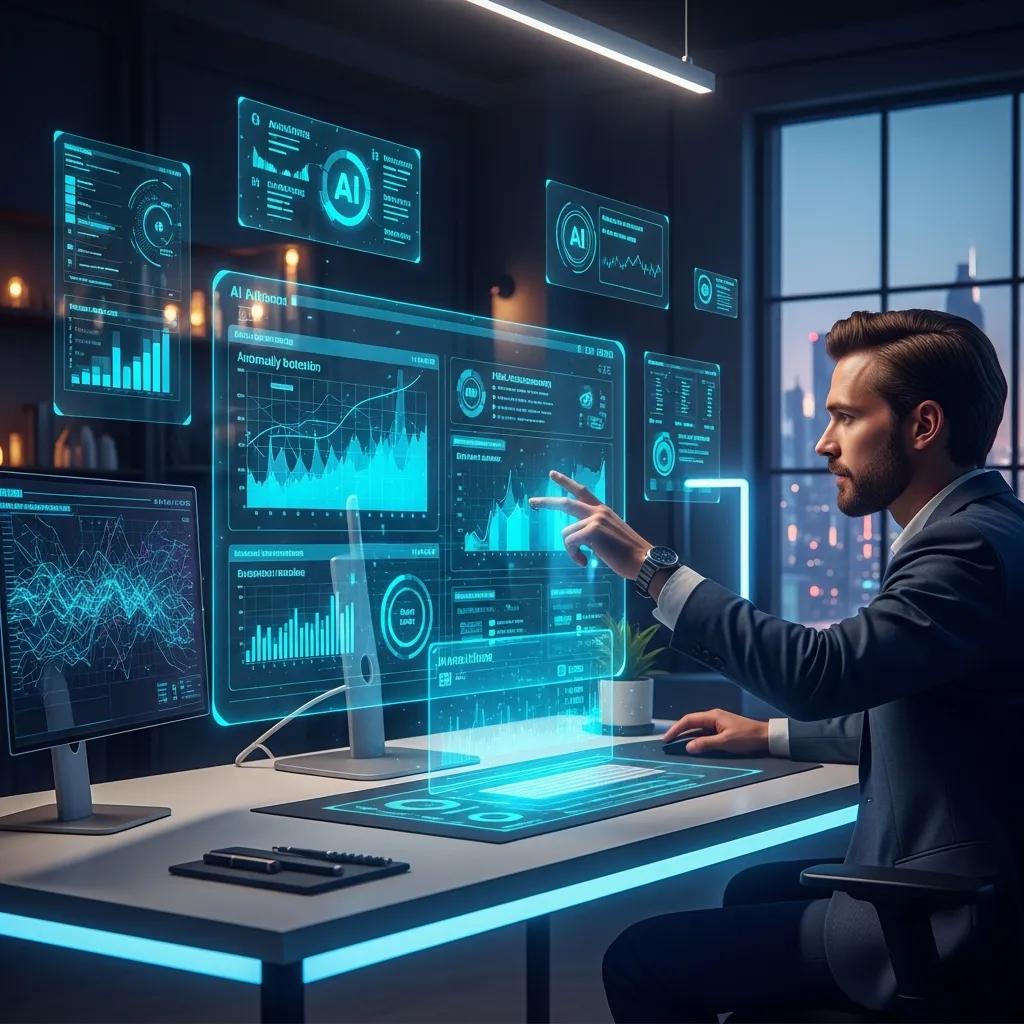
AI-powered auditing speeds evidence triage, uses NLP to extract relevant clauses, applies predictive risk scoring, and continuously monitors logs to spot anomalies before they become findings. These capabilities make evidence review faster, sampling more consistent, and help auditors focus on the highest-risk areas — improving both surveillance efficiency and recertification readiness. AI augments auditor judgement rather than replacing it: combined, they reduce manual work, reveal subtle trends across datasets, and support a proactive monitoring posture. The table below maps key AI capabilities to practical benefits for maintenance activities.
Adoption of AI in auditing is already improving accuracy, efficiency, and risk assessment in many sectors.
AI in Auditing: Enhancing ISO Compliance & Risk Assessment
The rise of AI in auditing is changing how audits are done — improving accuracy, efficiency, and anomaly detection. Technologies like machine learning, RPA, and NLP automate repetitive tasks, surface unusual patterns, and sharpen risk assessment so auditors can focus on strategic judgement.
| AI Capability | Attribute | Benefit |
|---|---|---|
| NLP Document Review | Automated extraction of clauses and evidence | Faster evidence collation and consistency |
| Predictive Risk Scoring | Historical trend analysis | Prioritizes high-risk processes for audit focus |
| Continuous Monitoring | Real-time log analysis | Early detection of anomalies and incidents |
| Audit Sampling Optimization | Statistical selection algorithms | Reduces time spent while increasing coverage |
With these capabilities, audit teams can focus on high-value work and reduce time spent on repetitive checks. Predictive insights also guide targeted internal audits and sharper management review agendas, improving improvement outcomes and proving control effectiveness.
In practice, AI screens large document sets and operational logs to surface the most relevant evidence and flag anomalies for human review. For example, automated log analysis that highlights repeated access failures in an ISMS directs auditors where controls may be weak and speeds remediation. That consistency shortens audit cycles and lessens business disruption.
Research is now examining how practical and impactful AI is for specialized audits such as ISO 27001.
AI for ISO 27001 Auditing: Feasibility & Impact
Recent studies explore the feasibility and potential benefits of using AI to support ISO 27001 consultancy and auditing, highlighting opportunities and practical challenges identified by subject-matter experts.
In What Ways Does AI Improve Surveillance Audits?
AI speeds surveillance by automating document triage, spotting trends in process performance, and flagging anomalies that need a human check. NLP extracts evidence from policies and records to build a searchable evidence set, while predictive models rank processes by likely nonconformity based on past data. That lets auditors spend more time on interviews and verification and less time sorting documents, improving both the speed and depth of surveillance. The outcome is more consistent sampling, fewer missed patterns, and earlier detection of issues that might otherwise escalate.
Organizations using AI typically save time on evidence collection and achieve higher-confidence sampling aligned with risk. Consistent evidence assessment reduces variability across audit cycles and builds a cumulative knowledge base to inform future surveillance and recertification planning. When surveillance is efficient, it becomes a proactive improvement tool rather than a reactive requirement.
How Can AI Streamline the Recertification Process?
AI helps recertification by running automated readiness checks, producing predictive gap analyses, and collating evidence across systems into a reviewer-ready dossier. Readiness scoring can check the presence and completeness of internal audits, CAPA records, and management review minutes, then generate a prioritized gap list. Automated collation preserves version control and traceability, while predictive analytics focus corrective effort on issues most likely to affect renewal.
An AI-assisted recertification workflow typically scans the management system, yields a readiness score and gap list, then assigns owners to collect evidence and verify closures. By cutting prep time and reducing surprises during the audit, AI lowers administrative overhead and makes recertification more predictable. To benefit most, align AI outputs with your internal audit and management review cycles so readiness is continuous rather than episodic.
Stratlane Certification is an accredited certification body operating in 27+ countries with professional auditors in 29+ countries. We certify ISO 9001:2015, ISO 14001:2015, ISO/IEC 27001:2022, and ISO 42001. Our core services include initial certification, surveillance and recertification audits, AI-driven audit tools, and a certificate database with downloads. We position ourselves as an innovative certification body that uses AI to improve efficiency and reduce cost. If you want to explore AI-enhanced audit services, Stratlane offers options to Get A Quote or Book your audit to see how AI can shorten audit timelines and improve evidence consistency.
What Are the Specific Maintenance Requirements for Major ISO Standards?
Each ISO standard emphasizes different maintenance priorities. ISO 9001:2015 focuses on process performance, objectives, and customer satisfaction; ISO/IEC 27001:2022 centers on ongoing risk assessment, control testing, and incident records; ISO 42001 targets governance and monitoring of AI systems and related risks. Know each standard’s focal points so you can tailor surveillance evidence and internal audits. The table below compares maintenance focus areas and key records to help implementers streamline workflows and align evidence collection.
| Standard | Maintenance Focus | Key Records |
|---|---|---|
| ISO 9001:2015 | Process performance, quality objectives, customer satisfaction | KPI dashboards, internal audit reports, customer feedback logs |
| ISO/IEC 27001:2022 | Risk assessment, control effectiveness, incident handling | Risk register, access logs, incident reports, control test results |
| ISO 42001 | AI governance, model monitoring, bias and safety controls | Model governance records, validation reports, monitoring logs |
While core maintenance activities apply across standards, each one needs targeted evidence and monitoring approaches. Tailor internal-audit checklists and management-review inputs to the standard in scope so auditors can quickly validate system effectiveness during surveillance or recertification.
For ISO 9001, emphasize measuring process KPIs, tracking nonconformities through CAPA, and monitoring supplier performance and objective achievement. Analyze customer feedback and feed it into improvement initiatives. Ensure management review minutes record decisions on quality objectives so the QMS demonstrates intended outcomes and evolves with business needs.
How to Maintain ISO 9001:2015 Quality Management System Certification?
To keep ISO 9001:2015, monitor process performance against quality objectives, run scheduled internal audits, and show corrective actions are effective. Practical steps include a documented internal-audit schedule, KPIs that show process stability, and records of supplier evaluations and customer-satisfaction analysis. Management review should cover objectives, audit outcomes, and resource needs, with minutes assigning owners for improvements. Showing trend data and closed CAPAs demonstrates the QMS is working and improving.
A practical checklist: documented objectives and KPIs, recent internal audit reports with closure evidence, supplier performance records, and customer feedback analysis. Keep these items accessible and version-controlled to reduce effort for surveillance and recertification audits and to show a genuine commitment to continual quality improvement.
What Are the Ongoing Compliance Steps for ISO/IEC 27001:2022 Information Security?
Maintaining ISO/IEC 27001:2022 requires continual risk assessment, control monitoring, incident response records, and staff awareness to demonstrate an effective ISMS. Auditors typically review the risk treatment plan, evidence of control operation (logs, access reviews), incident reports with lessons learned, and training completion records. Regular vulnerability scans, access reviews, and change-management records provide operational proof that controls work and risks are managed. Keep a live risk register and document periodic reviews of controls and treatments so the ISMS adapts to shifting threats and stays audit-ready.
Practical tips: align log-retention policies with audit needs, automate access-review schedules, and fold incident lessons into management-review actions. These steps make it easier to show control effectiveness and to respond quickly to surveillance sampling requests.
How Can Organizations Overcome Challenges in Maintaining ISO Certification?
Common challenges include limited resources, documentation drift, staff turnover, and keeping up with standard updates — all of which can threaten certification if not addressed. Mitigate these risks with practical tactics: adopt digital document control, automate monitoring where feasible, assign clear ownership for CAPA closure, and schedule regular training and handovers to preserve knowledge. AI-enabled tools and streamlined workflows reduce manual work and increase evidence consistency; bring in external support when internal capacity is tight. The section below lists common obstacles and concrete mitigation steps to turn problems into manageable projects.
The list below summarizes common obstacles and recommended mitigation tactics.
- Resource Constraints: Prioritize risk-based audits and automate evidence collection to reduce manual effort.
- Documentation Drift: Enforce version control and keep a single document repository with defined change procedures.
- CAPA Closure Delays: Track owners, deadlines, and verification steps in a CAPA register to ensure timely closure.
Acting early prevents small gaps from becoming nonconformities. Treat issues as tracked projects with accountable owners and verified closure to build momentum toward sustainable compliance.
What Common Obstacles Affect ISO Certification Maintenance?
Typical obstacles are limited time and budget for internal audits, outdated documents, inconsistent CAPA follow-through, and staff turnover that disrupts institutional knowledge. These problems increase the chance that evidence requested during surveillance or recertification will be incomplete or late, which can lead to findings or delays. Mitigations include a risk-based audit schedule to focus scarce resources, strict document control procedures, and a CAPA register with owners and deadlines. Cross-training and handovers reduce the impact of turnover by ensuring multiple people understand critical processes and records.
Digital tools for version control and evidence collation cut administrative overhead and help small teams meet audit demands. With concrete process changes and monitoring, organizations can stabilize maintenance practices and become more resilient to personnel and operational change.
How Does Stratlane Support Businesses in Sustaining Compliance?
Stratlane Certification helps organizations stay certified with audit services, AI-enabled audit tools, a global auditor network, and certificate-management features that simplify compliance work. Our offerings include initial certification, surveillance and recertification audits, AI-driven audit assistance, and a certificate database with download capability for fast verification. We tailor audit frequency and scope to your organizational risk and capacity. If you want tailored support, you can Get A Quote or Book your audit to explore how our AI-enabled processes can shorten timelines and improve evidence consistency.
Choosing a certification body that pairs experienced auditors with AI tools reduces admin work and can shorten audit timelines without sacrificing rigor. When internal resources are limited, engaging external partners is a practical way to keep certification healthy and make audits a force for improvement rather than disruption.
Where Can You Find Resources and Support for ISO Certification Maintenance?
Useful resources include certificate databases, audit and management-review templates, training programs for internal auditors and leaders, and digital tools for document control and continuous monitoring. Official ISO guidance and accreditation body materials provide the normative background, while practical templates and tools help teams operationalize requirements. The section below explains how to use certificate databases and recommends training and tooling that support continuous improvement. Searchable, practical resources reduce time to produce evidence during audits and make surveillance and recertification simpler.
| Resource | Purpose | Recommended Use |
|---|---|---|
| Internal Audit Training | Auditor competence and methodology | Quarterly upskilling and certification for internal auditors |
| Document Control Systems | Versioning and distribution | Central repository with role-based access |
| AI Audit Dashboards | Continuous monitoring and prioritization | Integrate with logs and evidence sources for anomaly detection |
| Awareness Training | Personnel security and process adherence | Annual refreshers aligned with management review outputs |
How to Use Stratlane’s Certificate Database and Download Services?
Stratlane’s certificate database lets clients verify certificate status and download official certificate files for records or third-party checks. Authorized users search by organization or certificate ID, review metadata to confirm scope and validity, and download a certified copy for filing or submission. If a certificate isn’t found, contact support to confirm account access or issuance details and request retrieval help. Use the database to check certificate validity and download files for audits, tenders, or customer requests to reduce administrative friction.
Store downloaded certificates in a controlled repository with clear naming and retention policies so you can produce proof quickly when asked. Keep metadata (issue date, expiry, scope) alongside files to support audit sampling and avoid last-minute searches during surveillance.
What Training and Tools Aid Continuous Improvement for ISO Compliance?
Effective training includes internal auditor courses, ISMS awareness sessions, and role-specific workshops that make responsibilities and evidence requirements clear. Tools that support maintenance include document control systems, CAPA tracking software, performance dashboards, and AI-assisted audit tools that automate evidence collation and monitoring. Pair training refreshers with management-review cycles so lessons from audits convert into updated practices. Pick tools that integrate with your systems and provide audit trails for changes and access to improve transparency and reduce evidence-assembly work.
Combining focused training with automation and monitoring reduces human error, speeds corrective actions, and embeds compliance into day-to-day operations. Review tool effectiveness and training outcomes in management review to close the feedback loop essential for continuous improvement.
Frequently Asked Questions
What are the consequences of losing ISO certification?
Loss of certification can damage customer trust, limit market opportunities, and complicate contract eligibility where certification is required. It may trigger extra scrutiny from regulators and require costly re-audits to regain status. Maintaining certification protects operational credibility and market reputation.
How often should internal audits be conducted for ISO compliance?
At minimum, conduct internal audits annually. Frequency should be risk-based: higher-risk or problem areas need more frequent reviews. Regular audits catch weaknesses early, verify corrective actions, and keep the management system effective and audit-ready.
What role does employee training play in maintaining ISO certification?
Training is essential. It ensures staff know their roles, understand procedures, and can produce the evidence auditors request. Regular training builds a compliance-aware culture, improves audit performance, and supports faster, more reliable corrective actions.
How can organizations effectively manage documentation for ISO compliance?
Use a centralized document control system that enforces versioning, approvals, and distribution rules. Define clear procedures for document creation, review, and change control, and train staff on these processes. Regular checks of document practices prevent drift and make audits easier.
What are the best practices for preparing for a surveillance audit?
Keep a rolling evidence pack with recent internal audit reports, management review minutes, and performance metrics. Do a pre-audit readiness check to find gaps, ensure previous CAPAs are closed and documented, and run mock interviews to prepare staff. These steps reduce surprises and smooth the audit.
How can AI tools assist in the ISO certification maintenance process?
AI automates document triage, evidence collection, and risk assessment, and it analyzes large datasets to reveal trends and anomalies. AI can produce readiness scores and prioritized gap lists, cutting manual work and improving the accuracy and speed of surveillance and recertification preparation.
What should organizations do if they face challenges in maintaining ISO certification?
Start with a root-cause assessment. Adopt digital tools for document control, automate monitoring where possible, and assign clear ownership for CAPA. Schedule regular training and handovers to protect knowledge. When internal capacity is limited, bring in external consultants or a certification body for targeted support.
Conclusion
Maintaining ISO certification protects operational integrity and market access. With disciplined practices — regular internal audits, strong CAPA management, disciplined document control — and by using AI where it helps, organizations can reduce audit risk and make continuous improvement part of daily work. These approaches cut admin overhead, improve readiness for surveillance and recertification, and keep your certificate working for the business. Explore our resources and services to support your ongoing compliance journey.